Exact2Pass

Last Update 8 hours ago Total Questions : 384
The HashiCorp Certified: Terraform Associate (004) (HCTA0-004) content is now fully updated, with all current exam questions added 8 hours ago. Deciding to include Terraform-Associate-004 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our Terraform-Associate-004 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these Terraform-Associate-004 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any HashiCorp Certified: Terraform Associate (004) (HCTA0-004) practice test comfortably within the allotted time.
Your team often uses API calls to create and manage cloud infrastructure. In what ways does Terraform differ from conventional infrastructure management approaches?
You corrected a typo in a resource name, changing it from aws_s3_bucket.photoes to aws_s3_bucket.photos. You want to update the Terraform state so that the existing resource is recognized under the new name, without destroying and recreating it. Which configuration should you use?
You are responsible for a set of infrastructure that is managed by two workspaces: example-network and example-compute. The example-compute workspace uses data from output values configured in the example-network workspace and must be deployed afterward. Currently, this is a manual process:
An operator deploys changes to the example-network workspace.
They manually copy the output values from the example-network workspace to input variables configured for the example-compute workspace.
They deploy the example-compute workspace.
Which HCP Terraform features can you use to automate this process?
Pick the two correct responses below.
Which parameters does terraform import require? Choose two correct answers.
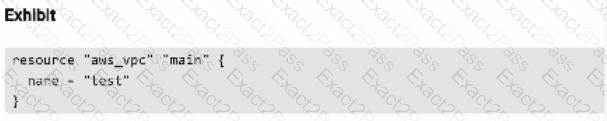
A resource block is shown in the Exhibit space of this page. What is the provider for this resource?
Terraform stores the value of an output in its state file, even if the sensitive argument is set to true.
Which of the following does terraform apply change after you approve the execution plan? (Choose two.)
The_________determines how Terraform creates, updates, or delete resources.
Exhibit:
provider " aws " { region = " us-east-1 " }
provider " aws " { region = " us-west-2 " }
You need to deploy resources into two different AWS regions in the same Terraform configuration using the provider blocks shown in the exhibit. What do you need to add to the provider configuration to deploy a resource to the us-west-2 AWS region?
You want to use API tokens and other secrets within your team ' s Terraform workspaces. Where does HashiCorp recommend you store these sensitive values?
(Pick 3 correct responses)

