Exact2Pass

Last Update 1 hour ago Total Questions : 75
The HPE Network Security Expert Written Exam content is now fully updated, with all current exam questions added 1 hour ago. Deciding to include HPE7-A10 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our HPE7-A10 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these HPE7-A10 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any HPE Network Security Expert Written Exam practice test comfortably within the allotted time.
Refer to the exhibit.
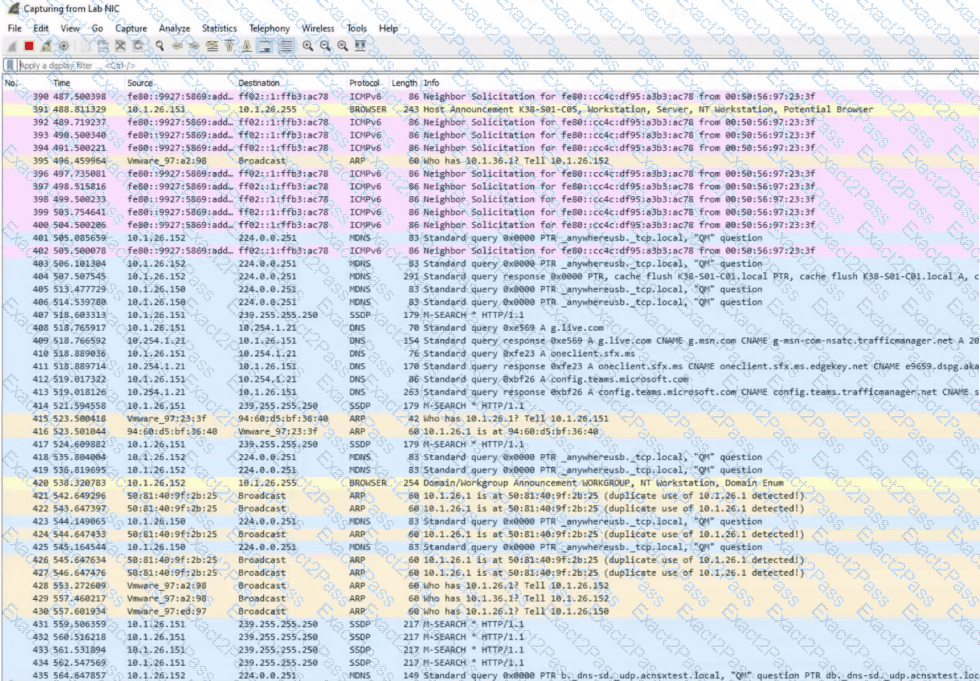
Frame 421: 50:81:40:9f:2b:25 - > Broadcast ARP 60 10.1.26.1 is at 50:81:40:9f:2b:25 (duplicate use of 10.1.26.1 detected!)
Frame 422: 50:81:40:9f:2b:25 - > Broadcast ARP 60 10.1.26.1 is at 50:81:40:9f:2b:25 (duplicate use of 10.1.26.1 detected!)
Frame 424: 50:81:40:9f:2b:25 - > Broadcast ARP 60 10.1.26.1 is at 50:81:40:9f:2b:25 (duplicate use of 10.1.26.1 detected!)
Which device should be documented as potentially malicious and requiring further investigation?
A company has HPE Aruba Networking gateways and plans to begin implementing gateway IDS/IPS. The customer has chosen Block as the Fail Strategy.
What could you recommend to help reduce unexpected outages caused by this particular fail strategy?
A company wants its AOS-CX switches to obtain certificates from ClearPass Onboard and use those certificates to implement RadSec with ClearPass Policy Manager (CPPM).
ClearPass Onboard has a CA with EST enabled and this EST URL: `[https://cp1.acnsxtest.com/.well-known/est/ca:2](https://cp1.acnsxtest.com/.well-known/est/ca:2)`
ClearPass Guest has an account whose username is `switchcorp123`. (Assume CPPM also has a valid service to authenticate users who access the EST application.)
CPPM has a network-device account for the switches with RadSec enabled. The RadSec settings validate by CN or SAN using this regex: `switchcorp123`
ClearPass has these certificates:
* HTTPS certificate signed by DigiCert
* RadSec certificate signed by DigiCert
* RADIUS/EAP certificate signed by MyDomainCA
This configuration is on the AOS-CX switches:
```text
crypto pki est-profile est1
url https://clearpass1.acnsxtest.com/.well-known/est/ca:2
username switchcorp123
password plaintext %FY212h & zaTk
vrf default
exit
crypto pki certificate cert1
subject switchcorp123
enroll est-profile onboard
crypto pki application radsec-client certificate cert1
```
The switches’ TA-profile list includes DigiCert.
Assume you have obtained the correct password associated with the indicated username. What error or errors are present?
Your company uses an HPE Aruba Networking AOS-10 architecture managed by HPE Aruba Networking Central. A ClearPass Policy Manager (CPPM) cluster supplies authentication. The company also has a Palo Alto firewall. You want to configure the HPE Aruba Networking infrastructure to quarantine clients for which the firewall sends Syslog Threat messages to CPPM.
Network infrastructure devices already have a “quarantine” role configured.
You checked the CPPM event dictionary and found an entry for Palo Alto Syslog Threats that includes:
Prefix: PANW-Threat
Attributes such as syslogtimestamp and logtype
What is a correct component of the configuration in ClearPass server settings?
A company uses an HPE Aruba Networking AOS-10 mobility infrastructure. Network administrators recently enabled wireless detection on the APs, which checks for all infrastructure and client threats. However, the administrators quickly became overwhelmed and now want to disable most checks.
They want a recommendation for the checks most likely to indicate genuine threats.
Which one should be mentioned?
An organization wants an AOS-CX switch to generate an alert when its RADIUS server (cp.acnsxtest.local) rejects an abnormal number of client authentication requests each hour. After discussing this with other HPE Aruba Networking administrators, you still do not know how many rejections should be considered normal or abnormal. You expect this value may vary for every switch.
You are assisting the developer with developing an NAE script for this use case.
Refer to the scenario.
You are helping a customer define an NAE script for AOS-CX switches. The script will monitor statistics from a RADIUS server configured on the switch. To future-proof the script, you want administrators to be able to choose a different hostname or IP address for the monitored RADIUS server when they create an agent from the script.
What should you recommend?
A client connects to an AOS-CX switch that tunnels the client’s traffic to an AOS-10 gateway. The gateway places the client in a role with these rules:
any any svc-dhcp permit
user alias host1 svc-dns permit
user alias net1 svc-https permit
user alias net2 tcp 8086 permit
user alias net3 any deny
user alias net4 svc-https permit
The gateway defines these aliases:
host1 = 10.0.6.8
net1 = 10.0.0.0 255.255.252.0
net2 = 10.0.3.0 255.255.255.0
net3 = 10.0.0.0 255.255.248.0
net4 = 10.0.0.0 255.255.0.0
The client sends these two packets:
1: tcp 8086 to 10.0.3.75
2: https to 10.0.7.24
What occurs?
Refer to the exhibit.
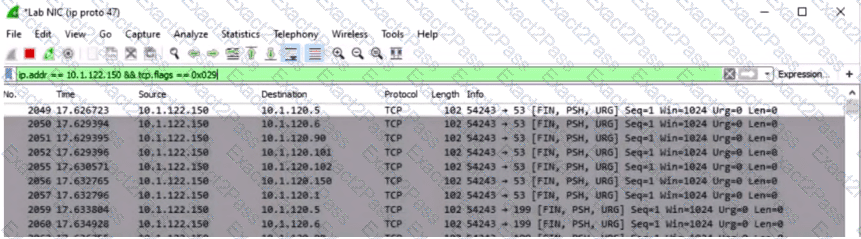
Packet trace display:
Source: 10.1.122.150 - > Destination: 10.1.120.5 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0
Source: 10.1.122.150 - > Destination: 10.1.120.6 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0
Source: 10.1.122.150 - > Destination: 10.1.120.90 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0
Source: 10.1.122.150 - > Destination: 10.1.120.101 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win= 1024 Urg=0 Len=0
Source: 10.1.122.150 - > Destination: 10.1.120.5 TCP 54243 - > 199 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0
What does this indicate?
Introduction to the customer
You are assisting a company with adding HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking network-infrastructure devices.
The company already has a Windows domain and Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers.
ClearPass cluster IP addressing and hostnames
Publisher = 10.47.47.5
Subscriber 1 = 10.47.47.6
Subscriber 2 = 10.47.47.7
Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
Refer to the scenario.
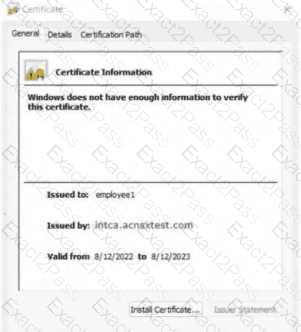
Assume that you configured CPPM to assign HPE Aruba Networking ClearPass roles and AOS user roles as indicated in the scenario. However, a penetration tester was able to access the network with medical-staff privileges on a client with a valid computer certificate but a revoked medical user certificate. In this situation, the customer wants the client to receive computer-only access.
What can you do to resolve this issue while continuing to meet the other customer requirements?
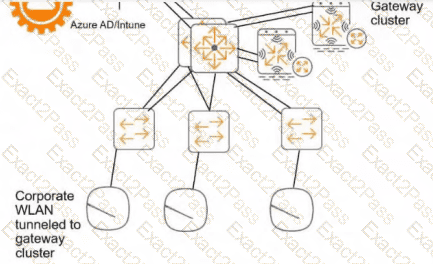
A customer has an AOS-10 architecture managed by HPE Aruba Networking Central. HPE Aruba Networking infrastructure devices authenticate clients against an HPE Aruba Networking ClearPass cluster.
In HPE Aruba Networking Central, you are reviewing network traffic flows for a wireless IoT device categorized as a “Raspberry Pi” client. You observe SSH traffic. You then review several additional wireless IoT clients and find that they are also sending SSH.
Refer to the scenario.
You are assisting the customer in assessing ways to mitigate the potential threat detected. For the foreseeable future, until the security team has addressed the threat, the company wants to block most traffic from any IoT client detected sending SSH traffic. The company does want to allow limited access for these clients so that administrators can remediate them remotely.
What action should you take?

