Exact2Pass
The global enterprise cyber defense and security operations landscape in 2026 demands proactive threat vector containment, multi-layered perimeter governance, and rapid incident mitigation protocols. As organizations expand distributed infrastructures across multi-cloud environments, containerized microservices, and remote endpoint nodes, defensive teams must transition away from basic passive monitoring toward adaptive, intelligence-driven protection frameworks. Earning the EC-Council Certified Network Defender (CND) credential validates your comprehensive capacity to build resilient defense-in-depth postures, configure stateful detection systems, and safeguard physical and virtual assets. However, many network administrators, security analysts, and systems support specialists fail on this intensive 4-hour, 100-question evaluation because they rely on superficial preparation habits. Relying on flat answer keys or context-stripped question repositories found on unverified public forums cannot prepare you for the intricate situational logic of evaluating packet-level anomaly traces or resolving firewall rule order conflicts under active production workloads.
True success on the official 312-38 examination requires a thorough, practical command of the full security lifecycle—spanning the Protect, Detect, Respond, and Predict operational methodology. Defensive engineers must maintain sharp diagnostic judgment when configuring network segmentation boundaries, tuning Intrusion Detection and Prevention Systems (IDS/IPS), establishing identity access governance, and managing Endpoint Detection and Response (EDR) telemetry streams. Candidates frequently spend several months searching for high-yield eccouncil 312-38 exam questions online, hoping to locate an updated certified network defender 312-38 study guide to evaluate their operational fluency, or reviewing log analyzer parameters to verify their SIEM event correlation rules. Without interactive workspace software, a structured network defense course, or targeted practical practice that can provide actual help in exam preparation, passive reading fails to build the diagnostic capabilities needed to handle attack surface vulnerabilities or isolate encrypted malware payloads within the enterprise network.
At Exact2Pass, we replace passive reading with active, scenario-driven structural engineering exercises designed to build true platform confidence. Our premium preparation workspace simulates the functional operational layers, terminal diagnostic views, and threat analysis consoles of the active network security ecosystem. We guide you through executing gap analyses on legacy perimeter configurations, analyzing packet capture files using Wireshark, configuring User and Entity Behavior Analytics (UEBA), and deploying automated incident response playbooks. This targeted practice builds the exact threat-hunting judgment and system deployment skills demanded by leading enterprise security operations centers, ensuring you pass your proctored assessment on your very first try.
The 312-38 certification exam is engineered to evaluate your end-to-end network protection, traffic monitoring, and incident mitigation capabilities across modern enterprise parameters, combining multi-scenario case analysis with complex multiple-choice items. Our realistic simulation platform replicates active firewall management consoles, SIEM log analysis dashboards, and real-time threat intelligence tracking displays instead of serving up generic multiple-choice questionnaires. You will master the underlying network protocol behavior, operator-driven security controls, and infrastructure-level dependencies of the active security framework, preparing you to tackle any scenario-based defense question with ease.
Timothy works as a network administrator in a multinational organization. He decides to implement a dedicated network for sharing storage resources. He uses a_______as it seperates the storage units from the
servers and the user network.
Which of the following indicators are discovered through an attacker ' s intent, their end goal or purpose, and a series of actions that they must take before being able to successfully launch an attack?
A popular e-commerce company has recently received a lot of complaints from its customers. Most
of the complaints are about the customers being redirected to some other website when trying to
access the e-com site, leading to all their systems being compromised and corrupted. Upon
investigation, the network admin of the firm discovered that some adversary had manipulated the
company’s IP address in the domain name server’s cache. What is such an attack called?
John has been working a* a network administrator at an IT company. He wants to prevent misuse of accounts by unauthorized users. He wants to ensure that no accounts have empty passwords. Which of the following commands does John use to list all the accounts with an empty password?
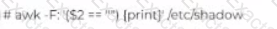
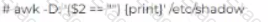

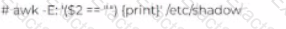
Malone is finishing up his incident handling plan for IT before giving it to his boss for review. He is outlining the incident response methodology and the steps that are involved. What is the last step he should list?
Which event type indicates a significant problem such as loss of data or loss of functionality?
Which firewall technology can filler application-specific commands such as CET and POST requests?
Which of the following refers to a potential occurrence of an undesired event that can eventually damage and interrupt the operational and functional activities of an organization?
If Myron, head of network defense at Cyberdyne, wants to change the default password policy settings on the company’s Linux systems, which directory should he access?
Which of the following is an example of MAC model?