Exact2Pass
The web application security landscape in 2026 demands highly specialized cloud and perimeter defense competencies, particularly as enterprises transition legacy architectures to containerized microservices. Achieving the status of a Fortinet Certified Professional (FCP) in Cloud Security by passing the FortiWeb 8.0 Administrator exam validates your ability to configure, manage, and troubleshoot advanced Web Application Firewall (WAF) systems. However, many network security engineers and system administrators struggle on this intensive, 75-minute technical evaluation by treating it as a simple product memorization drill. Relying on flat, context-stripped answer registries or linear question tables found on unverified communication forums cannot prepare you for the complex situational logic of active policy deployment, real-server pools, and certificate offloading under live network conditions.
True success on this exam requires a holistic understanding of FortiWeb’s operational modes, spanning inline transparent active bypass, true reverse-proxy setups, and offline sniffing architectures. Security professionals must understand how FortiWeb processes and sanitizes HTTP/HTTPS headers, executes deep packet inspection, and manages dynamic content routing policies. Candidates frequently spend several months searching for high-yield nse5_fwb_ad-8.0 exam questions online, hoping to locate a comprehensive study guide, or seeking out structured training resources that can assist with system validation. Without interactive practice that lets you configure server objects, analyze security profiles, and evaluate high-availability multi-node clustering schemas, dry theoretical reading will fail to develop the high-level diagnostic skills required to clear the strict passing thresholds of the actual testing terminal.
At Exact2Pass, we replace passive reading with active, scenario-driven deployment exercises designed to build true platform confidence. Our premium preparation workspace simulates the functional layers and configuration states of FortiWeb 8.0, preparing you to make critical decisions regarding signature exclusions, threat classifications, and TLS key management. We guide you through configuring API protection schemas, managing bot detection parameters, and setting up secure LDAP or SAML authentication paths. This targeted practice develops the deep conceptual judgment needed by elite network security teams, ensuring you pass on your very first try.
The NSE5_FWB_AD-8.0 evaluation is designed to assess your end-to-end WAF administration capabilities, from initial physical integration to post-deployment log telemetry analysis and troubleshooting. Our realistic simulation platform replicates active FortiWeb console behaviors and traffic processing patterns instead of serving up generic multi-choice questionnaires. You will master the underlying database integrations, policy-based routing structures, and service-level dependencies of the active FortiWeb 8.0 ecosystem, preparing you to tackle any scenario-based configuration question with ease.
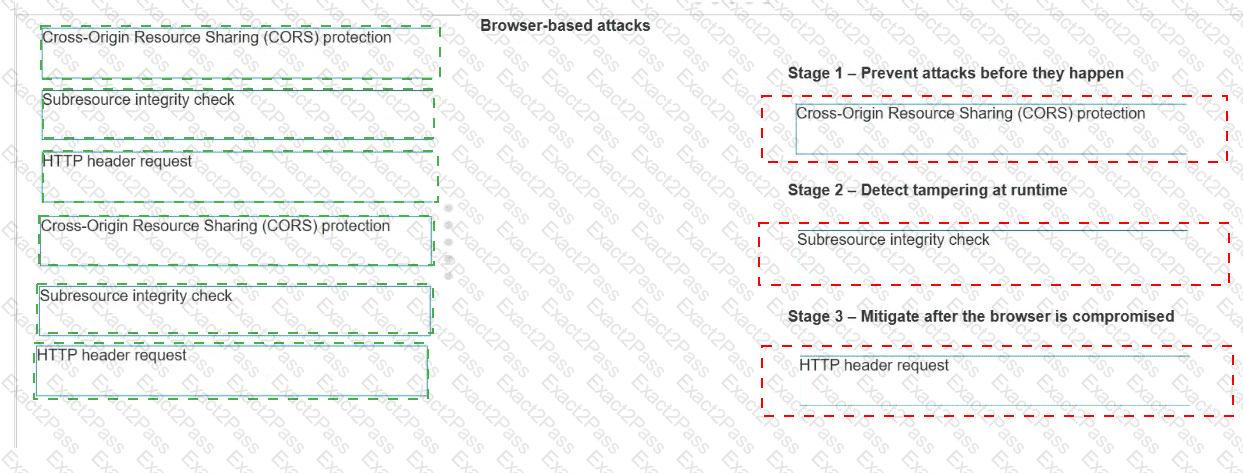
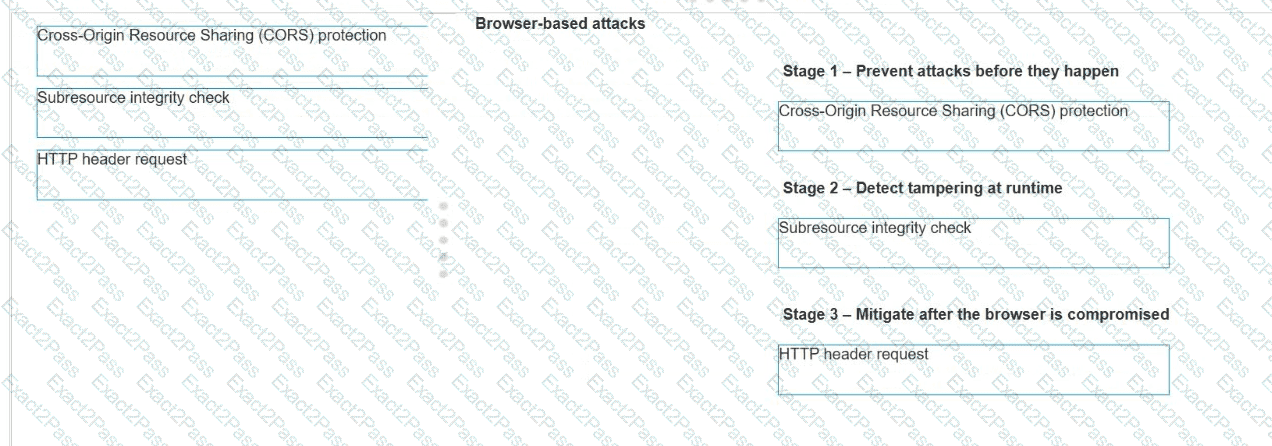
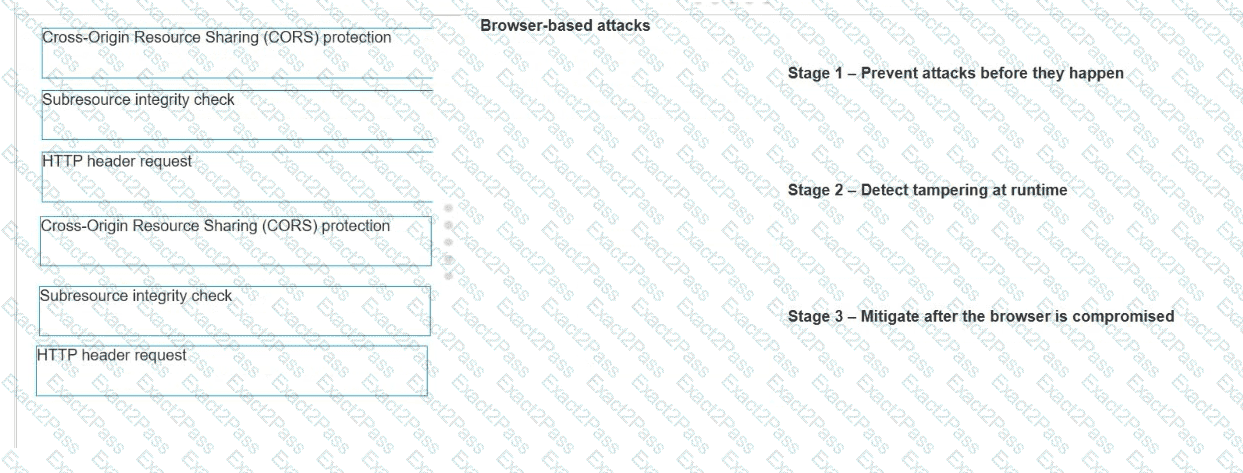
You are configuring the FortiWeb client-side protection feature to defend against browser-based attacks.
Based on the layered defense strategy, drag and drop each control to the corresponding stage of defense.
You are setting up a FortiWeb policy to protect a customer login portal. Users connect to https://login.training.lab, and you want FortiWeb to forward those requests to a load-balanced pool of back-end servers.
Which three components must you configure to complete the server policy?
While reviewing FortiWeb logs, you notice a suspicious login request that failed authentication. You suspect it may be part of an injection attack targeting the login form.
Which input pattern is an example of a typical SQL injection attempt that could bypass authentication checks?
A FortiWeb administrator needs to allow a known web indexer to scan the website for search engine visibility.
What is the easiest way to allow this on FortiWeb?
You recently deployed two FortiWeb devices in an active-active (A-A) high availability (HA) cluster.
During routine maintenance, you want to confirm that the cluster is synchronizing the correct configuration areas and that both FortiWeb devices behave consistently in production.
As the FortiWeb administrator, which two configuration areas should you examine to verify that HA synchronization is functioning correctly? (Choose two.)
Refer to the exhibits.
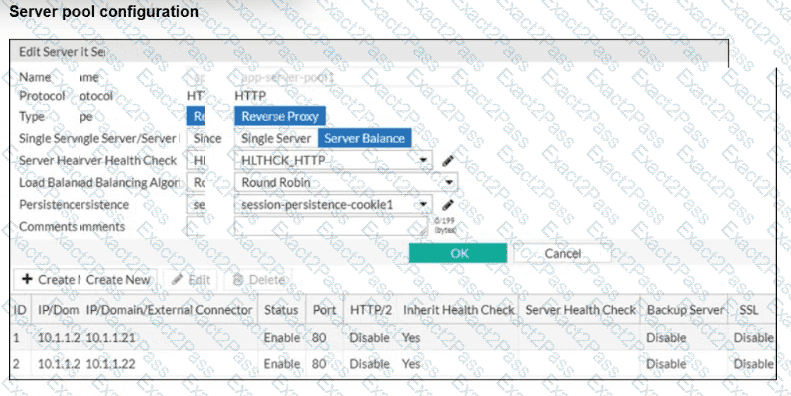
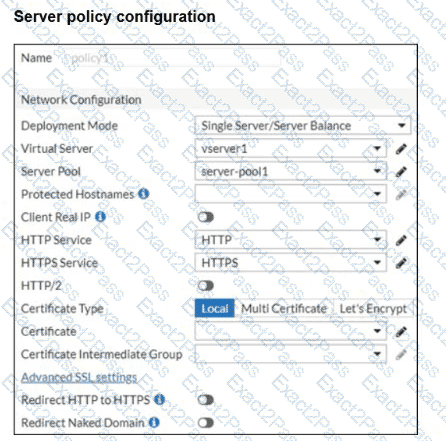
You are configuring a FortiWeb device in reverse proxy mode, placed downstream from a FortiGate. The server pool includes two back-end web servers: 10.1.1.21 and 10.1.1.22, and you’ve defined a health check policy.
After completing the server policy configuration and applying it to a virtual server, you notice that FortiWeb is not forwarding traffic to the back-end servers. No errors or health check failures appear in the logs.
Based on the configuration shown in the exhibit, which change should you make to restore back-end traffic flow?
A large enterprise has an existing web infrastructure with complex routing rules and static IP address assignments. The network administrators cannot modify the current IP address scheme, but they need FortiWeb to inspect and block threats like SQL injection and cross-site scripting (XSS) without changing the client-server communication flow.
In this situation, which FortiWeb operation mode is the most suitable?
A FortiWeb administrator sees the following request:
GET /api/v1/data HTTP/1.1
Host: example.com
Authorization: ApiKey abc123def456
The API key belongs to a user in group B who is authorized to access only /api/v1/reports.
What should the administrator do to prevent this unauthorized access?
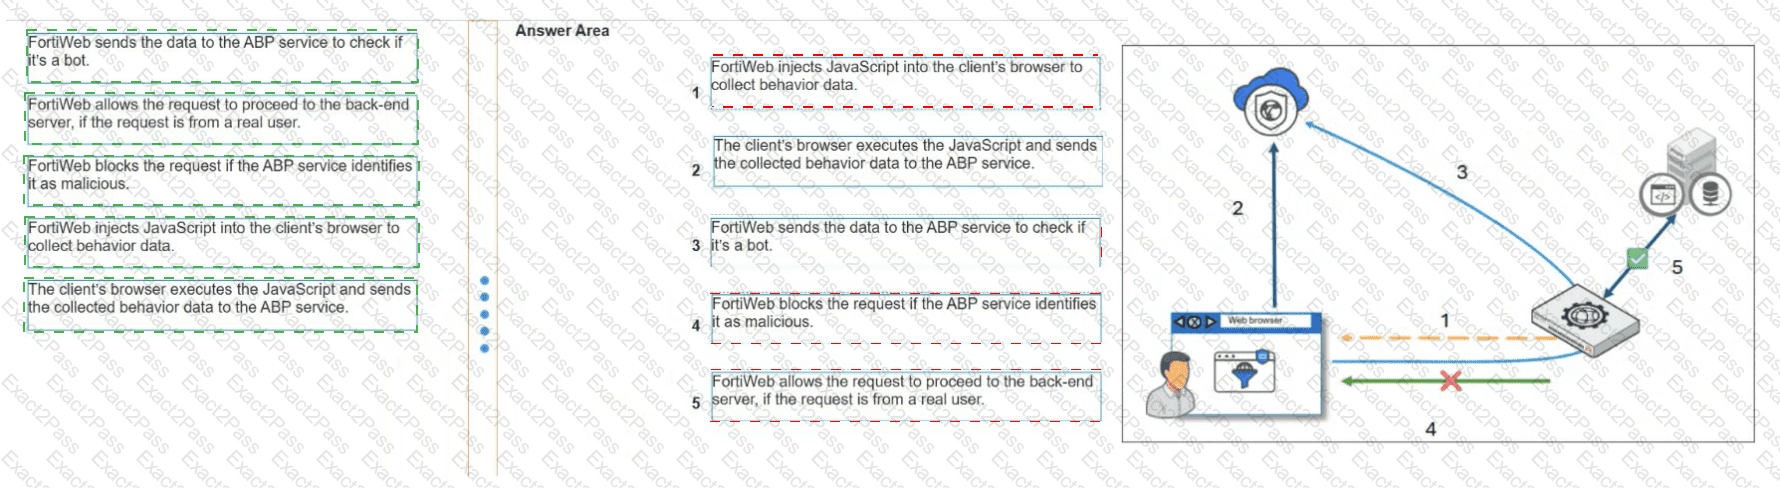
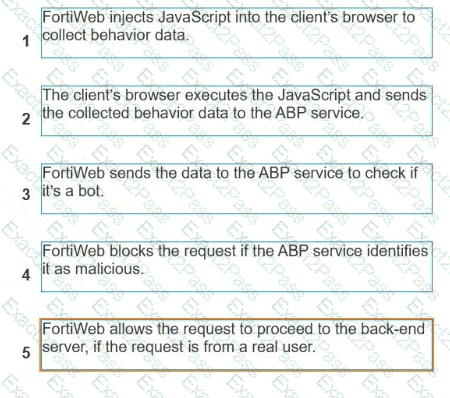
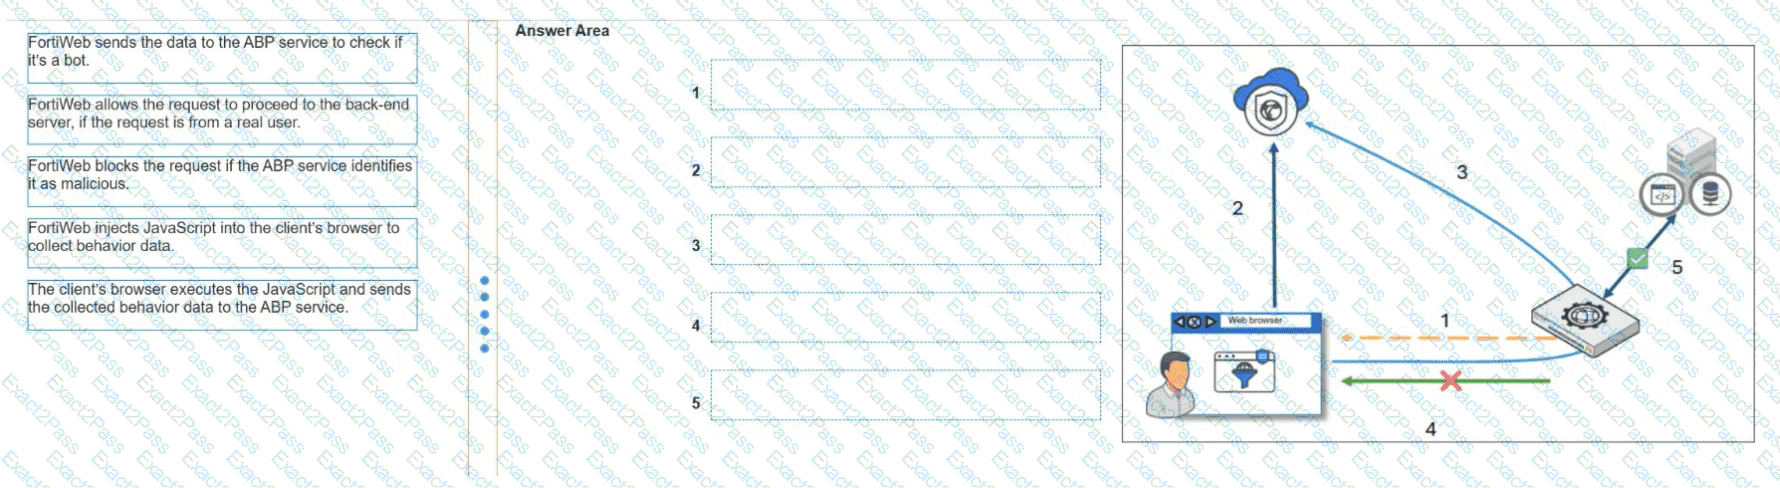
You are reviewing the FortiWeb integration with the Advanced Bot Protection (ABP) service.
Match each step in the ABP flow with its description.
Which situation best explains when a FortiWeb administrator should enable automatic HTTP-to-HTTPS redirection?