Ticking Clock Black Friday Special: 75% Off! Apply coupon code below to save on all exam bundles! - Ends in 0d 00h 00m 00s - Coupon code: 75epass

Exact2Pass Menu

CyberArk Guardian Exam

Last Update 5 hours ago Total Questions : 60

The CyberArk Guardian Exam content is now fully updated, with all current exam questions added 5 hours ago. Deciding to include GUARD practice exam questions in your study plan goes far beyond basic test preparation.

You'll find that our GUARD exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these GUARD sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any CyberArk Guardian Exam practice test comfortably within the allotted time.

Question # 1

You need to implement a solution that requires users to verify they have run an application.

Which solution is best?

A.

EPM Step-up authentication.

B.

Accounts with Least Privilege configured.

C.

Ad Hoc Access and Ad Hoc Connections.

D.

PTA Risky Commands.

Question # 2

What type of attack can CyberArk mitigate?

A.

Pass-the-Hash

B.

SQL Injection

C.

DDOS

D.

Phishing

Question # 3

Which components are required to configure external recording storage for PSM?

A.

SMB 3.0 supported storage, A Windows Privileged Account, Storage-level Tampering Protection.

B.

SMB 3.1 supported storage, A Domain Administrator Account, Storage-level Tampering Protection.

C.

NAS Storage, a private SSH Key, Azure Key Vault.

D.

SAN Storage, AWS Access Key, AWS KMS.

Question # 4

In most cases, why should a failed CPM verification followed by a reconciliation action be considered a security incident?

A.

The secret may have been changed outside of CyberArk and is compromised.

B.

The secret is not configured for automatic reconciliation.

C.

The CPM should not be performing automatic reconciliation actions.

D.

The secret was rotated outside of an approved change-control window.

Question # 5

ClientABC is moving into the DevOps space. They currently use CCP and are considering Conjur. They have noticed there is considerable overlap.

How would you explain the difference between the two?

Choose two

A.

Conjur is well suited for the velocity of the CI/CD pipeline because it includes native authentication such as API keys, 1AM, and OAuth. You store the secret at the project folder level.

B.

CCP is a good choice if you're using client certificate authentication. With CCP you need to authenticate and pass an application ID and your query for your secret.

C.

Conjur is best suited for static secrets. You only need to pass an API key to make the call. This is suited well for the velocity of the CI/CD pipeline because it integrates seamlessly with containers.

D.

CCP is best used for ad-hoc scripts. It's a great choice because you're able to use enhanced authentication mechanisms such as 'Path' and 'Hash'.

E.

When trying to decide between the two, you should generally choose CCP, as Conjur cannot be integrated with the same vault that is used for CyberArk PAM.

Question # 6

You want to be notified when a password is used. You configured NFNotifyOnPasswordUsed in the platform's Notification parameters.

Which two use cases result in the notification being sent?

Choose two

A.

When a user copies the password from the PVWA Ul.

B.

When the credential is first onboarded and assigned to the platform.

C.

When a user clicks 'Verify' to verify the password via the PVWA Ul.

D.

When user connects using PSM for SSH.

E.

When user logs on and clicks connect from the PVWA Ul.

Question # 7

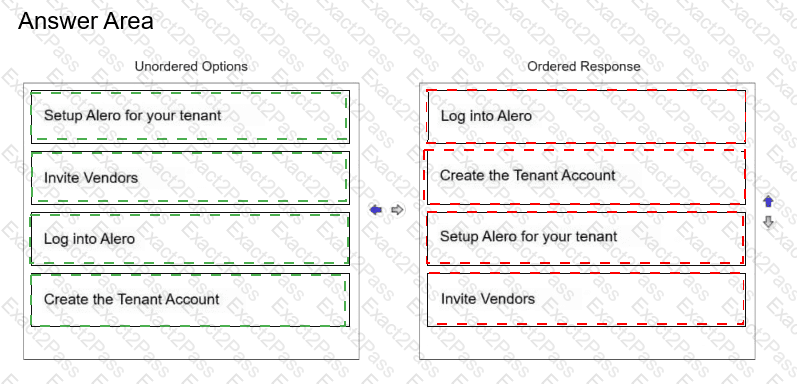
Place the steps for creating a new Alero tenant in the correct sequence.

Drag & Drop
Question # 8

When Dual Control is enabled for a platform in the Master Policy, exceptions may be configured in the following two locations.

Choose two

A.

Exceptions can be configured in the safe permissions for specific users or groups.

B.

Exceptions can be configured in the object level of individual vaulted accounts associated with that platform.

C.

Exceptions can be configured for PSM connectivity at the platform level.

D.

Exceptions can be configured for specific users or groups at the master policy level.

E.

Exceptions can be configured in vault level permissions for specific users and groups.

Question # 9

What is required for a Privilege Cloud Connector Server?

A.

Public Facing IP

B.

IIS Server 10

C.

IPv6 Address

D.

Joined to the domain

Question # 10

At which stage is it appropriate to incorporate the C3 Alliance integrations?

A.

Since we already have integrations available and little development is required, they should all be completed in Stage 1.

B.

Integrate the security tools in Stage 1 and other tools such as RPA in Stage 2.

C.

They are less of a risk, so we should leave them until Stage 3 and focus on other privileged accounts first.

D.

They should all be integrated prior to the actual ’go-live' of CyberArk PAM.

Go to page: