Exact2Pass

We have coached hundreds of corporate health and safety managers, compliance officers, risk managers, and independent management systems consultants through this intensive PECB global milestone. Let's look honestly at the modern international compliance and regulatory auditing landscape. The safety professionals who fall short on this rigorous, 180-minute professional-tier evaluation are almost always those who leaned heavily on low-quality, linear test sheets—those flat, context-stripped answer repositories floating around unverified business forums. Those static, unverified materials simply cannot prepare you for live audit evidence collection or the intricate root-cause evaluations tested on the real exam. Candidates frequently spend months looking for high-yield iso 45001 lead auditor exam questions online, trying to source realistic pecb certified ohsms expert tests to measure their analytical capability, or tracking down an updated iso-45001-lead-auditor study guide that breaks down Clause 8 operational controls. They quickly discover that rote memorization fails completely when faced with complex, scenario-based worker consultation gaps and unexpected regulatory non-compliance issues during field verification trails.
At Exact2Pass, our framework targets the underlying structural logic, the ISO 19011 auditing guidelines, and the plan-do-check-act (PDCA) lifecycle of the active ISO 45001:2018 standard instead. Our premium preparation platform delivers comprehensive regulatory and methodology breakdowns for every evidence-gathering track and opening meeting scenario. You will master actual production-grade core compliance verification patterns instead of leaning on short-sighted memorization shortcuts. We map out hazard identification matrices, worker participation enforcement rules, legal registries verification, and audit program risk-based management parameters step by step. Our learning material is designed from the ground up by active, certified principal OHSMS lead auditors who direct and execute enterprise-scale safety audits daily across heavy industrial sectors. Because of that, we completely avoid mindless, repetitive question repositories. Instead, our software acts as an active administrative simulation that forces you to evaluate audit notes, resolve conflicting stakeholder testimonials, and classify non-conformities like a veteran lead auditor. You will learn the exact reason why a specific piece of audit evidence or corrective action plan succeeds or fails to meet international registration standards. That is how you build real confidence before logging into your official PECB account to launch your proctored evaluation workspace. Our adaptive simulation tools develop deep, practical environment judgment that transfers perfectly to enterprise risk environments, helping you pass on your very first try.
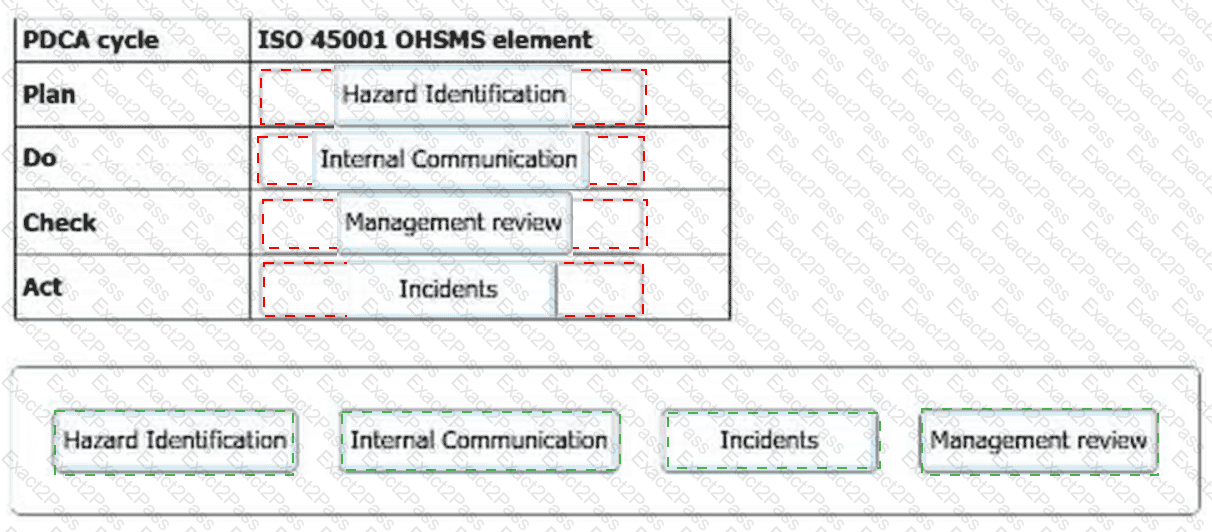
Plan-Do-Check-Act (PDCA) provides a framework for continually improving an OHSMS in accordance with ISO 45001.
Match each OHSMS element with the relevant stage in the PDCA cycle.
An audit team leader who has been contracted to perform a full Occupational Health and Safety management system audit is conducting a documented information review in preparation for the audit.
Which four options are a benefit of completing this task?
Which one of the following options is the definition of an interested party?
You are conducting a Stage 2 certification audit to ISO 45001 at an adventure park in the Scottish Highlands. The park offers treetop walks, zip-line rides, walking trails, and horse-riding trips. The park is open to adults and children of any age. You are particularly interested in compliance with legal requirements and interview the Park Manager.
You: How do you evaluate the risks to participants that the various activities present?
Park Manager: Our risks are covered by insurance, and we operate under health and safety legislation that requires frequent checks of all our facilities. For example, we trust staff to check all our harnesses every morning.
You: Are you required to have an independent inspection carried out of zip lines, for example?
Park Manager: Yes, our insurance company employs a reputable body to do that sort of thing.
You: Can you show me a copy of the latest inspection report? Park Manager: I’d need to get that from the insurance organisation. I have the initial one when we opened eight years ago.
You examine the inspection report, which takes the form of a checklist that does not identify individual zip lines, treetop platforms, harnesses, or rope ladders. It is dated eight years previously and has a scribbled signature with no other identification of the inspection engineer. Select the two statements for which there is evidence of a nonconformity to ISO 45001.
Select two statements.
When conducting an ISO 45001 audit and while reviewing a report of a recent emergency preparedness and response exercise, you note that the organisation has determined that it needs to make some changes to its OHSMS in order to improve OH and S performance.
Which three of the following statements about the management of change are true?