Exact2Pass

Last Update 1 hour ago Total Questions : 35
The Fortinet NSE 6 - FortiEDR 7.0 Administrator content is now fully updated, with all current exam questions added 1 hour ago. Deciding to include NSE6_EDR_AD-7.0 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our NSE6_EDR_AD-7.0 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these NSE6_EDR_AD-7.0 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Fortinet NSE 6 - FortiEDR 7.0 Administrator practice test comfortably within the allotted time.
Which two Python commands are supported when using FortiEDR Connect to directly access a protected device shell? (Choose two answers)
Refer to the Exhibit:
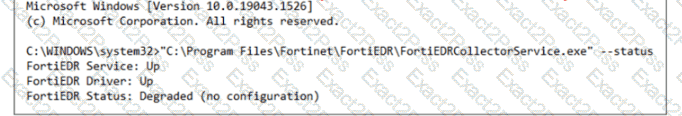
Based on the FortiEDR status output shown in the exhibit, what are two reasons for the degraded state? (Choose two answers)
Refer to the Exhibit:
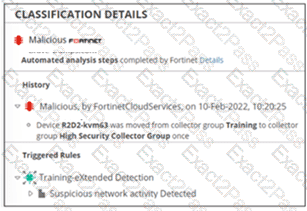
Based on the event shown in the exhibit, which two statements about the event are true? (Choose two answers)
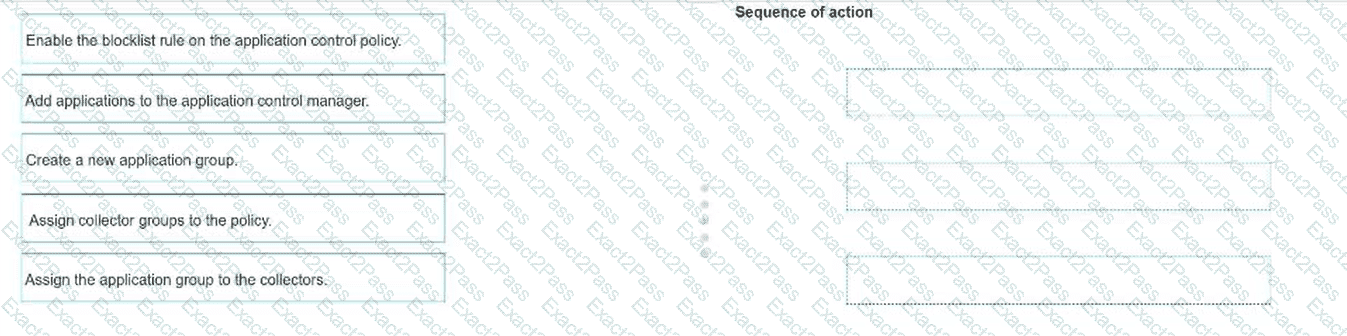
When implementing an application block policy in FortiEDR, which three actions, in order, reflect the correct operational sequence? (Choose three.)
Select an action in the left column and hold and drag it to a blank position in the column on the right. Place the three correct actions in order, starting with the first action at the top of the column. After you
place an action, you can move it again if you want to change your answer before proceeding to the next question. You must drop three actions in the work area.
Select and drag the screen divider to change the viewable area of the source and work areas.
Which two criteria are required for integrating FortiEDR with the Fortinet Security Fabric? (Choose two answers)
What action does an on-premises reputation server take when it receives a hash request that is not found in its local database? (Choose one answer)
A playbook is configured with two actions: terminate process and isolate device. The terminate process action fails because the process is protected by Windows. What is the expected behavior for the second action, isolate device? (Choose one answer)
You are asked to create a playbook to isolate a device with a collector. Which action category does isolating a device with a collector fall under? (Choose one answer)
Refer to the exhibit.
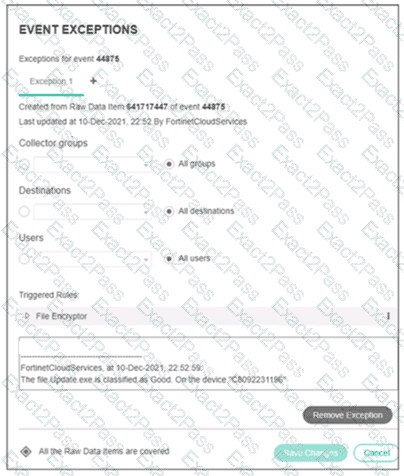
An event exception is shown. Which two statements about the exception are true? (Choose two answers)
Refer to the exhibits.
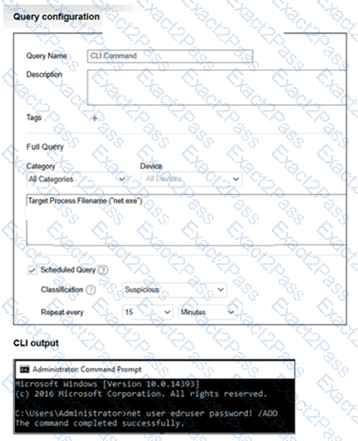
What happens when the net user command runs on an endpoint? (Choose one answer)