Exact2Pass
Last Update 22 hours ago Total Questions : 67
The Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect content is now fully updated, with all current exam questions added 22 hours ago. Deciding to include NSE7_CDS_AR-7.6 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our NSE7_CDS_AR-7.6 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these NSE7_CDS_AR-7.6 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect practice test comfortably within the allotted time.
Exhibit.
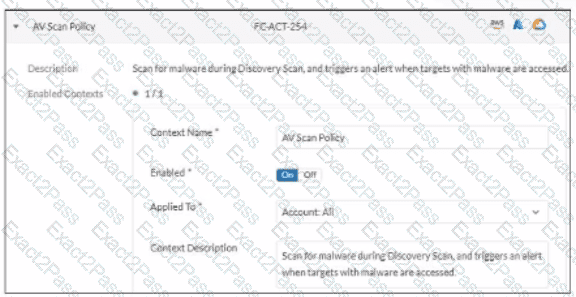
In which type of FortiCNP insights can an administrator examine the findings triggered by this policy?
You need a solution to safeguard public cloud-hosted web applications from the OWASP Top 10 vulnerabilities. The solution must support the same region in which your applications reside, with minimum traffic cost.
Which solution meets the requirements?
Refer to the exhibit.
You are troubleshooting a Microsoft Azure SDN connector issue on your FortiGate VM in Azure.
Which command can you use to examine details about API calls sent by the connector?
Refer to the exhibit.
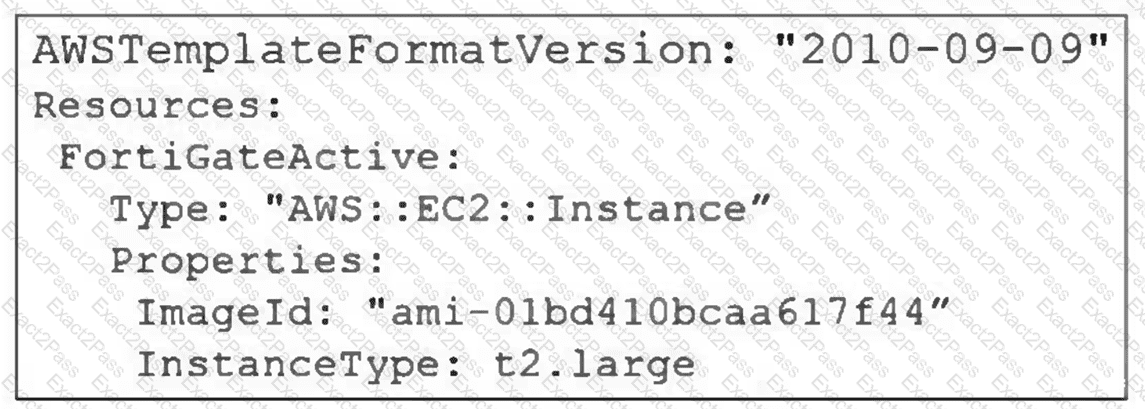
A senior administrator in a multinational organization needs to include a comment in the template shown in the exhibit to ensure that administrators from other regions change the EC2 instance size value to one that meets the requirements in their local deployments. How can the administrator add the comment in that section of the file? (Choose one answer)
Your DevOps team is evaluating different Infrastructure as Code (IaC) solutions for deploying complex Azure environments.
What is an advantage of choosing Azure Bicep over other IaC tools available?
Refer to the exhibit.
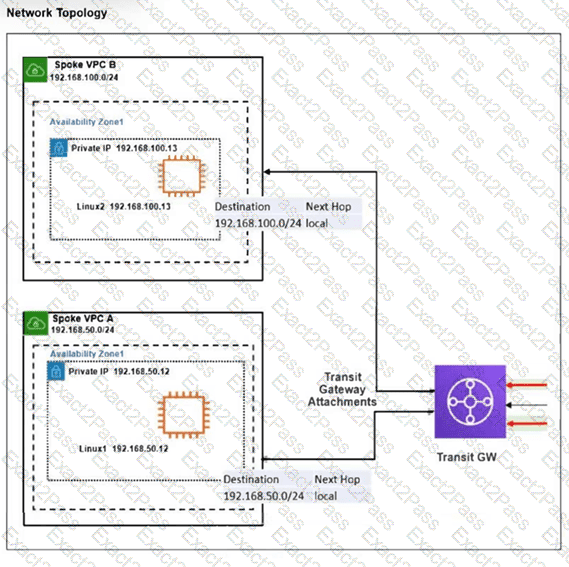
The exhibit shows a customer deployment of two Linux instances and their main routing table in Amazon Web Services (AWS). The customer also created a Transit Gateway (TGW) and two attachments. Which two steps are required to route traffic from Linux instances to the TGW? (Choose two answers)
Refer to the exhibit.
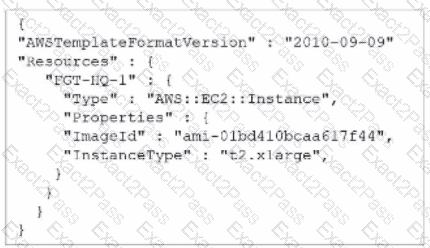
A senior administrator in a multinational organization needs to include a comment in the template shown in the exhibit to ensure that administrators from other regions change the Amazon Machine Image (AMI) ID to one that is valid in their location.
How can the administrator add the required comment in that section of the file?
Refer to the exhibit.
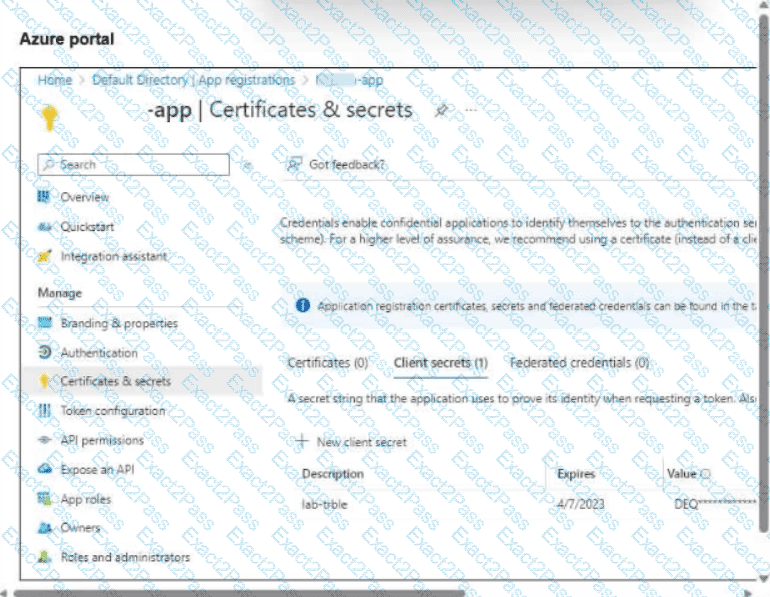
An administrator is trying to deploy a FortiGate VM in Microsoft Azure using Terraform. However, during the configuration, the Azure client secret is no longer visible in the Azure portal.
How would the administrator obtain the Azure client secret to configure in Terraform?
An organization is deploying FortiDevSec to enhance security for containerized applications, and they need to ensure containers are monitored for suspicious behavior at runtime.
Which FortiDevSec feature is best for detecting runtime threats?
An administrator decides to use the Use managed identity option on the FortiGate SDN connector with Microsoft Azure. However, the SDN connector is failing on the connection.
What must the administrator do to correct this issue?