Exact2Pass
Last Update 19 hours ago Total Questions : 159
The CompTIA SecAI+ v1 Exam content is now fully updated, with all current exam questions added 19 hours ago. Deciding to include CY0-001 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our CY0-001 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these CY0-001 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any CompTIA SecAI+ v1 Exam practice test comfortably within the allotted time.
A security analyst who is reviewing logs notices the following:
• Suspicious inputs are present and contain character look-alikes.
• Strange character substitutions
• Odd spacing
• Inputs that appear to be broken sentence structures
Which of the following best explains what the user was utilizing?
An administrator must conduct generative AI cost monitoring for use in the healthcare industry.
Which of the following criteria is the best way to calculate this cost?
Which of the following is the first step before using an online data set?
For which of the following situations would a human-in-the-loop be most recommended?
Which of the following certifies an organization in the use of responsible AI?
A security administrator needs to improve an AI model. During an initial investigation, the administrator notices that two successive login failures are recorded every day, and then a successful login occurs after a specific time interval. All the successful login attempts have been during office hours.
Which of the following techniques should the administrator use to improve the AI model ' s security?
A global security operations center (SOC) wants to adapt and leverage the strength of AI in order to enhance its security operations.
Which of the following is the best way to enhance the global SOC functions?
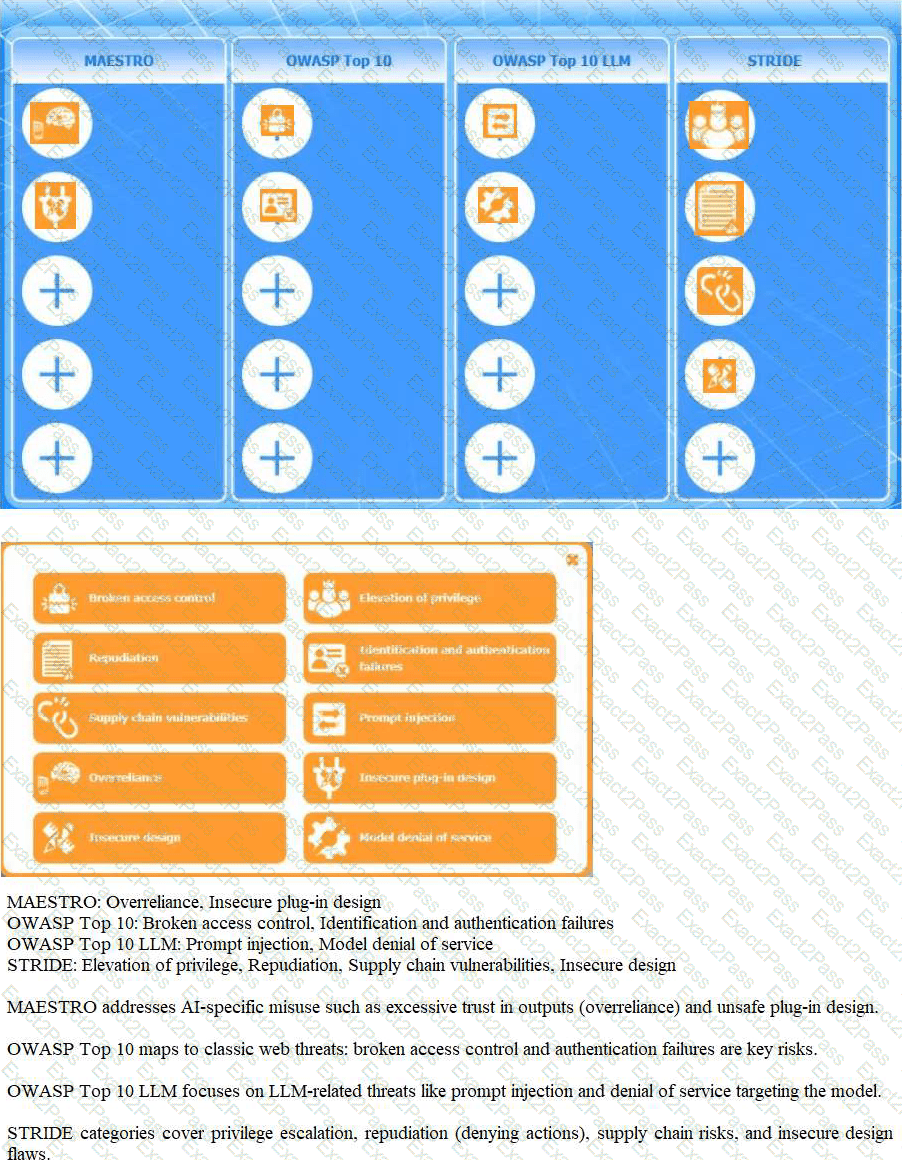
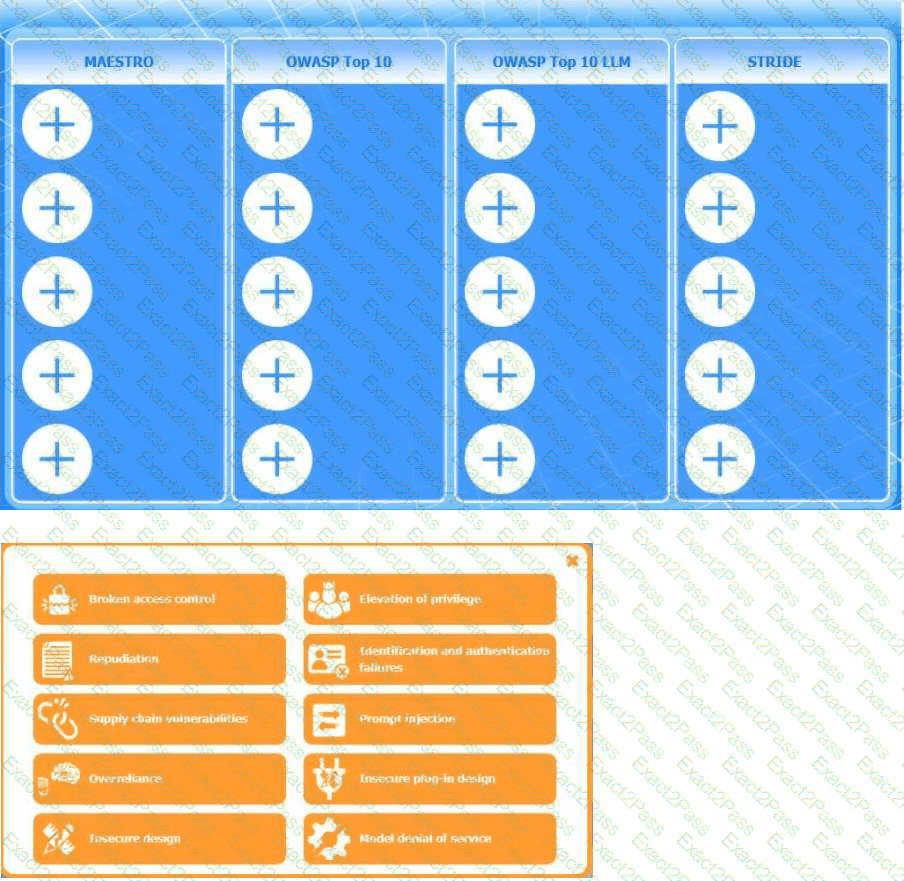
Instructions: Click the (+) to assign each threat category into its appropriate framework.
An architect is modeling an agentic system to meet security standards.
A loan company compares a machine learning model that was found on the dark web with the company ' s proprietary model. Using proprietary information, the company generates the following:
Input
Dark web model
Company ' s proprietary model
Jane A.
Approve
Approve
John B.
Deny
Deny
Ann J.
Deny
Deny
Joe H.
Approve
Approve
Which of the following should the AI red team recommend to mitigate risks for future deployments?
Which of the following describes the process of adjusting the distribution of underrepresented classes in an AI model data set to improve model performance?