Exact2Pass

The enterprise infrastructure protection and unified threat management landscape in 2026 demands highly sophisticated security policies and real-time perimeter defense controls. As commercial networks face volatile, multi-vector zero-day exploits, security administrators, firewall engineers, and hybrid cloud consultants must possess the technical capacity to deploy unified hardware and virtual appliance safeguards natively. Achieving the FCP - FortiGate 7.4 Administrator designation validates your senior-level mastery of structuring granular object barriers, organizing secure data streams, and managing automated system diagnostics across your global footprint. However, many network engineering professionals struggle on this intensive, 90-minute core platform evaluation because they treat it as a basic software vocabulary drill. Trusting flat, context-stripped answer files found on unverified public tech forums cannot prepare you for the complex situational logic of phase negotiation or packet-flow path tracing under live data center processing loads.
True success on this 50-question advanced system verification requires a comprehensive grasp of the full FortiOS v7.4 software architecture, spanning from initial deployment topologies to automated multi-link failover rules. Network defenders must maintain clear conceptual judgment regarding when to toggle between flow-based or proxy-based content inspection settings to balance throughput performance against deep-packet identification. Candidates frequently spend several months searching for high-yield fcp_fgt_ad-7.4 exam questions online, hoping to locate a comprehensive study guide, or checking system metrics to verify their policy ordering parameters. Without interactive learning environments, a structured enterprise security course, or targeted simulator practice that can provide actual help in exam preparation, passive reading fails to develop the critical troubleshooting capabilities needed to handle certificate validation faults or address central NAT mismatches within the security fabric.
At Exact2Pass, we replace passive reading with active, scenario-driven structural engineering exercises designed to build true platform confidence. Our premium preparation workspace simulates the functional operational layers, prompt verification command panels, and network state parameters of the active FortiGate ecosystem. We guide you through executing gap analyses on incoming commercial routing paths, configuring Fortinet Single Sign-On (FSSO) collectors, optimizing site-to-site IPsec VPN tunnels, and establishing automated security profile matrices. This focused practice builds the exact data-management strategy and system execution skills demanded by elite global enterprise consultation teams, ensuring you clear your proctored evaluation on your very first try.
The FCP_FGT_AD-7.4 certification is designed to assess your end-to-end cloud-powered advanced defense capabilities, from initial system setup and high availability configuration to advanced threat prevention and traffic shaping. Our realistic simulation platform replicates active FortiOS GUI dashboards, command-line interface tracking tools, and real-time distributed tracing paths instead of serving up generic multi-choice questionnaires. You will master the underlying multi-vendor integrations, operator-driven data ingestion perimeters, and service-level dependencies of the active Fortinet security ecosystem, preparing you to tackle any scenario-based infrastructure question with ease.
Which inspection mode does FortiGate use for application profiles if it is configured as a profile-based next-generation firewall (NGFW)?
Refer to exhibit.
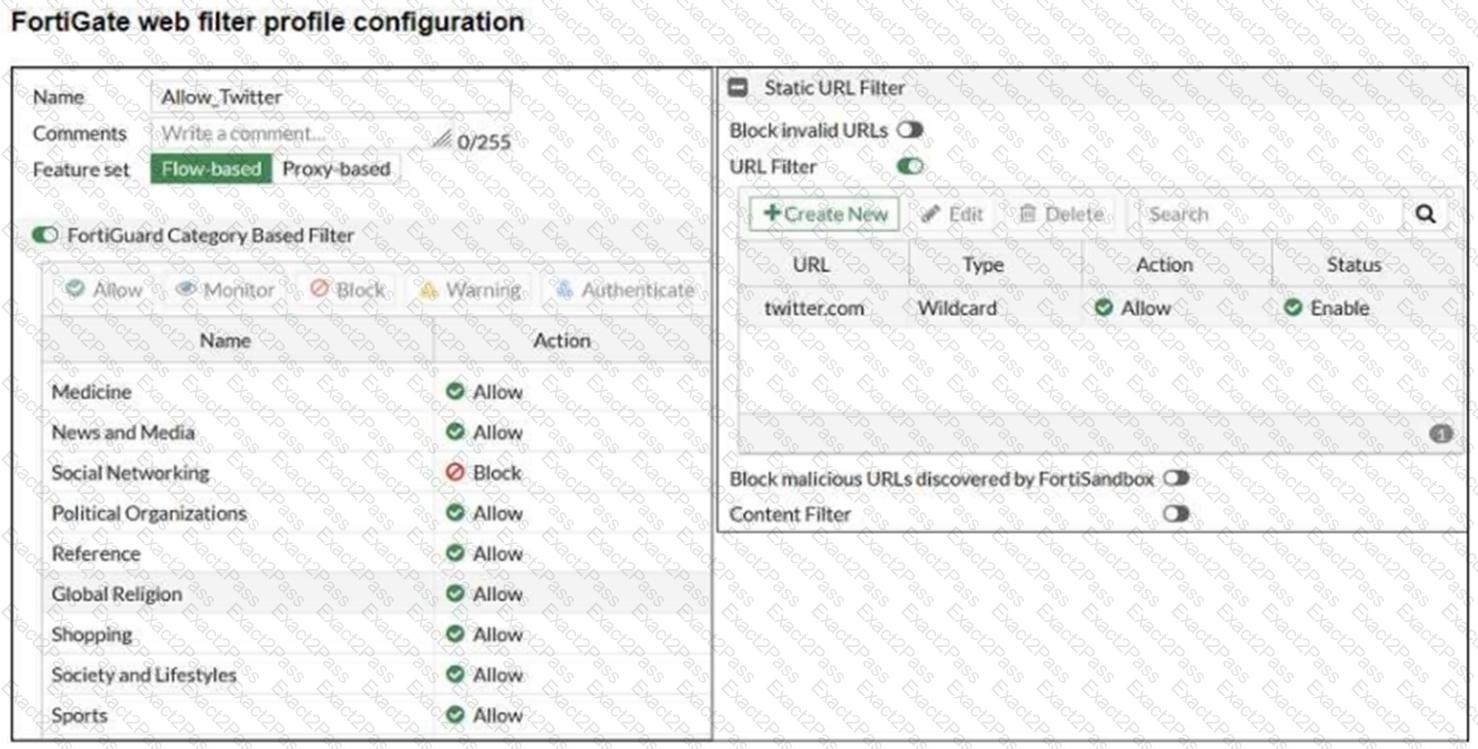
An administrator configured the web filtering profile shown in the exhibit to block access to all social networking sites except Twitter. However, when users try to access twitter.com , they are redirected to a FortiGuard web filtering block page.
Based on the exhibit, which configuration change can the administrator make to allow Twitter while blocking all other social networking sites?
Refer to the exhibit.
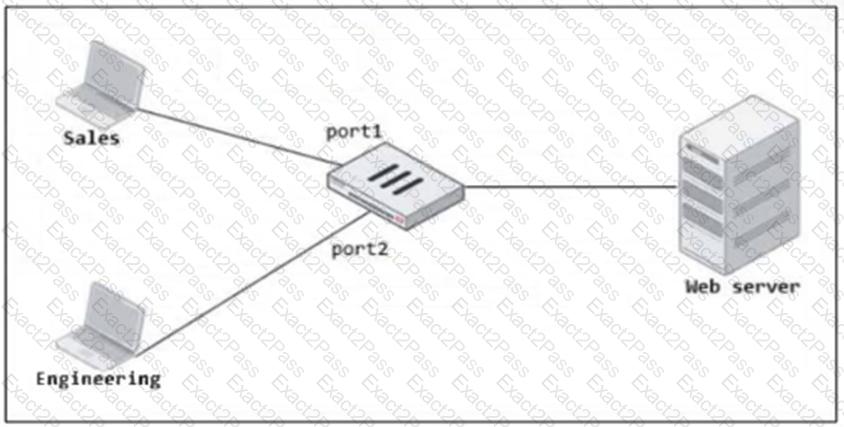
FortiGate has two separate firewall policies for Sales and Engineering to access the same web server with the same security profiles.
Which action must the administrator perform to consolidate the two policies into one?
Which statement is a characteristic of automation stitches?
Which three statements about SD-WAN zones are true? (Choose three.)
Which statement is correct regarding the use of application control for inspecting web applications?

