Exact2Pass
Last Update 7 hours ago Total Questions : 68
The Security, Specialist (JNCIS-SEC) content is now fully updated, with all current exam questions added 7 hours ago. Deciding to include JN0-336 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our JN0-336 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these JN0-336 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Security, Specialist (JNCIS-SEC) practice test comfortably within the allotted time.
How does the SSL proxy detect if a particular session is SSL encrypted?
You want to show tabular data for operational mode commands.
In this scenario, which logging parameter will provide this function?
Which two statements are correct about a chassis cluster? (Choose two.)
Which two statements describe how Juniper ATP Cloud improves security? (Choose two.)
What are two properties negotiated during IKE Phase 2? (Choose two.)
Which three different objects would be created, modified, cloned, and deleted in the Shared Objects workspace of Junos Space Security Director? (Choose three.)
Using Junos Space Security Director, you want to configure a unique firewall policy for a specific SRX Series device.
Which firewall policy rule would satisfy the requirement?
Using Junos Space Security Director, you want to configure a unique firewall policy for a specific SRX Series device.
Which firewall policy rules would satisfy the requirement?
Which statement is correct about Active Directory as an identity source for identity-aware security policies?
You are asked to configure your company SRX Series device to use identity-aware security policies. Information about your Active Directory network is shown in the exhibit.
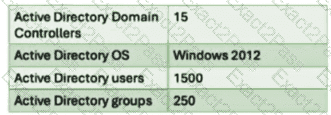
In this scenario, why must you configure JIMS instead of Active Directory as an identity source?