Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: buysanta

Exact2Pass Menu

Fortinet NSE 5 - FortiSwitch 7.6 Administrator

Last Update 17 hours ago Total Questions : 114

The Fortinet NSE 5 - FortiSwitch 7.6 Administrator content is now fully updated, with all current exam questions added 17 hours ago. Deciding to include NSE5_FSW_AD-7.6 practice exam questions in your study plan goes far beyond basic test preparation.

You'll find that our NSE5_FSW_AD-7.6 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these NSE5_FSW_AD-7.6 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Fortinet NSE 5 - FortiSwitch 7.6 Administrator practice test comfortably within the allotted time.

Question # 11

What can an administrator do to maintain the existing standalone FortlSwltch configuration while changing the management mode to FortLink?

A.

Use a migration tool based on python script to convert the configuration

B.

Enable the Forti-link setting on FortiSwitch before the authorization process

C.

FortiGate will automatically save the existing FortiSwitch configuration during the Forti-link management process.

D.

Register FortiSwitch to For1ISwitch Cloud to save a copy before managing by Forti-Gate.

Question # 12

Which statement about 802.1X security profiles using MAC-based authentication mode is true?

A.

FortiSwitch allows connectivity to all hosts connected to a port, if one host is authenticated.

B.

FortiSwitch can grant each device a different access level based on the credentials provided

C.

FortiSwitch performs faster when using this security mode on the ports.

D.

FortiSwitch must communicate with the RADIUS server to authenticate devices

Question # 13

Refer to the exhibit.

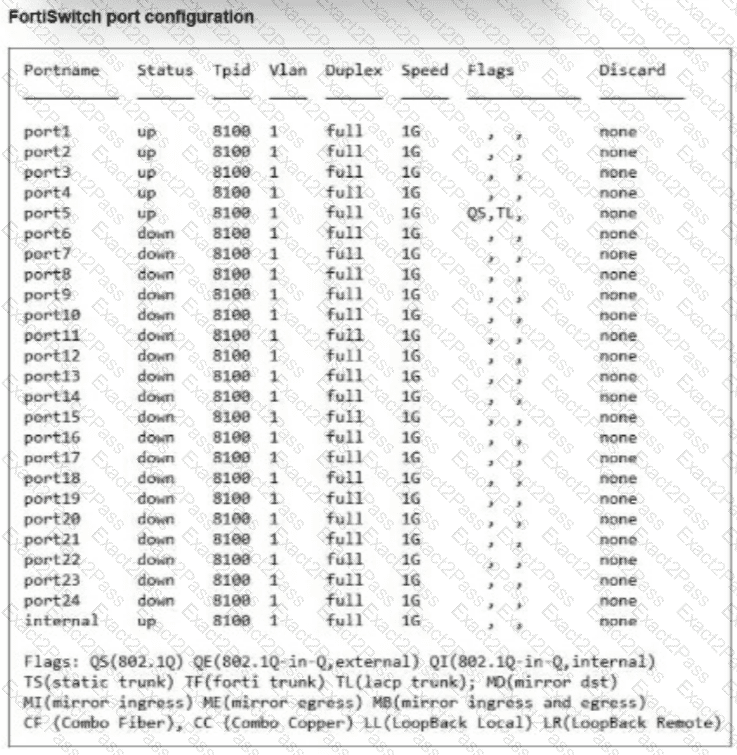
You run the command diagnose switch physical-ports summary on FortiSwitch.

Based on exhibit, what does the output indicate to about the FortiSwitch mode? (Choose one answer)

A.

FortiSwitch is configured as access ports.

B.

FortiSwitch is configured as a layer 3 router.

C.

FortiSwitch is in standalone mode.

D.

FortiSwitch is operating in managed mode.

Question # 14

Refer to the exhibit.

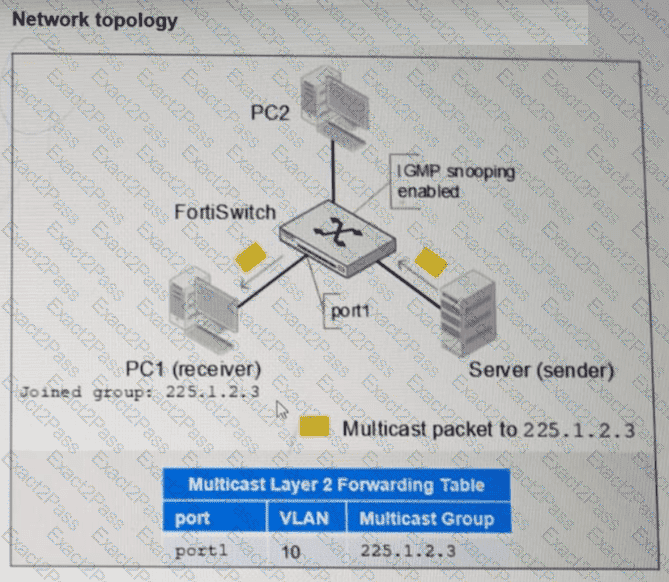
PC1 connected to port1 has joined multicast group 225.1.2.3 on VLAN 10 with IGMP snooping enabled. What will happen if you disable IGMP snooping on FortiSwitch? (Choose one answer)

A.

PC1 will be removed from the multicast group 225.1.2.3.

B.

The FortiSwitch will stop processing IGMP report join messages.

C.

Multicast traffic for 225.1.2.3 will be flooded to all ports.

D.

Multicast traffic will stop until a multicast receiver is detected.

Question # 15

Which two statements about DHCP snooping enabled on a FortiSwitch VLAN are true? (Choose two.)

A.

Enabling DHCP snooping on a FortiSwitch VLAN ensures requests and replies are seen by all DHCP servers.

B.

switch-controller-dhcp-snooping-verify-mac verifies the destination MAC address to protect against DHCP exhaustion attacks.

C.

By default, all FortiSwitch ports are set to forward client DHCP requests to untrusted ports.

D.

Settings related to DHCP option 82 are only configurable through the CLI

Question # 16

You are deploying a multitier FortiSwitch topology with redundant links between access and aggregation switches. The team is considering Multiple Spanning Tree Protocol (MSTP) to manage spanning tree across multiple VLANs. Which two Rapid STP (RSTP) features would be useful in this deployment to ensure fast convergence and predictable port roles? (Choose two answers)

A.

The process for selecting the root bridge

B.

Recalculating paths after a topology change

C.

Automatic VLAN assignment

D.

The rules for determining port roles

Question # 17

Which packet capture method allows FortiSwitch to capture traffic on trunks and management interfaces?

A.

SPAN

B.

Sniffer profile

C.

sFlow

D.

TCP dump

Question # 18

Which drop policy mode, if assigned to a congested port, will drop incoming packets until there is no congestion on the egress port?

A.

Tail-drop mode

B.

Weighted round robin mode.

C.

Random early detection mode

D.

Strict mode

Question # 19

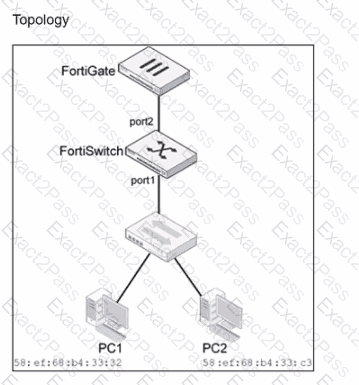
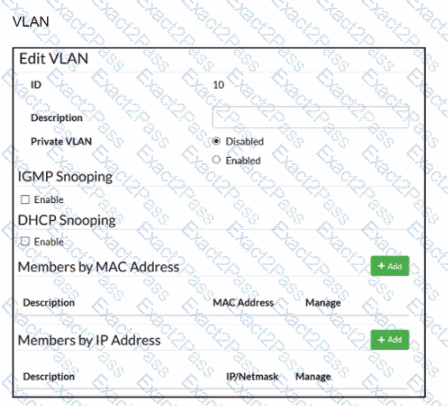
Refer to the exhibits

Traffic arriving on port2 on FortiSwitch is tagged with VLAN ID 10 and destined for PC1 connected on port1. PC1 expects to receive traffic untagged from port1 on FortiSwitch. Which two configurations can you perform on FortiSwitch to ensure PC1 receives untagged traffic on port1? (Choose two.)

A.

Add the MAC address of PC1 as a member of VLAN 10.

B.

Add VLAN ID 10 as a member of the untagged VLANs on port1.

C.

Remove VLAN 10 from the allowed VLANs and add it to untagged VLANs on port1.

D.

Enable Private VLAN on VLAN 10 and add VLAN 20 as an isolated VLAN.

Question # 20

Which statement best describes a benefit of using MAC, IP address, or protocol-based VLAN assignments on FortiSwitch? (Choose one answer)


A.

It disables 802.1X authentication while preserving user access control.1

B.

It requires devices to authenticate through a RADIUS server before VLAN tagging.

C.

It assigns ports to VLANs regardless of device type or traffic.

D.

It offers dynamic segmentation benefits similar to 802.1X authentication.2

Go to page: