Exact2Pass

Last Update 12 hours ago Total Questions : 120
The Splunk Certified Cybersecurity Defense Architect content is now fully updated, with all current exam questions added 12 hours ago. Deciding to include SPLK-5003 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our SPLK-5003 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these SPLK-5003 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Splunk Certified Cybersecurity Defense Architect practice test comfortably within the allotted time.
Buttercup Games is experiencing a multi-vector phishing attack that exploits trust in a popular machine-learning development platform. Malicious emails impersonating the platform’s employees direct developers to compromised models containing embedded malware.
How can Buttercup Games use automated threat detection and orchestrate an alert-response strategy when users report phishing emails?
Choose three
A critical legacy application server operates on an unsupported OS, and IT cannot install a security agent or forward logs from this server. The application processes sensitive data.
What is the best approach for continuously monitoring the server’s activity?
While collaborating with the Security Automation team, an architect reviews a playbook that automates the response to compromised credentials. The playbook includes these stages:
1. Examine the account to verify that it is not a service or control account.
2. Access all identity platforms and lock the user account.
3. Revoke all active sessions (email, VPN, and so on).
The architect identifies a possibility that the compromised credentials could be used remotely again.
Which action must be added to the playbook to mitigate this?
Review the output shown below.
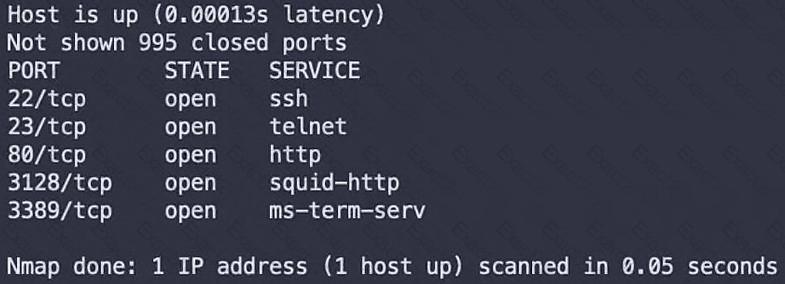
What should be the first action taken to harden this host?
Yokoco has engaged Helpime to conduct a penetration test. The test scope covers all web-facing internet applications. Helpime has completed the test and delivered its report to Yokoco.
What should be done with the report’s unremediated findings?
The cybersecurity team at a logistics management company plans to work with its software engineering practice in a “shift-left” approach to securing the software development life cycle (SDLC).
What improvement could the team recommend to enable early detection of software vulnerabilities?
Which of the following tools can be used to identify weak passwords?
Kevin, a SOC analyst, is working with the SRE team to investigate a report of slow responses from a customer-facing web application. While reviewing load balancer and WAF logs, Kevin discovers that one of the web servers hosting the application has gone offline. He finds no alerts in the WAF or from the endpoint detection and response agent running on that web server.
As part of triaging this incident, what should they do next?
Choose three
Where should high-value, low-volume data be kept for searching, such as alerts generated by security tools?
A security architect is collaborating with their cloud architect peer to introduce additional controls in the non-production cloud environment. Testing shows that implementing four of these controls will carry significant cost.
Which action must be completed before presenting the findings to the CISO?

