Exact2Pass

Last Update 11 hours ago Total Questions : 117
The Designing and Implementing Enterprise Network Assurance (300-445 ENNA) content is now fully updated, with all current exam questions added 11 hours ago. Deciding to include 300-445 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 300-445 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 300-445 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Designing and Implementing Enterprise Network Assurance (300-445 ENNA) practice test comfortably within the allotted time.
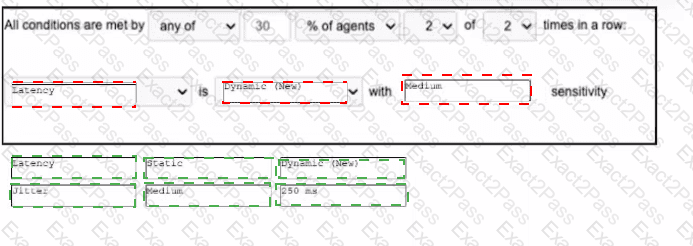
An engineer is configuring an alert to trigger whenever network latency spikes in a single test on at least 30% of the agents. Drag and drop the options from the bottom onto the boxes in the alert configuration screen. Not all options are used.
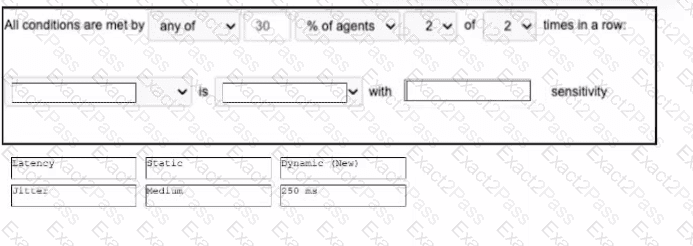
Refer to the exhibit.
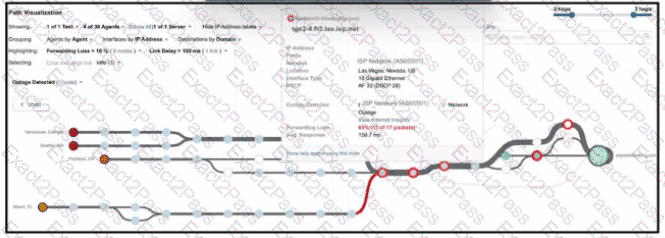
A network admin receives a P1 alert stating that one of the applications is not accessible from multiple locations. Which action restores the services?
What are the different ways to deploy a ThousandEyes Agent in a Switch? (Choose all that apply)
Refer to the exhibit.
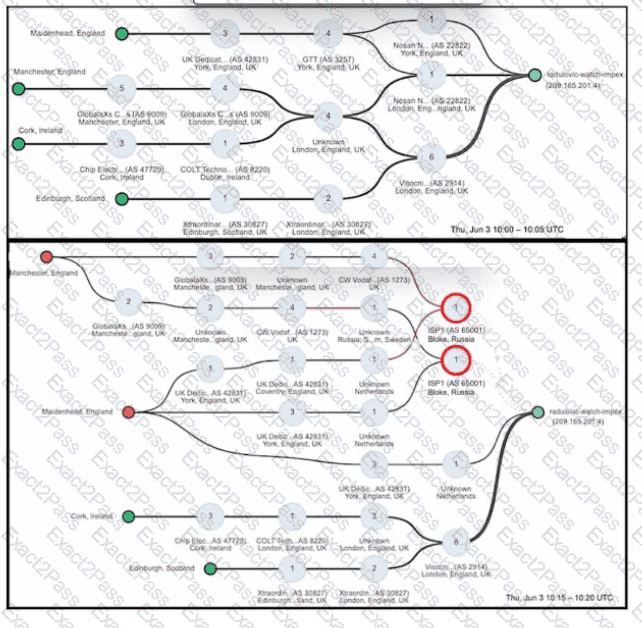
Cisco ThousandEyes sent an alert to report that the e-commerce website availability metric dropped. An engineer compares BGP Route Visualization for an alert in ThousandEyes before and during an outage. What is the root cause of the issue?
The Endpoint stopped appearing online after it was moved to another network. The customer reviewed the endpoint logs but did not identify anything suspicious. The customer also confirmed that the endpoint was online on the old network, and the new network is fully operational. Other endpoints that were moved to the new network are also online. Since the new network is small, the admin is using static IP assignment. What is the best way to bring the endpoint online?
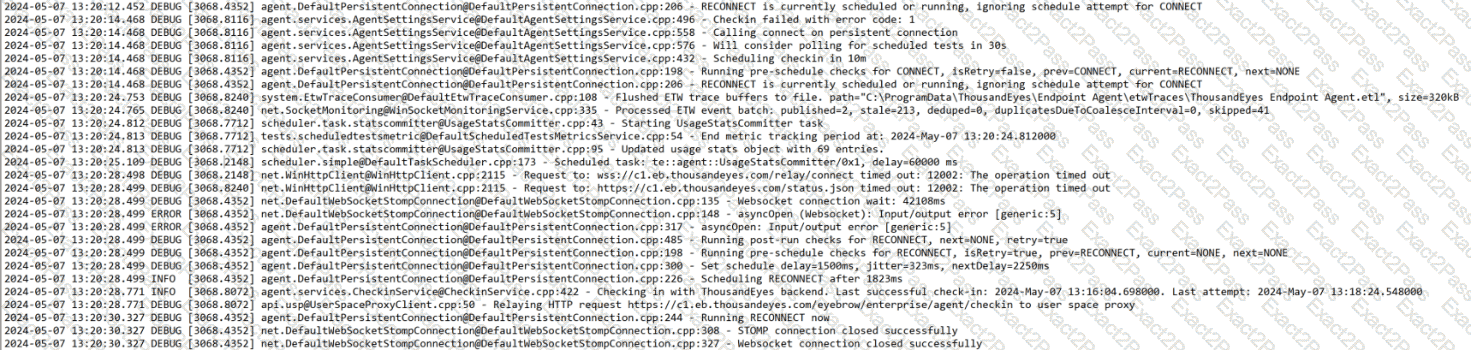
Considering the observed network behavior and the information in the exhibits, which action would be the most appropriate next step for the network administrator to take?
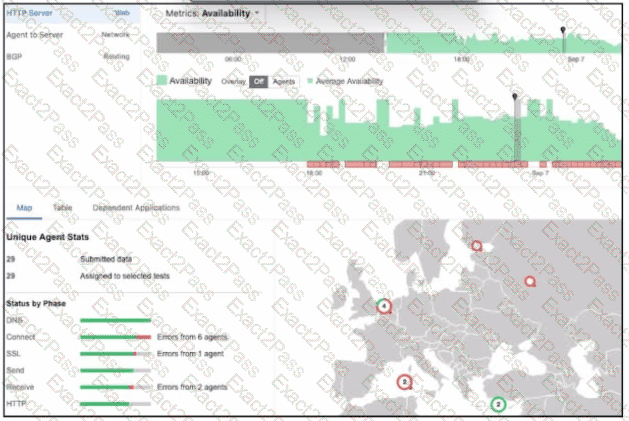
Refer to the exhibit. Which security incident is causing a drop in website availability?
Employees and customers of a retail company are experiencing performance issues with the store website, such as slowness during the login process or failure when adding items to the cart. Which test type is the most useful for identifying the root cause of these problems?
A campus site uses two ISPs to provide Internet connection – one as the active provider and the other as a backup provider. An engineer is configuring an alert rule in Cisco ThousandEyes to trigger an alert when the upstream Internet connection fails back to the backup Internet connection. Which alert condition must be configured?
Which on-premises method is used to deploy the Cisco ThousandEyes Endpoint Agent MSI pack-age at scale in a Windows environment?