Exact2Pass

Last Update 22 hours ago Total Questions : 105
The Splunk Certified Cybersecurity Defense Engineer content is now fully updated, with all current exam questions added 22 hours ago. Deciding to include SPLK-5002 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our SPLK-5002 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these SPLK-5002 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Splunk Certified Cybersecurity Defense Engineer practice test comfortably within the allotted time.
An engineer has been asked to build a new dashboard after an increase in login failures across the organization ' s Microsoft Azure domain. They need to construct a search to only display failed logins for their Azure Active Directory users and create a visualization that will help quickly identify failed logins that originate outside of North America. Which search and visualization type combination will achieve this?
Which practices strengthen the development of Standard Operating Procedures (SOPs)? (Choose three)
An engineer has been working on building a new automation for the SOC. What Scope should be selected in the SOAR Playbook Debugger during the playbook development to ensure consistency?
Which field in the risk index is used to describe the activity within a finding?
What document can be helpful in understanding the prioritization of risk when comparing entities in an organization?
A Detection Engineer works closely with SOC leads to define expected analyst workflow, often documented as a Standard Operating Procedure (SOP). Which capability can be used to document expected analyst actions in an investigation?
Which of the following detections would use a high count of events with Windows Event Code 4740 grouped by a user to determine suspicious behavior?
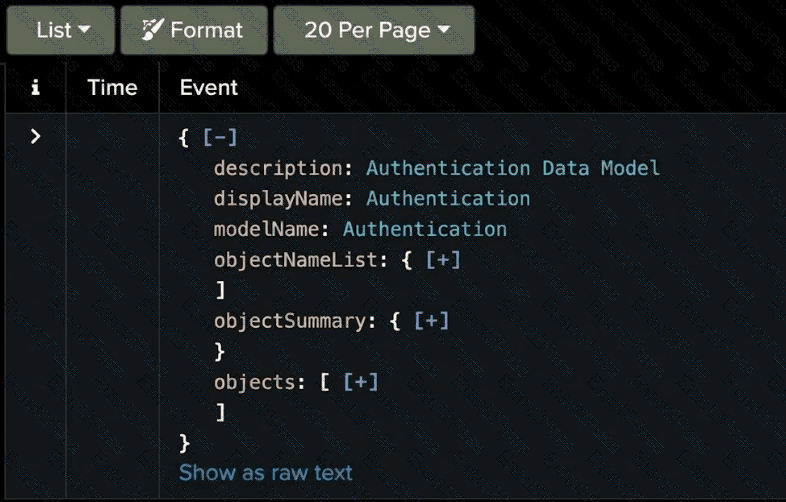
Which search command was used to generate the result in the image below?
The SOC manager has a desire to measure mean time to acknowledge finding (notable event) in order to meet a desired service-level objective. Which two fields can be used to measure the difference?
What field is used by default to direct data into CIM data model datasets?

