Exact2Pass

Last Update 55 minutes ago Total Questions : 69
The Cisco Certified Support Technician (CCST) Cybersecurity content is now fully updated, with all current exam questions added 55 minutes ago. Deciding to include 100-160 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 100-160 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 100-160 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Cisco Certified Support Technician (CCST) Cybersecurity practice test comfortably within the allotted time.
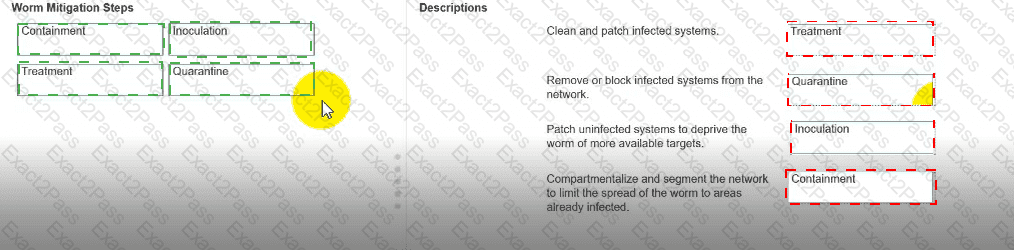
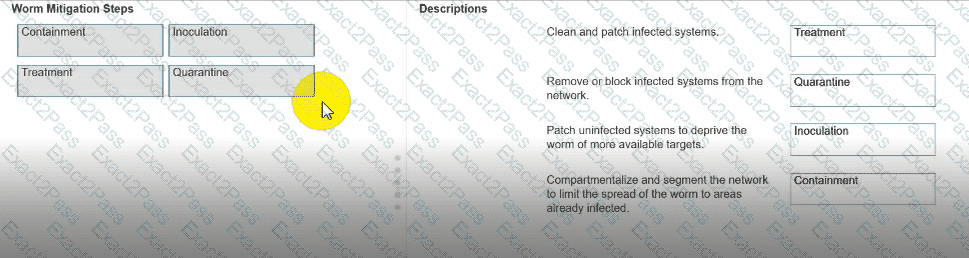
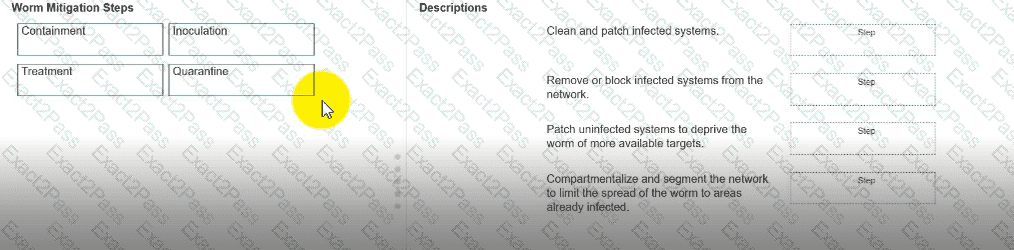
Move each worm mitigation step from the list on the left to the correct description on the right.
Note: You will receive partial credit for each correct answer.
The company web server collects information through a form. The form is accessed by using port 80. The form content is transferred to an encrypted database for storage. You are investigating a complaint that the form content has been compromised.
What is the cause of the security breach?
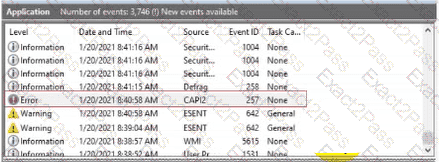
You are reviewing the Application log on a Windows computer. You see an event with an error-level message as shown.
What can you determine about the application that generated the event message?
An administrator wants to ensure that any files downloaded from the internet are automatically scanned for malicious code before execution. Which security control should be implemented?
Which two private IPv4 addresses would be blocked on the Internet to prevent security and performance issues? (Choose two.)
Note: You will receive partial credit for each correct selection.
You need to filter the websites that employees can access on the company network.
Which type of device should you deploy?
During an incident response, the security team needs to isolate a compromised server from the rest of the network but still allow forensic analysis. Which action should they take?
You notice that a new CVE has been shared to an email group that you belong to.
What should you do first with the CVE?
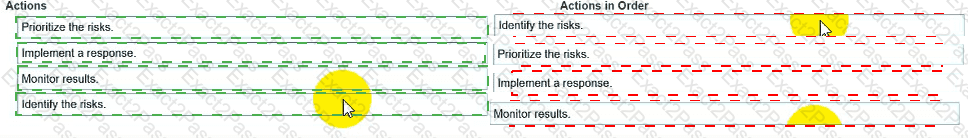
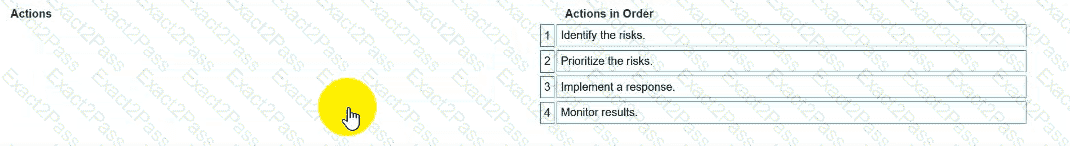
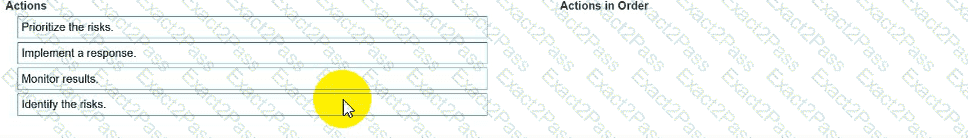
You need to manage security risks at your company. In which order should you complete the actions?
Move all the actions to the answer area and place them in the correct order.
You work for a hospital that stores electronic protected health information (ePHI) in an online portal. Authorized employees can use their mobile devices to access patient ePHI.
You need to ensure that employees’ mobile devices comply with HIPAA regulations.
Which safeguard should you develop and implement?