Exact2Pass

Last Update 15 hours ago Total Questions : 444
The Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 content is now fully updated, with all current exam questions added 15 hours ago. Deciding to include 300-710 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 300-710 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 300-710 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 practice test comfortably within the allotted time.
An engineer is configuring a second Cisco FMC as a standby device but is unable to register with the active unit. What is causing this issue?
An engineer must integrate a thud-party security Intelligence teed with Cisco Secure Firewall Management Center. Secure Firewall Management Center is running Version 6.2 3 and has 8 GB of memory. Which two actions must be taken to implement Throat Intelligence Director? (Choose two.)
What is the result when two users modify a VPN policy at the same lime on a Cisco Secure Firewall Management Center managed device?
A network engineer is tasked with minimising traffic interruption during peak traffic limes. When the SNORT inspection engine is overwhelmed, what must be configured to alleviate this issue?
An engineer needs to configure remote storage on Cisco FMC. Configuration backups must be available from a secure location on the network for disaster recovery. Reports need to back up to a shared location that auditors can access with their Active Directory logins. Which strategy must the engineer use to meet these objectives?
A network administrator notices that remote access VPN users are not reachable from inside the network. It is determined that routing is configured correctly, however return traffic is entering the firewall but not leaving it What is the reason for this issue?
Which two dynamic routing protocols are supported in Firepower Threat Defense without using FlexConfig? (Choose two.)
A network administrator reviews the file report for the last month and notices that all file types, except exe. show a disposition of unknown. What is the cause of this issue?
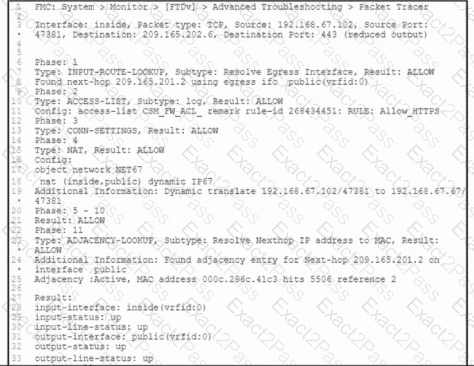
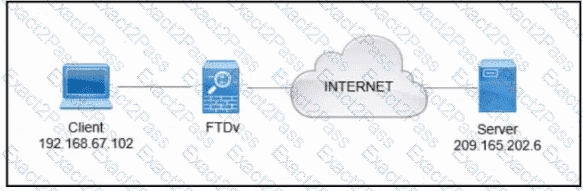
Refer to the exhibit. A client that has IP address 192.168.67.102 reports issues when connecting to a remote server. Based on the topology and output of packet tracer tool, which action resolves the connectivity issue?
A network engineer must configure the cabling between a Cisco Secure Firewall Threat Defense appliance and a network so the Secure Firewall Threat Defense appliance performs inline to analyze and tune generated intrusion events before going live. Which Secure Firewall Threat Defense interface mode must the engineer use?

