Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: buysanta

Exact2Pass Menu

Fortinet NSE 7 - Secure Networking 7.6 Architect

Last Update 13 hours ago Total Questions : 177

The Fortinet NSE 7 - Secure Networking 7.6 Architect content is now fully updated, with all current exam questions added 13 hours ago. Deciding to include NSE7_FSN_AR-7.6 practice exam questions in your study plan goes far beyond basic test preparation.

You'll find that our NSE7_FSN_AR-7.6 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these NSE7_FSN_AR-7.6 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Fortinet NSE 7 - Secure Networking 7.6 Architect practice test comfortably within the allotted time.

Question # 31

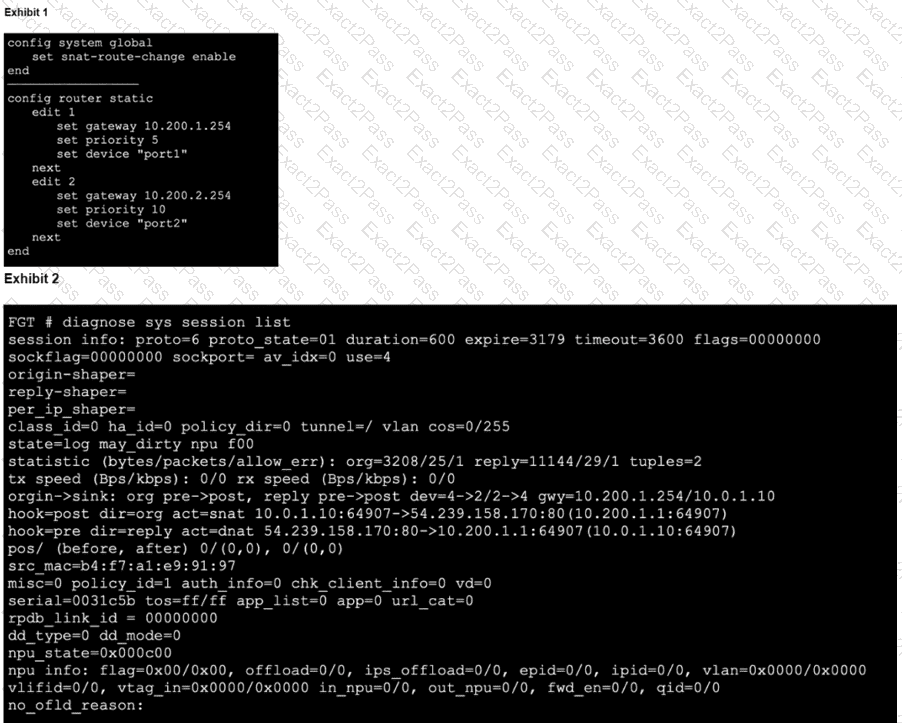
Refer to the exhibits,

which show the configuration on FortiGate and partial session information for internet traffic from a user on the internal network. If the priority on route ID 2 were changed from 10 to 0, what would happen to traffic matching that user session? (Choose one answer)

A.

The session would be deleted, and the client would need to start a new session.

B.

The session would remain in the session table, but its traffic would now egress from both port1 and port2.

C.

The session would remain in the session table, and its traffic would egress from port2.

D.

The session would remain in the session table, and its traffic would egress from port1.

Question # 32

Refer to the exhibit, which shows a partial output of the real-time LDAP debug.
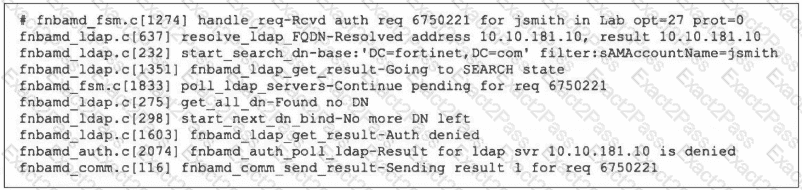
What two actions can the administrator take to resolve this issue? (Choose two.)

A.

Ensure the user logs in using ' John Smith ' not ' jsmith ' .

B.

Ensure the user is providing the correct user credentials.

C.

Ensure the user is a member of at least one AD group to ensure step 4 of the LDAP authentication process is successful.

D.

Ensure the account is active.

Question # 33

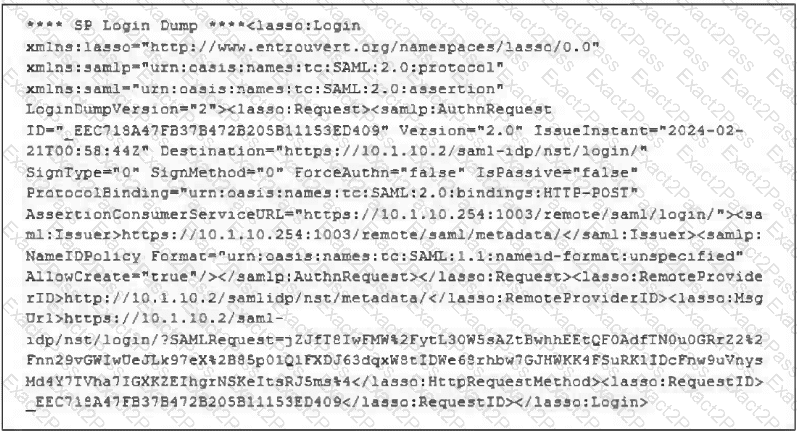
Refer to the exhibit.

The output from using the command diagnose debug application samld -1 to diagnose a SAML connection is shown. Based on this output, which two conclusions can you draw? (Choose two answers)

A.

The IdP IP address is 10.1.10.254.

B.

The SP IP address is 10.1.10.254.

C.

The SP IP address is 10.1.10.2.

D.

The IdP IP address is 10.1.10.2.

Question # 34

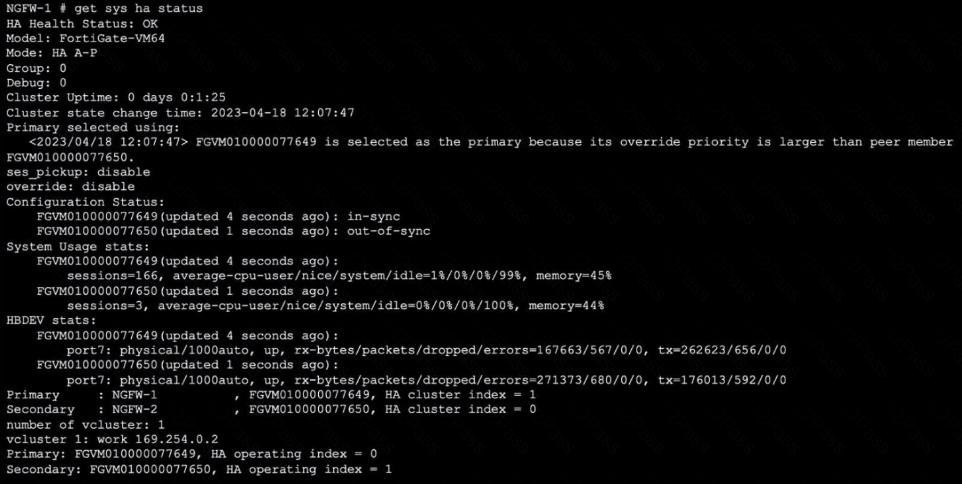
Exhibit.

Refer to the exhibit, which shows the output of get system ha status.

NGFW-1 and NGFW-2 have been up for a week.

Which two statements about the output are true? (Choose two.)

A.

If a configuration change is made to the primary FortiGate at this time, the secondary will initiate a synchronization reset.

B.

If port 7 becomes disconnected on the secondary, both FortiGate devices will elect itself as primary.

C.

If FGVM...649 is rebooted. FGVM...650 will become the primary and retain that role, even after FGVM...649 rejoins the cluster.

D.

If no action is taken, the primary FortiGate will leave the cluster because of the current sync status.

Question # 35

Refer to the exhibit, which shows a partial output of a real-time LDAP debug.
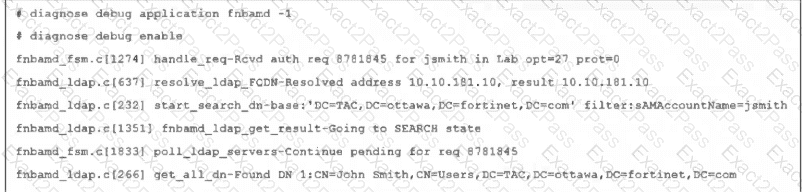
What two conclusions can you draw from the output? (Choose two.)

A.

The user was found in the LDAP tree, whose root is TAC.ottawa.fortinet.com.

B.

FortiOS performs a bind to the LDAP server using the user ' s credentials.

C.

FortiOS collects the user group information.

D.

FortiOS is performing the second step (Search Request) in the LDAP authentication process.

Question # 36

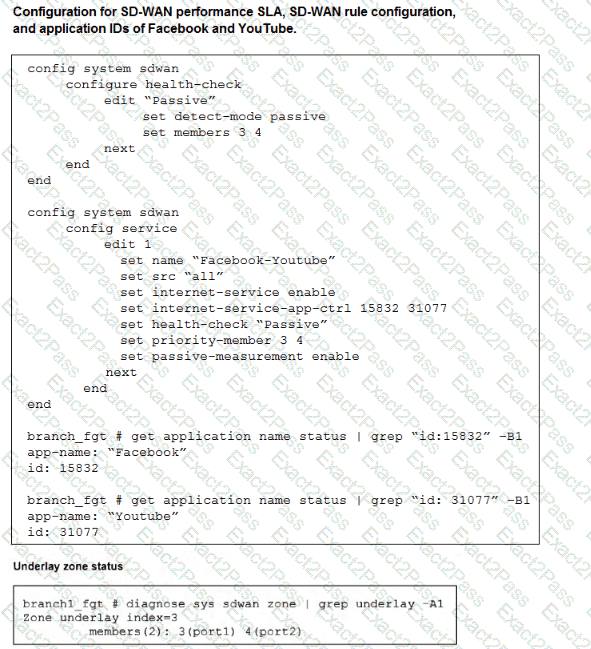
Refer to the exhibits.

Which two statements are true about the health and performance of SD-WAN members 3 and 4? (Choose two.)

A.

Only related TCP traffic is used for performance measurement.

B.

The performance is an average of the metrics measured for Facebook and YouTube traffic passing through the member.

C.

FortiGate identifies the member as dead when there is no Facebook and YouTube traffic passing through the member.

D.

Encrypted traffic is not used for the performance measurement.

Question # 37

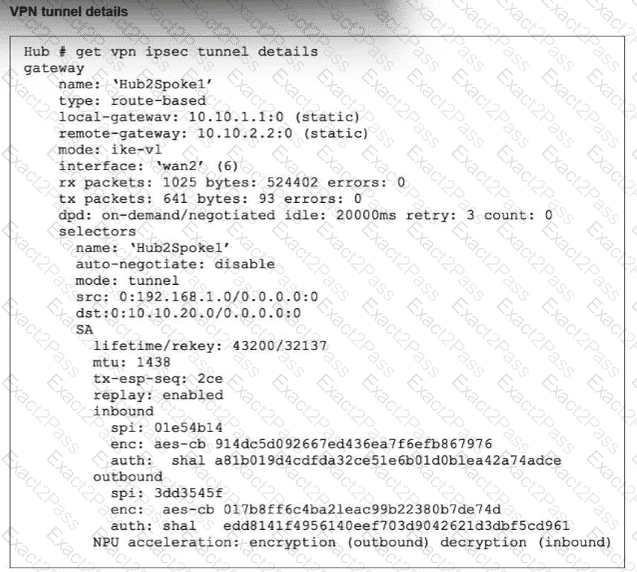
Refer to the exhibit.

Partial output of the get vpn ipsec tunnel details command is shown. Based on the output, which two statements are correct? (Choose two.)

A.

The npu_flag for this tunnel is 02.

B.

Different SPI values are a result of auto-negotiation being disabled for phase2 selectors.

C.

The npu_flag for this tunnel is 03.

D.

Anti-replay is enabled.

Question # 38

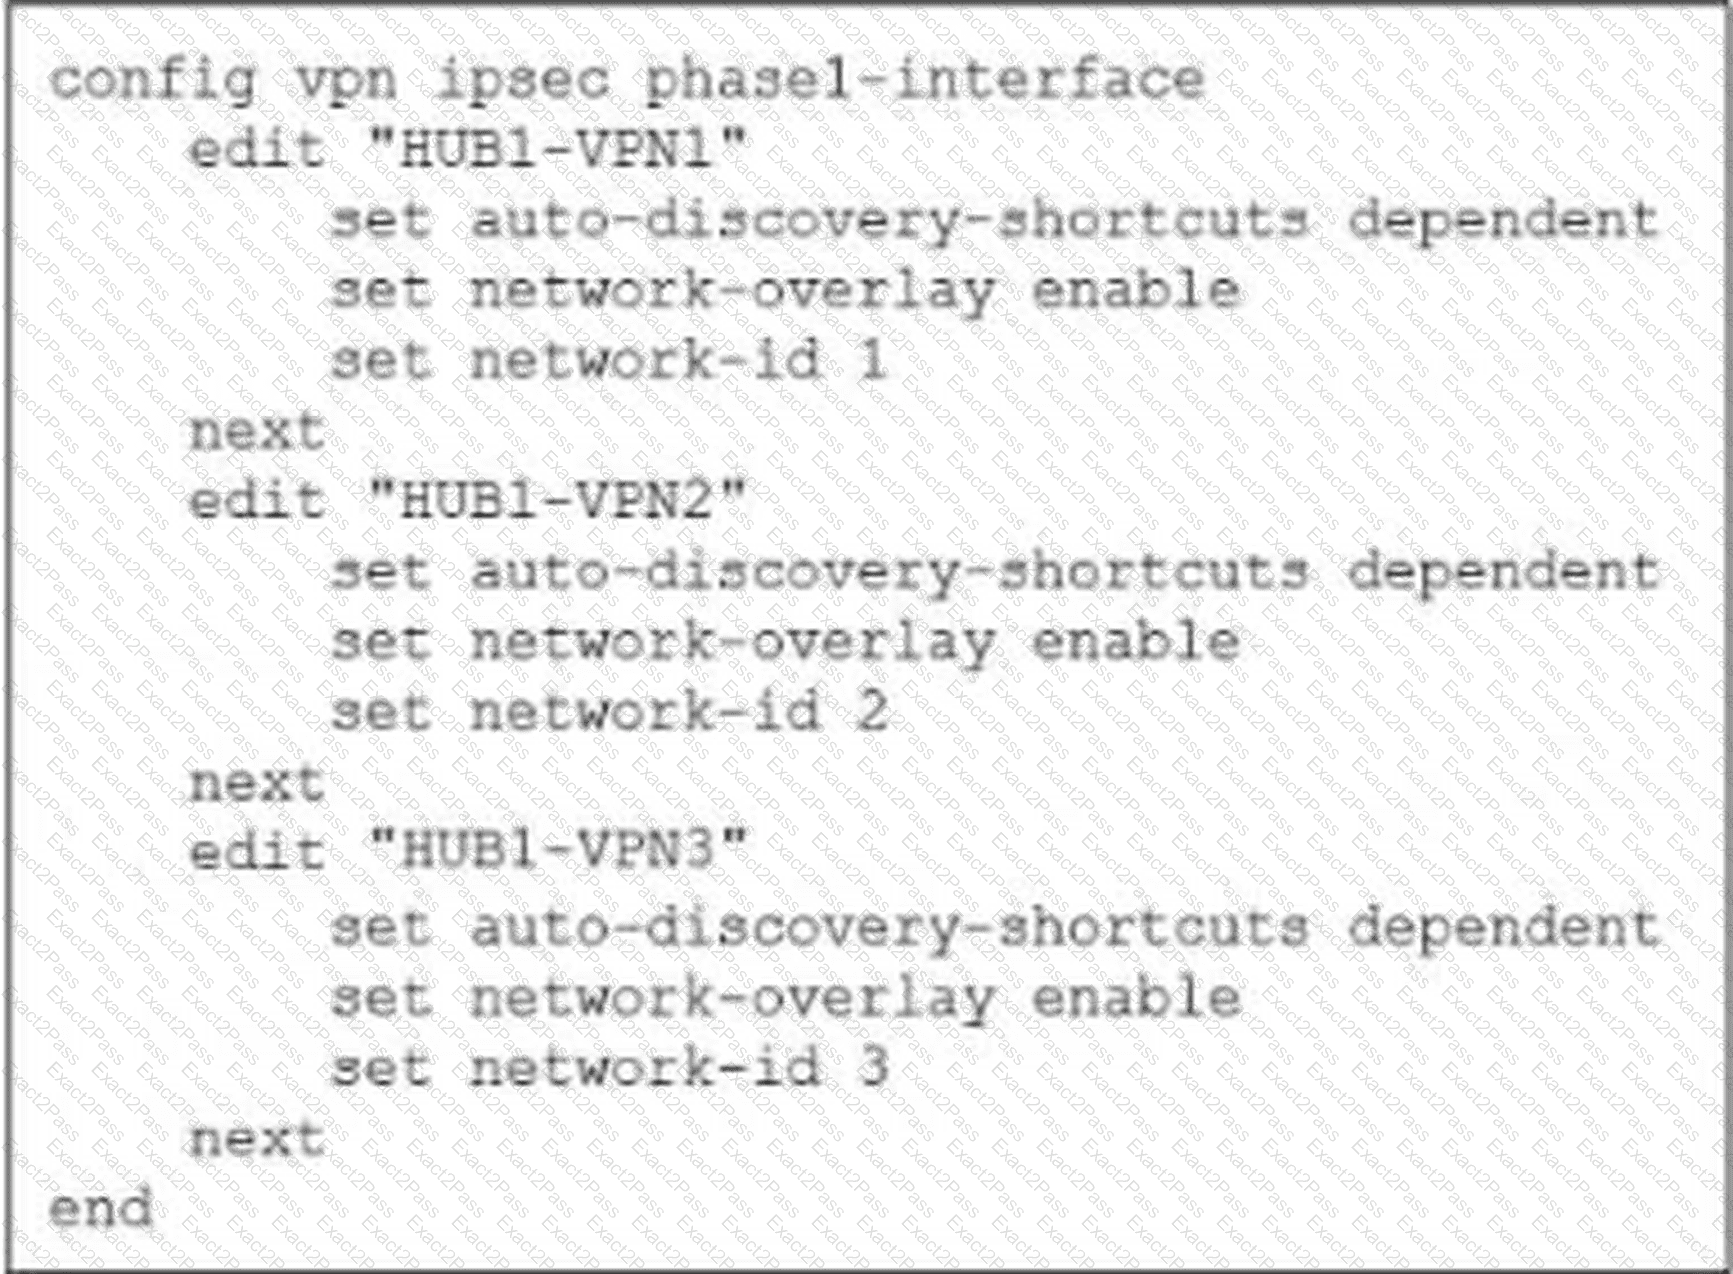
Refer to the exhibit.

You update the spokes configuration of an existing auto-discovery VPN (ADVPN) topology by adding the parameters shown in the exhibit.

Which is a valid objective of those settings?

A.

Convert the configuration from ADVPN to ADVPN 2.0.

B.

Prevent multiple shortcuts from being established over the same overlay.

C.

Prevent cross-overlay shortcuts.

D.

Enable the tunnels as overlay links.

Question # 39

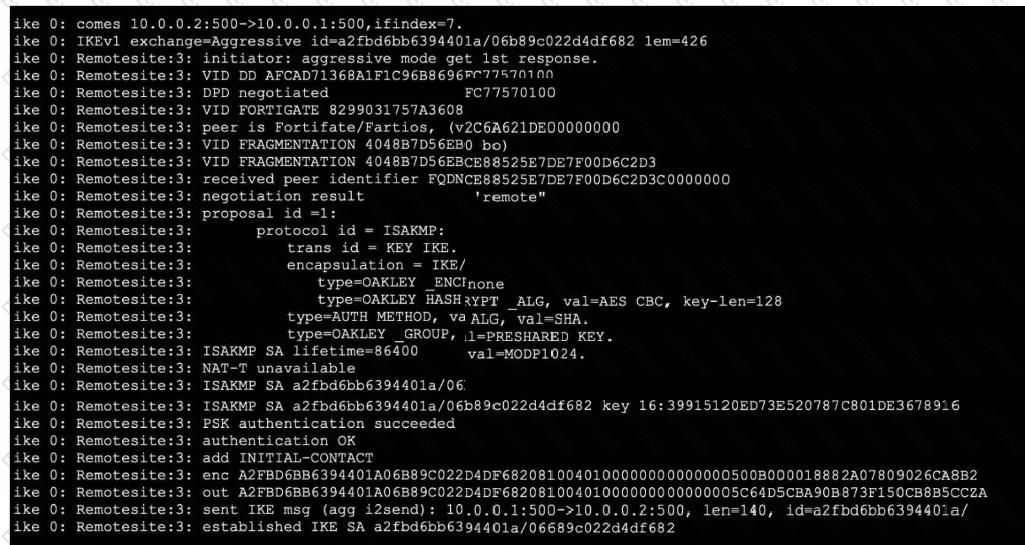
Exhibit.

Refer to the exhibit, which contains partial output from an IKE real-time debug.

Which two statements about this debug output are correct? (Choose two.)

A.

Perfect Forward Secrecy (PFS) is enabled in the configuration.

B.

The local gateway IP address is 10.0.0.1.

C.

It shows a phase 2 negotiation.

D.

The initiator provided remote as its IPsec peer ID.

Question # 40

In IKEv2, which exchange establishes the first CHILD_SA?
A.

IKE_SA_INIT

B.

INFORMATIONAL

C.

CREATE_CHILD_SA

D.

IKE_AUTH

Go to page: