Exact2Pass

Last Update 14 hours ago Total Questions : 444
The Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 content is now fully updated, with all current exam questions added 14 hours ago. Deciding to include 300-710 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 300-710 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 300-710 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 practice test comfortably within the allotted time.
How many report templates does the Cisco Firepower Management Center support?
An engineer is using the configure manager add < FMC IP > Cisc402098527 command to add a new Cisco FTD device to the Cisco FMC; however, the device is not being added. Why Is this occurring?
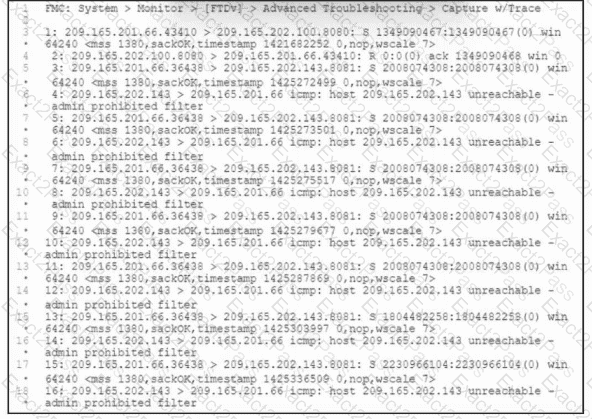
Refer to the exhibit. Users attempt to connect to numerous external resources on various TCP ports. If the users mistype the port, their connection closes immediately, and it takes more than one minute before the connection is torn down. An engineer manages to capture both types of connections as shown in the exhibit. What must the engineer configure to lower the timeout values for the second group of connections and resolve the user issues?
An administrator Is setting up a Cisco PMC and must provide expert mode access for a security engineer. The engineer Is permitted to use only a secured out-of-band network workstation with a static IP address to access the Cisco FMC. What must be configured to enable this access?
A network engineer is deploying a pair of Cisco Secure Firewall Threat Defense devices managed by Cisco Secure Firewall Management Center tor High Availability Internet access is a high priority for the business and therefore they have invested in internet circuits from two different ISPs. The requirement from the customer Is that Internet access must do available to their user’s oven if one of the ISPs is down. Which two features must be deployed to achieve this requirement? (Choose two.)
Which type of certificate must be exported from Cisco ISE to integrate Cisco Secure Firewall Management Center with pxGrid?
A network administrator notices that inspection has been interrupted on all non-managed interfaces of a device. What is the cause of this?
An engineer is reviewing an existing custom server fingerprint on a Cisco Secure Firewall because the current information is inaccurate. Which action must the engineer take to improve the accuracy of the network discovery rules?
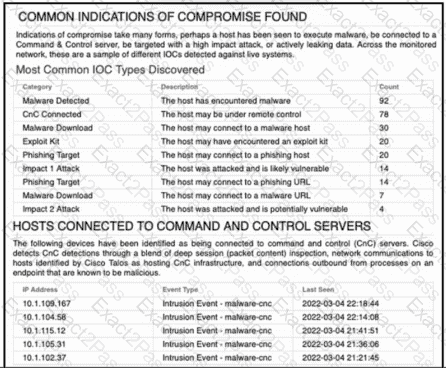
Refer to the exhibit. An engineer analyzes a Network Risk Report from Cisco Secure Firewall Management Center. What should the engineer recommend implementing to mitigate the risk?
An engineer has been tasked with providing disaster recovery for an organization ' s primary Cisco FMC. What must be done on the primary and secondary Cisco FMCs to ensure that a copy of the original corporate policy is available if the primary Cisco FMC fails?

