Exact2Pass

Last Update 14 hours ago Total Questions : 444
The Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 content is now fully updated, with all current exam questions added 14 hours ago. Deciding to include 300-710 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 300-710 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 300-710 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 practice test comfortably within the allotted time.
An engineer is integrating Cisco Secure Endpoint with Cisco Secure Firewall Management Center in high availability mode. Malware events detected by Secure Endpoint must also be
received by Secure Firewall Management Center and public cloud services are used. Which two configurations must be selected on both high availability peers independently? (Choose two.)
Which CLI command is used to generate firewall debug messages on a Cisco Firepower?
Encrypted Visibility Engine (EVE) is enabled under which lab on an access control policy in Cisco Secure Firewall Management Centre?
What is an advantage of adding multiple inline interface pairs to the same inline interface set when deploying an asynchronous routing configuration?
Which policy rule is included in the deployment of a local DMZ during the initial deployment of a Cisco NGFW through the Cisco FMC GUI?
An engineer is investigating connectivity problems on Cisco Firepower for a specific SGT. Which command allows the engineer to capture real packets that pass through the firewall using an SGT of 64?
An engineer runs the command restore remote-manager-backup location 2.2.2.2 admin /Volume/home/admin FTD408566513.zip on a Cisco FMC. After connecting to the repository, the Cisco FTD device is unable to accept the backup file. What is the reason for this failure?
A cisco Secure firewall Threat Defence device is configured in inline IPS mode to inspect all traffic that passes through the interfaces in the inline set. Which setting in the inline set configuration must be connected to allow traffic to pass through uninterrupted when VDB updates are being applied?
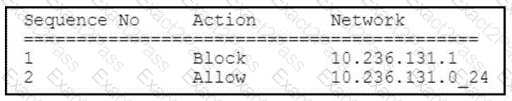
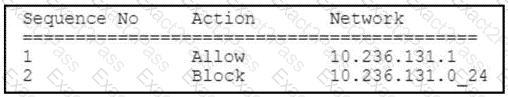
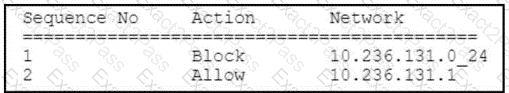
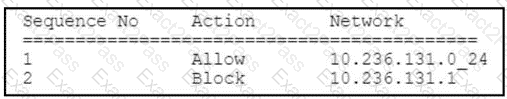
A security engineer must create an access list object in Cisco Secure Firewall Management Center to allow traffic to IP address 10.236.131.1 but block traffic to IP address 10.236.131.0/24. Which access control entries must the engineer create?
A)
B)
C)
D)
A network administrator wants to configure a new Secure Firewall Threat Defense instance, which is managed by Cisco Secure Firewall Management Center, to load balance internet-bound traffic across multiple zones. Secure Firewall is connected to upstream ISP devices in multiple Zones. Which action must be taken to meet the requirement?

