Exact2Pass

Last Update 6 hours ago Total Questions : 534
The Designing, Deploying and Managing Network Automation Systems AUTOCOR v2.0 content is now fully updated, with all current exam questions added 6 hours ago. Deciding to include 350-901 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 350-901 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-901 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Designing, Deploying and Managing Network Automation Systems AUTOCOR v2.0 practice test comfortably within the allotted time.
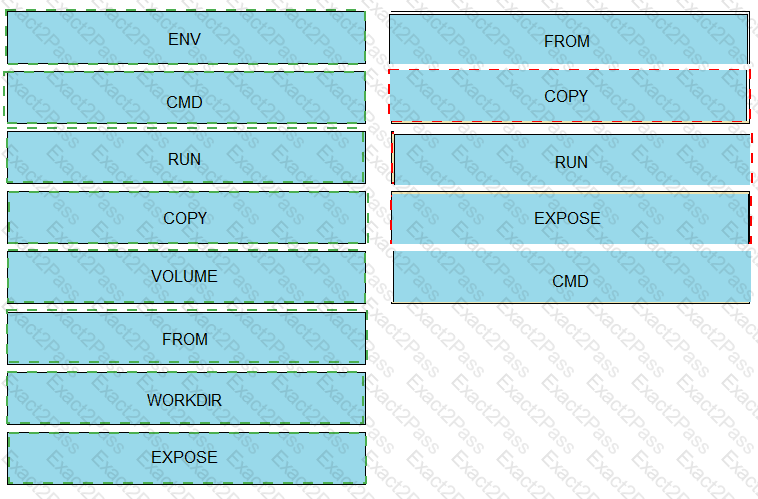
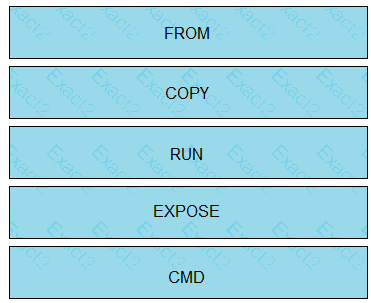
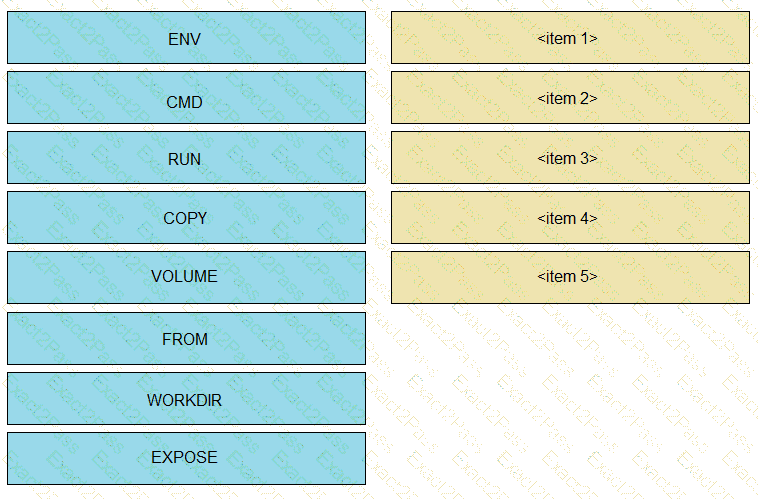
Refer to the exhibit.
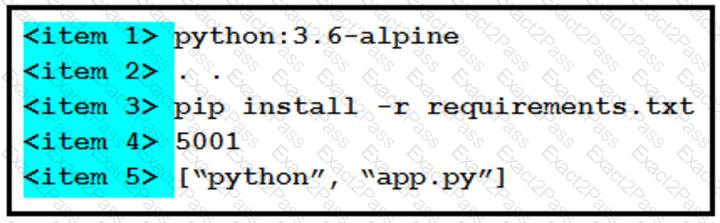
Drag and drop the correct parts of the Dockerfile from the left onto the item numbers on the right that match the missing sections in the exhibit to complete the Dockerfile to successfully build and deploy a container running a Python application. Not all parts of the Dockerfile are used.
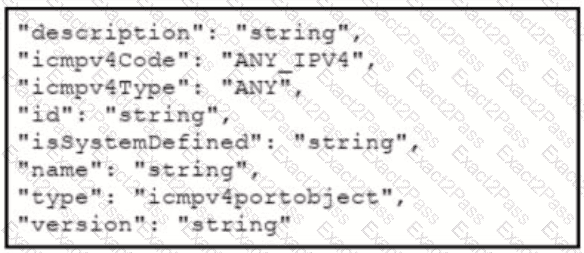
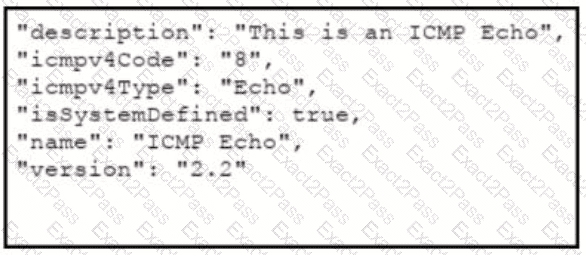
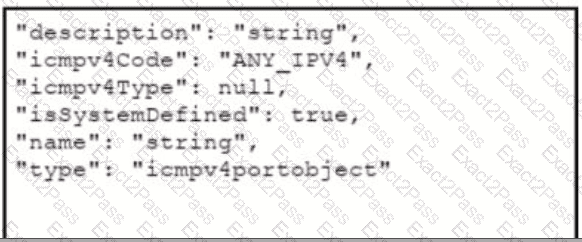
Refer to the exhibits which show the documentation associated with the create port object API cafl in Cisco Firepower Threat Defense, and a cURL command. Which data payload completes the cURL command to run the APi call?
A)
B)
C)
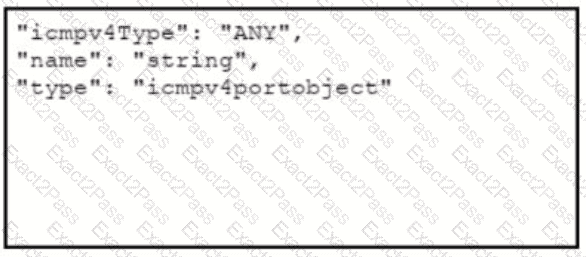
D)
What are two methods for sending bearer access tokens in resource requests to servers? (Choose two,)
While building a network automation tool, developers determined that mutual TLS authentication is required for secure communication. The process must ensure that server-side certificates are validated and accepted by the systems under automation. All data exchanges must be confidential and tamper-resistant during each workflow. Which task introduces safeguards to protect sensitive exchanges during the automation process?
Why is end-to-end encryption deployed when exposing sensitive data through APIs?
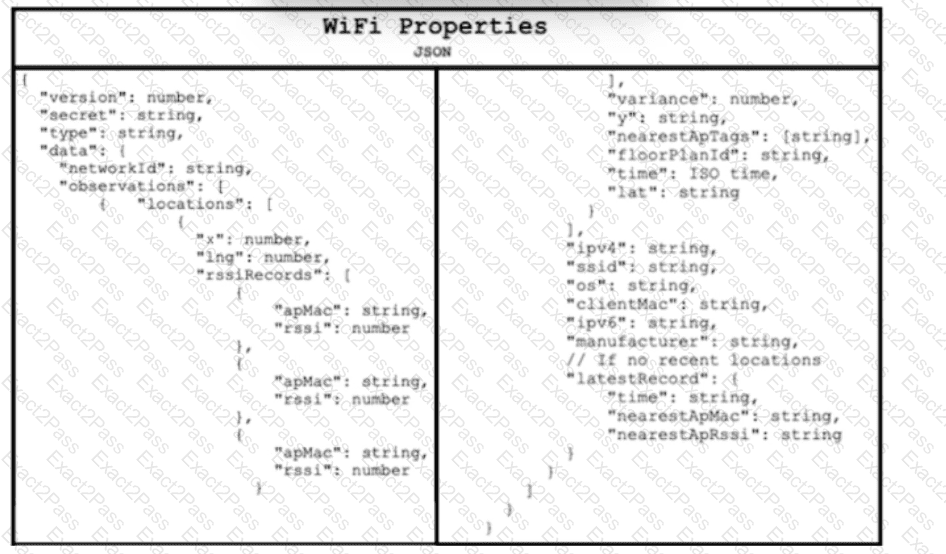
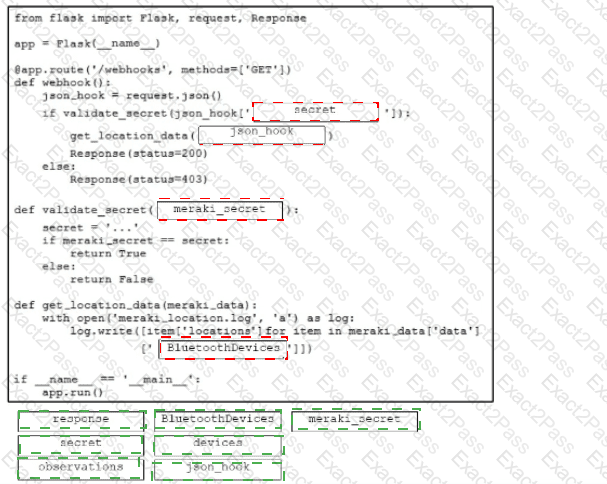
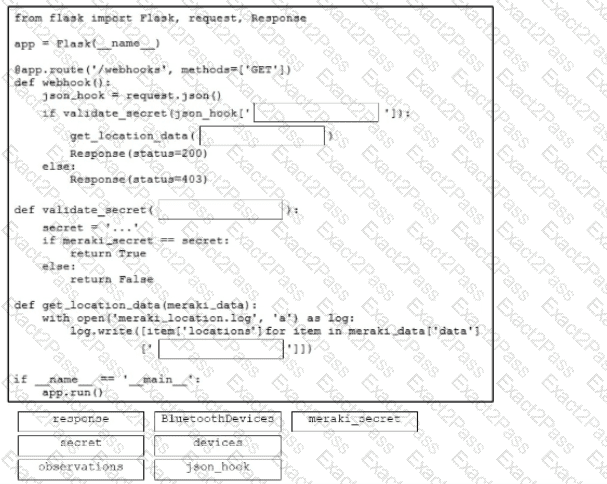
Refer to the exhibit. Drag and drop the code snippets from the bottom onto the blanks in the Python script to retrieve location data from the Cisco Meraki Location API by using a webhook receiver. Not all options are used.
A new network automation platform is being deployed, and detailed diagnostic data must be captured. The logging framework needs to be set up to facilitate quick detection of anomalies for specialized event traceability. The platform also must integrate seamlessly with an external log aggregator without introducing latency. Which configuration must be implemented to meet the requirements?
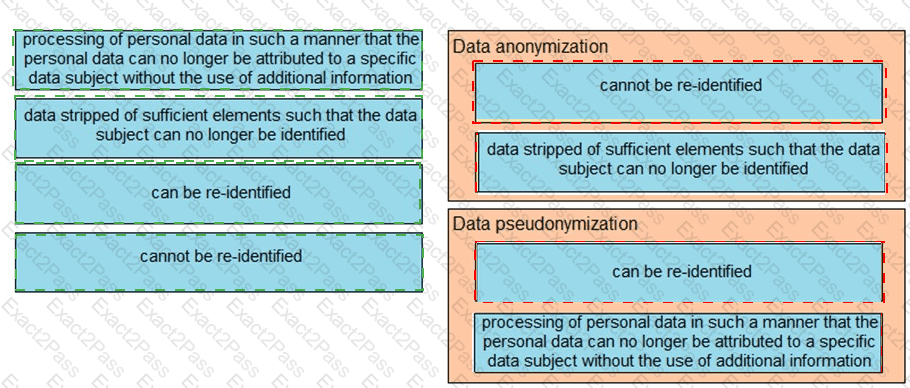
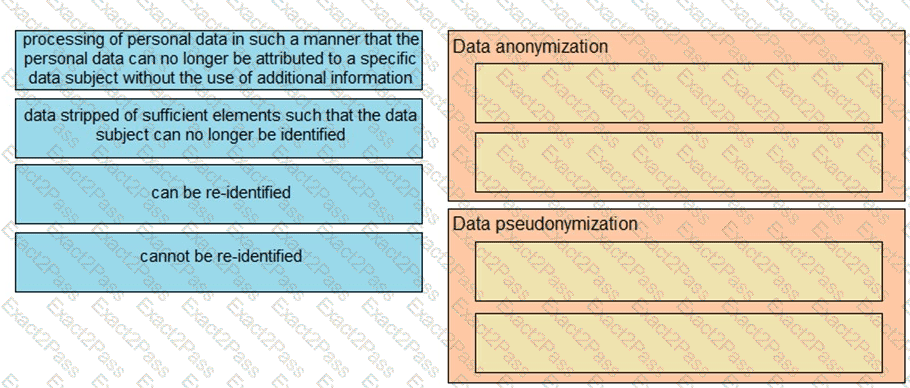
Drag and drop the characteristics from the left onto the correct data processing techniques on the right, in the context of GDPR.
Which two methods are API security best practices? (Choose two.)
Refer to the exhibit.
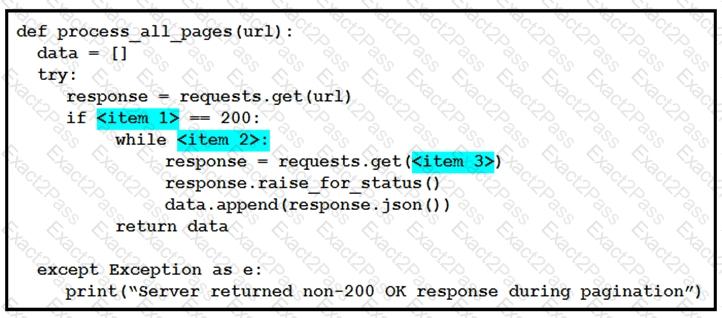
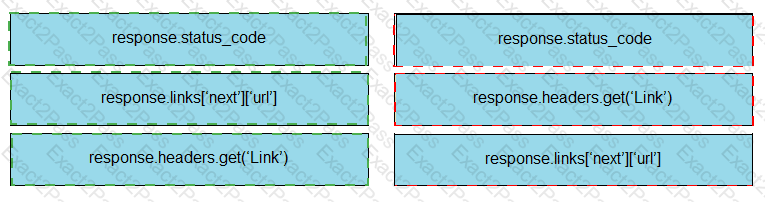
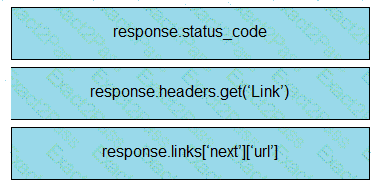
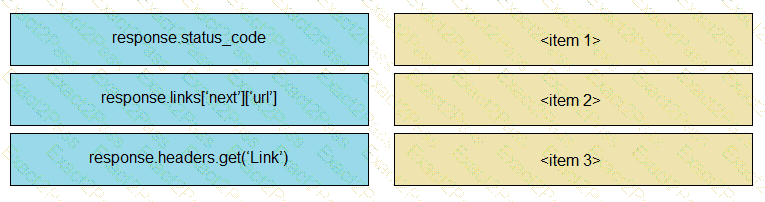
Drag and drop the parts of the Python code from the left onto the item numbers on the right that match the missing sections in the exhibit that consumes REST API pagination.
How are end-to-end encryption principles applied to API usage?
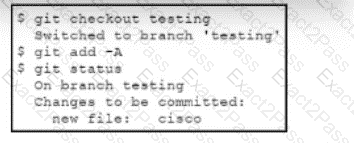
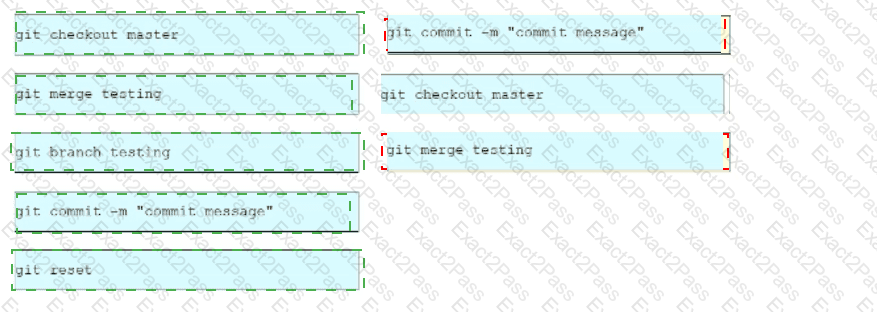
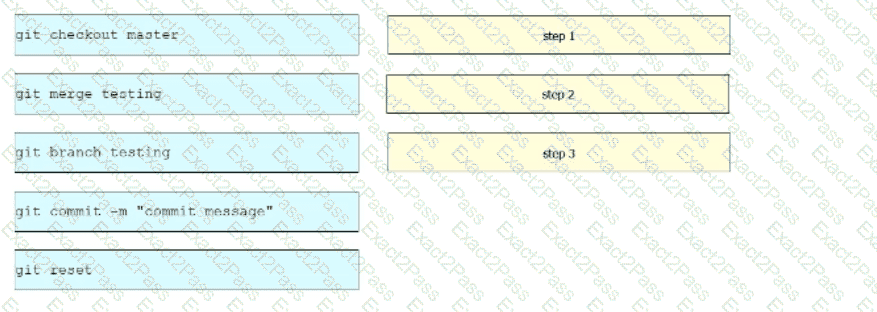
Refer to the exhibit. A new file named Cisco is added to a branch named testing, but it has not been committed. Drag and drop the Git commands from the left into the order on the right to merge the testing branch, with the new Cisco frte. into the master branch. Not all options are used.
What are two benefits of using a centralized logging service? (Choose two.)
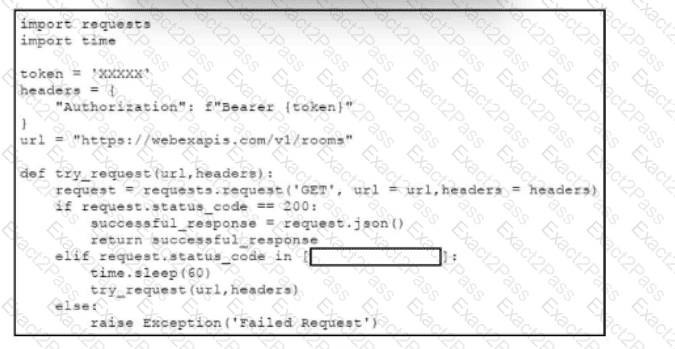
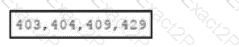
Refer to the exhibit. An engineer creates a function that gathers information from the Cisco Webex RESTful API. To enable increased durability, the engineer needs to implement a retry mechanism that pauses the scrip1 and retries the request it specific response codes are received. Which code snippet must be placed in the blank in the code to meet this requirement?
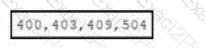
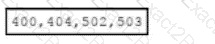
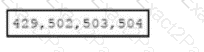
A developer has created an application based on customer requirements. The customer needs to run the application with the minimum downtime. Which design approach regarding high-availability applications, Recovery Time Objective, and Recovery Point Objective must be taken?