Exact2Pass

Modern security operations center (SOC) environments require immediate threat detection, behavioral anomaly correlation, and automated incident containment across multi-cloud and hybrid networks. Enterprise cybersecurity analysts must analyze real-time packet streams, identify evasive advanced persistent threat (APT) tactics, and manage vulnerability lifecycles under strict compliance standards. CompTIA established the CySA+ certification track to validate an analyst's ability to combat cyber threats using continuous security monitoring and intelligence-led defense strategies.
Passing the CS0-003 examination requires practical analytical competence rather than passive terminology memorization. Relying on static study sheets or high-yield cs0-003 exam questions leaves candidates unprepared for complex Performance-Based Questions (PBQs) that require interpreting SIEM alert outputs, analyzing PCAP packet captures in Wireshark, or configuring firewall remediation rules. Sourcing an updated comptia cysa cs0-003 study guide alongside realistic lab simulations ensures you build the diagnostic skills needed to score at least 750 on the official 100–900 scale. Exact2Pass provides calibrated, scenario-based practice tests that mirror official CompTIA assessment standards, helping you succeed on your first attempt.
The CS0-003 examination challenges your technical capacity to monitor infrastructure, prioritize enterprise vulnerabilities, and execute coordinated incident response procedures. Our practice tests replicate realistic terminal logs, Nmap scan outputs, and SIEM correlation queries instead of simple factual questionnaires. Practicing within timed simulations builds the analytical speed and diagnostic precision necessary to master both multiple-choice and multi-step performance-based questions under the 165-minute limit.
A technician is analyzing output from a popular network mapping tool for a PCI audit:
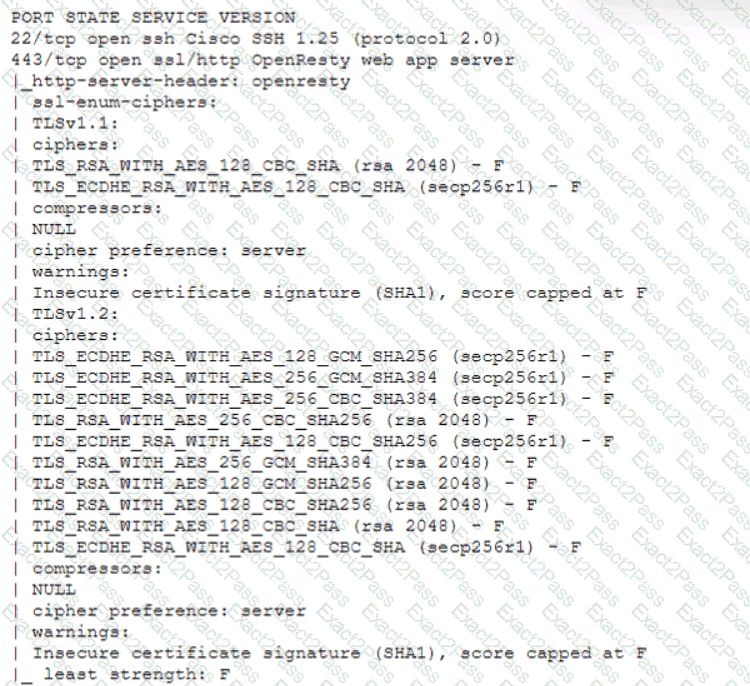
Which of the following best describes the output?
During an incident, analysts need to rapidly investigate by the investigation and leadership teams. Which of the following best describes how PII should be safeguarded during an incident?
A new SOC manager reviewed findings regarding the strengths and weaknesses of the last tabletop exercise in order to make improvements. Which of the following should the SOC manager utilize to improve the process?
A web application has a function to retrieve content from an internal URL to identify CSRF attacks in the logs. The security analyst is building a regular expression that will filter out the correctly formatted requests. The target URL is https://10.1.2.3/api, and the receiving API only accepts GET requests and uses a single integer argument named " id. " Which of the following regular expressions should the analyst use to achieve the objective?
Which of the following is best suited for determining the methods of an adversary?
Which of the following is the best framework for assessing how attackers use techniques over an infrastructure to exploit a target’s information assets?
A Chief Information Security Officer (CISO) has determined through lessons learned and an associated after-action report that staff members who use legacy applications do not adequately understand how to differentiate between non-malicious emails and phishing emails. Which of the following should the CISO include in an action plan to remediate this issue?
A security analyst is trying to identify anomalies on the network routing. Which of the following functions can the analyst use on a shell script to achieve the objective most accurately?
Which of the following would an organization use to develop a business continuity plan?
The Chief Information Security Officer for an organization recently received approval to install a new EDR solution. Following the installation, the number of alerts that require remediation by an analyst has tripled. Which of the following should the organization utilize to best centralize the workload for the internal security team? (Select two).

