Exact2Pass

Modern security operations center (SOC) environments require immediate threat detection, behavioral anomaly correlation, and automated incident containment across multi-cloud and hybrid networks. Enterprise cybersecurity analysts must analyze real-time packet streams, identify evasive advanced persistent threat (APT) tactics, and manage vulnerability lifecycles under strict compliance standards. CompTIA established the CySA+ certification track to validate an analyst's ability to combat cyber threats using continuous security monitoring and intelligence-led defense strategies.
Passing the CS0-003 examination requires practical analytical competence rather than passive terminology memorization. Relying on static study sheets or high-yield cs0-003 exam questions leaves candidates unprepared for complex Performance-Based Questions (PBQs) that require interpreting SIEM alert outputs, analyzing PCAP packet captures in Wireshark, or configuring firewall remediation rules. Sourcing an updated comptia cysa cs0-003 study guide alongside realistic lab simulations ensures you build the diagnostic skills needed to score at least 750 on the official 100–900 scale. Exact2Pass provides calibrated, scenario-based practice tests that mirror official CompTIA assessment standards, helping you succeed on your first attempt.
The CS0-003 examination challenges your technical capacity to monitor infrastructure, prioritize enterprise vulnerabilities, and execute coordinated incident response procedures. Our practice tests replicate realistic terminal logs, Nmap scan outputs, and SIEM correlation queries instead of simple factual questionnaires. Practicing within timed simulations builds the analytical speed and diagnostic precision necessary to master both multiple-choice and multi-step performance-based questions under the 165-minute limit.
An employee is suspected of misusing a company-issued laptop. The employee has been suspended pending an investigation by human resources. Which of the following is the best step to preserve evidence?
Which of the following is an important aspect that should be included in the lessons-learned step after an incident?
An attacker recently gained unauthorized access to a financial institution ' s database, which contains confidential information. The attacker exfiltrated a large amount of data before being detected and blocked. A security analyst needs to complete a root cause analysis to determine how the attacker was able to gain access. Which of the following should the analyst perform first?
The security analyst received the monthly vulnerability report. The following findings were included in the report
• Five of the systems only required a reboot to finalize the patch application.
• Two of the servers are running outdated operating systems and cannot be patched
The analyst determines that the only way to ensure these servers cannot be compromised is to isolate them. Which of the following approaches will best minimize the risk of the outdated servers being compromised?
A security analyst has received an incident case regarding malware spreading out of control on a customer ' s network. The analyst is unsure how to respond. The configured EDR has automatically obtained a sample of the malware and its signature. Which of the following should the analyst perform next to determine the type of malware, based on its telemetry?
A SOC manager reviews metrics from the last four weeks to investigate a recurring availability issue. The manager finds similar events correlating to the times of the reported issues.
Which of the following methods would the manager most likely use to resolve the issue?
A security analyst performs a vulnerability scan. Given the following findings:
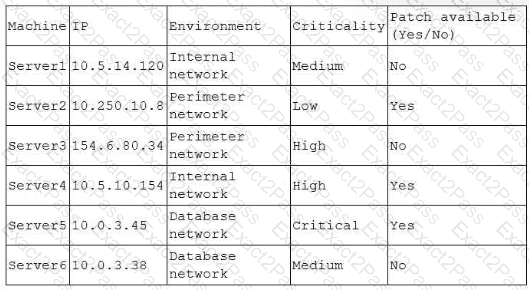
Which of the following machines should the analyst address first? (Select two).
A security team is concerned about recent Layer 4 DDoS attacks against the company website. Which of the following controls would best mitigate the attacks?
Which of the following are process improvements that can be realized by implementing a SOAR solution? (Select two).
A security analyst must preserve a system hard drive that was involved in a litigation request Which of the following is the best method to ensure the data on the device is not modified?

