Exact2Pass

Modern enterprise cloud security, regulatory risk governance, and digital identity defense require continuous operational visibility, Zero Trust architectural principles, and integrated compliance monitoring. As organizations accelerate digital transformation across Microsoft Azure, Microsoft 365, and multi-cloud environments, technology professionals and business stakeholders must maintain an accurate operational grasp of cloud defense mechanics. Earning the Microsoft Certified: Security, Compliance, and Identity Fundamentals designation proves your foundational competence across security controls, Microsoft Entra identity protections, Microsoft Defender threat detection, and Microsoft Purview data governance. However, many IT newcomers and security specialists hit a wall on this proctored 45-to-60-minute evaluation because they rely on simple buzzword memorization. Memorizing static answer keys or context-stripped question repositories found on unverified public forums cannot prepare you for the situational logic of matching specific Defender suite workloads to multi-tier attack vectors, configuring Conditional Access signal policies, or mapping regulatory compliance controls to automated Purview baselines.
True success on this scenario-driven fundamental assessment requires a comprehensive, multi-dimensional grasp of the shared responsibility model, defense-in-depth methodologies, and centralized SIEM and XDR incident correlation. Security practitioners must demonstrate sharp diagnostic judgment when evaluating user versus workload identity types in Microsoft Entra ID, interpreting Microsoft Sentinel analytics connectors, and identifying sensitivity labels or Data Loss Prevention (DLP) execution policies. Candidates frequently spend several months searching for high-yield sc-900 exam questions online, hoping to locate an updated microsoft security compliance and identity fundamentals sc-900 study guide to measure their operational readiness, or reviewing Microsoft Learn modules to verify identity governance definitions. Without interactive workspace software, a structured cloud security fundamentals course, or targeted practical simulator practice that can provide actual help in exam preparation, passive reading fails to build the diagnostic capabilities needed to handle real-world service mapping or isolate cloud posture misconfigurations. At Exact2Pass, our premium preparation workspace simulates real Microsoft Defender XDR security dashboards, Microsoft Entra admin centers, and Purview compliance portals, ensuring you score comfortably above the required 700 threshold on your very first try.
The SC-900 certification exam evaluates your real-world understanding of foundational security, compliance, and identity paradigms across modern enterprise cloud ecosystems. Our realistic simulation platform replicates active Microsoft 365 Defender security portals, Microsoft Entra ID access review consoles, and real-time Purview compliance manager scorecards instead of serving up generic questionnaires. You will master the underlying Zero Trust pillars, operator-driven threat hunting queries, and governance-level service dependencies of the active Microsoft ecosystem, preparing you to tackle any scenario-based fundamental question with ease.
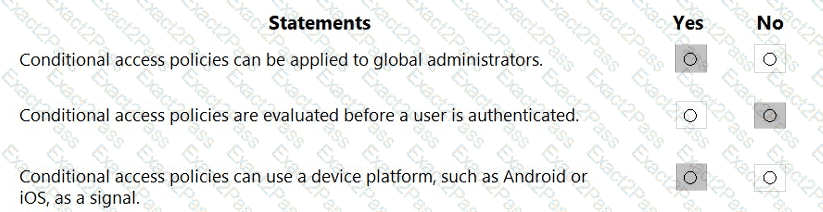
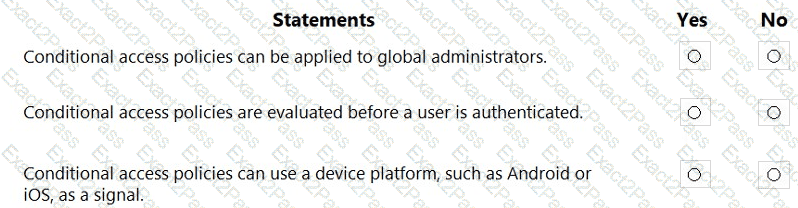
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Microsoft 365 Endpoint data loss prevention (Endpoint DLP) can be used on which operating systems?
You plan to implement a security strategy and place multiple layers of defense throughout a network infrastructure.
Which security methodology does this represent?
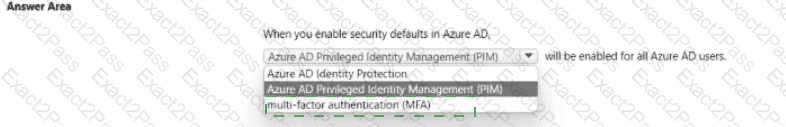
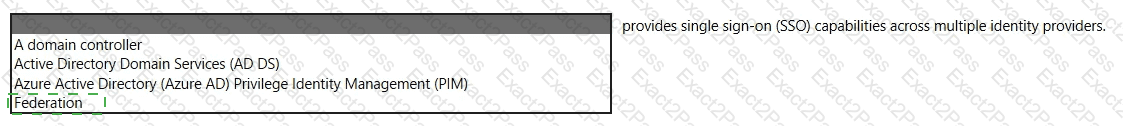
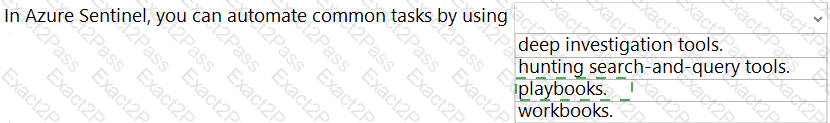
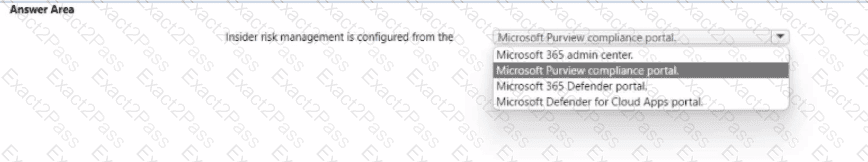
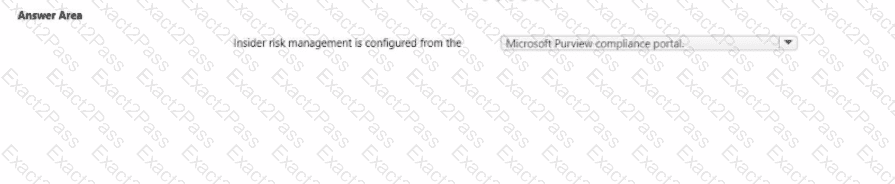
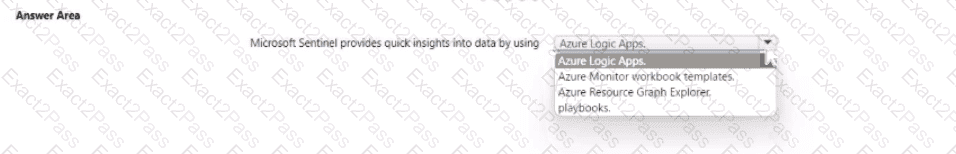
Select the answer that correctly completes the sentence.
Which feature is included in Microsoft Entra ID Governance?
Which statement represents a Microsoft privacy principle?
Which three authentication methods can Microsoft Entra users use to reset their password? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
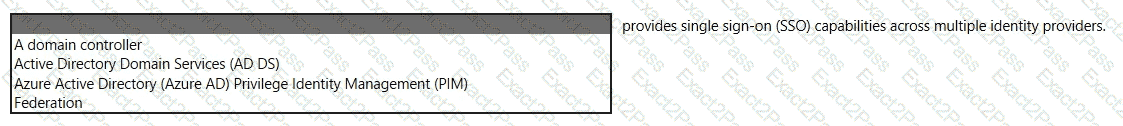
Select the answer that correctly completes the sentence.
What should you use to ensure that the members of an Azure Active Directory group use multi-factor authentication (MFA) when they sign in?
When security defaults are enabled for an Azure Active Directory (Azure AD) tenant, which two requirements are enforced? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.