Exact2Pass

Modern security operations center (SOC) environments require immediate threat detection, behavioral anomaly correlation, and automated incident containment across multi-cloud and hybrid networks. Enterprise cybersecurity analysts must analyze real-time packet streams, identify evasive advanced persistent threat (APT) tactics, and manage vulnerability lifecycles under strict compliance standards. CompTIA established the CySA+ certification track to validate an analyst's ability to combat cyber threats using continuous security monitoring and intelligence-led defense strategies.
Passing the CS0-003 examination requires practical analytical competence rather than passive terminology memorization. Relying on static study sheets or high-yield cs0-003 exam questions leaves candidates unprepared for complex Performance-Based Questions (PBQs) that require interpreting SIEM alert outputs, analyzing PCAP packet captures in Wireshark, or configuring firewall remediation rules. Sourcing an updated comptia cysa cs0-003 study guide alongside realistic lab simulations ensures you build the diagnostic skills needed to score at least 750 on the official 100–900 scale. Exact2Pass provides calibrated, scenario-based practice tests that mirror official CompTIA assessment standards, helping you succeed on your first attempt.
The CS0-003 examination challenges your technical capacity to monitor infrastructure, prioritize enterprise vulnerabilities, and execute coordinated incident response procedures. Our practice tests replicate realistic terminal logs, Nmap scan outputs, and SIEM correlation queries instead of simple factual questionnaires. Practicing within timed simulations builds the analytical speed and diagnostic precision necessary to master both multiple-choice and multi-step performance-based questions under the 165-minute limit.
An older CVE with a vulnerability score of 7.1 was elevated to a score of 9.8 due to a widely available exploit being used to deliver ransomware. Which of the following factors would an analyst most likely communicate as the reason for this escalation?
An analyst is reviewing a vulnerability report and must make recommendations to the executive team. The analyst finds that most systems can be upgraded with a reboot resulting in a single downtime window. However, two of the critical systems cannot be upgraded due to a vendor appliance that the company does not have access to. Which of the following inhibitors to remediation do these systems and associated vulnerabilities best represent?
A security analyst needs to develop a solution to protect a high-value asset from an exploit like a recent zero-day attack. Which of the following best describes this risk management strategy?
A company patches its servers using automation software. Remote SSH or RDP connections are allowed to the servers only from the service account used by the automation software. All servers are in an internal subnet without direct access to or from the internet. An analyst reviews the following vulnerability summary:
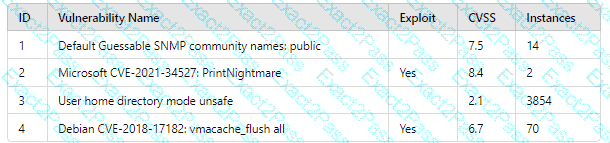
Which of the following vulnerability IDs should the analyst address first?
An analyst has discovered the following suspicious command:
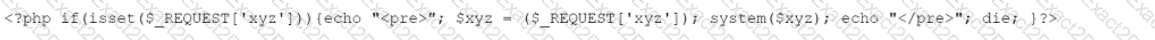
Which of the following would best describe the outcome of the command?
A list of loCs released by a government security organization contains the SHA-256 hash for a Microsoft-signed legitimate binary, svchost. exe. Which of the following best describes the result if security teams add this indicator to their detection signatures?
Which of the following explains how MTTD can affect IR reporting and communication?
An analyst wants to detect outdated software packages on a server. Which of the following methodologies will achieve this objective?
Which of the following does " federation " most likely refer to within the context of identity and access management?
Which of the following is the best metric for an organization to focus on given recent investments in SIEM, SOAR, and a ticketing system?

