Exact2Pass

Modern security operations center (SOC) environments require immediate threat detection, behavioral anomaly correlation, and automated incident containment across multi-cloud and hybrid networks. Enterprise cybersecurity analysts must analyze real-time packet streams, identify evasive advanced persistent threat (APT) tactics, and manage vulnerability lifecycles under strict compliance standards. CompTIA established the CySA+ certification track to validate an analyst's ability to combat cyber threats using continuous security monitoring and intelligence-led defense strategies.
Passing the CS0-003 examination requires practical analytical competence rather than passive terminology memorization. Relying on static study sheets or high-yield cs0-003 exam questions leaves candidates unprepared for complex Performance-Based Questions (PBQs) that require interpreting SIEM alert outputs, analyzing PCAP packet captures in Wireshark, or configuring firewall remediation rules. Sourcing an updated comptia cysa cs0-003 study guide alongside realistic lab simulations ensures you build the diagnostic skills needed to score at least 750 on the official 100–900 scale. Exact2Pass provides calibrated, scenario-based practice tests that mirror official CompTIA assessment standards, helping you succeed on your first attempt.
The CS0-003 examination challenges your technical capacity to monitor infrastructure, prioritize enterprise vulnerabilities, and execute coordinated incident response procedures. Our practice tests replicate realistic terminal logs, Nmap scan outputs, and SIEM correlation queries instead of simple factual questionnaires. Practicing within timed simulations builds the analytical speed and diagnostic precision necessary to master both multiple-choice and multi-step performance-based questions under the 165-minute limit.
A security analyst reviews the latest vulnerability scans and observes there are vulnerabilities with similar CVSSv3 scores but different base score metrics. Which of the following attack vectors should the analyst remediate first?
A security program was able to achieve a 30% improvement in MTTR by integrating security controls into a SIEM. The analyst no longer had to jump between tools. Which of the following best describes what the security program did?
A security analyst reviews the following results of a Nikto scan:
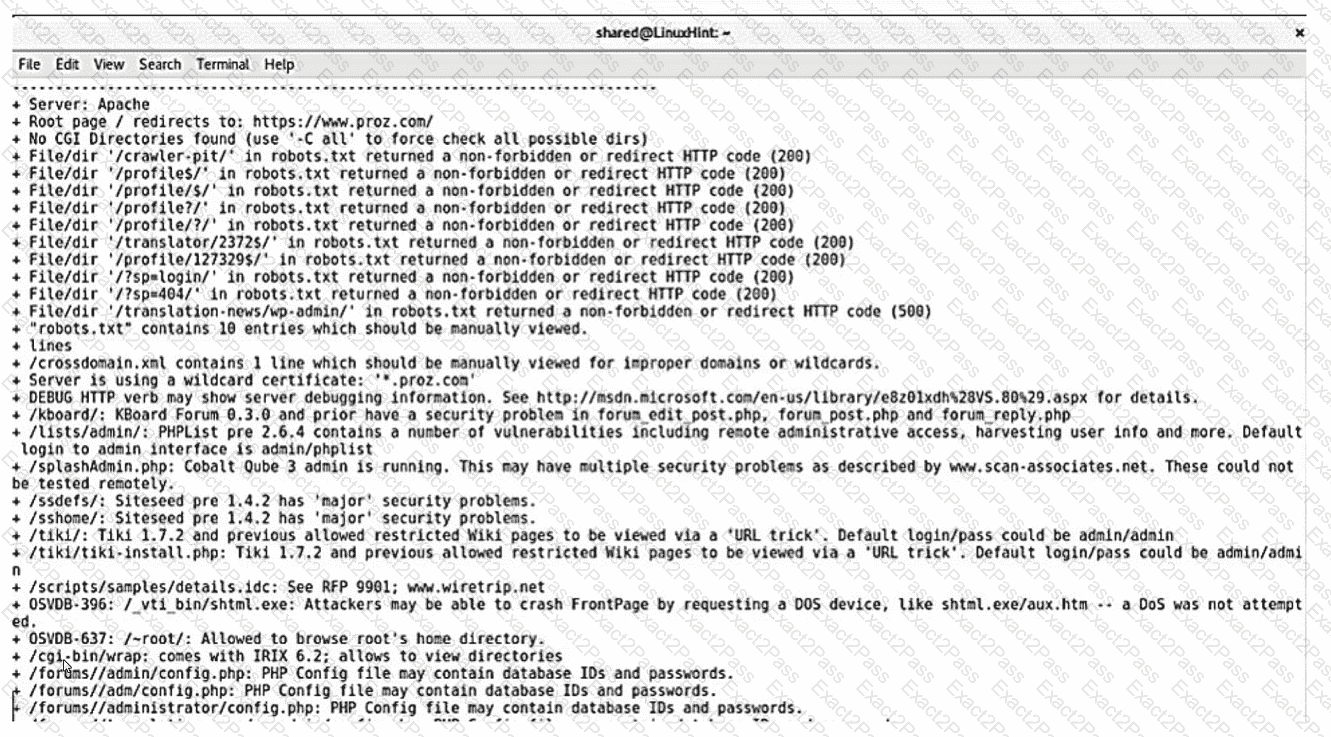
Which of the following should the security administrator investigate next?
A security analyst is reviewing events that occurred during a possible compromise. The analyst obtains the following log:
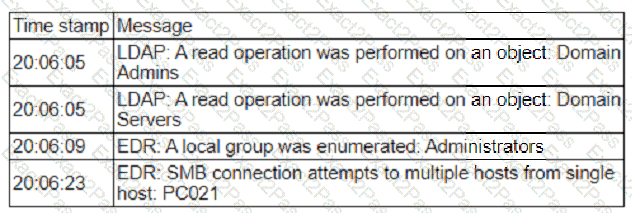
Which of the following is most likely occurring, based on the events in the log?
A cybersecurity analyst is reviewing SIEM logs and observes consistent requests originating from an internal host to a blocklisted external server. Which of the following best describes the activity that is
taking place?
Which of the following would help an analyst to quickly find out whether the IP address in a SIEM alert is a known-malicious IP address?
Which of the following in the digital forensics process is considered a critical activity that often includes a graphical representation of process and operating system events?
A vulnerability analyst is writing a report documenting the newest, most critical vulnerabilities identified in the past month. Which of the following public MITRE repositories would be best to review?
Which of the following best explains the importance of utilizing an incident response playbook?
A zero-day command injection vulnerability was published. A security administrator is analyzing the following logs for evidence of adversaries attempting to exploit the vulnerability:
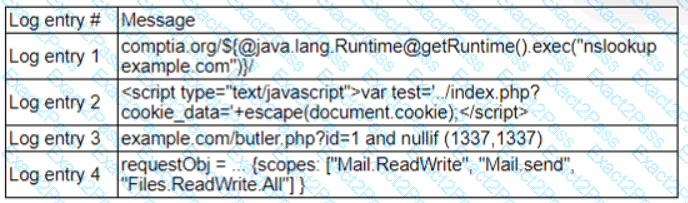
Which of the following log entries provides evidence of the attempted exploit?

