Exact2Pass
Last Update 20 hours ago Total Questions : 801
The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) content is now fully updated, with all current exam questions added 20 hours ago. Deciding to include 350-701 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 350-701 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-701 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) practice test comfortably within the allotted time.
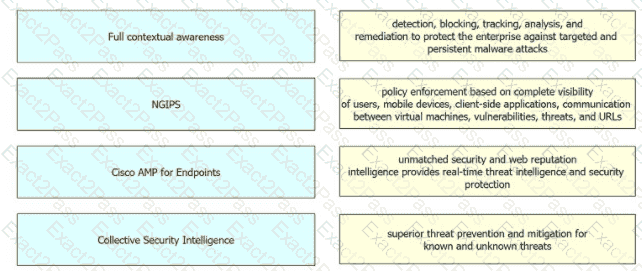
Drag and drop the security solutions from the left onto the benefits they provide on the right.
An engineer notices traffic interruption on the network. Upon further investigation, it is learned that broadcast
packets have been flooding the network. What must be configured, based on a predefined threshold, to
address this issue?
Which technology must De used to Implement secure VPN connectivity among company branches over a private IP cloud with any-to-any scalable connectivity?
An engineer is adding a Cisco DUO solution to the current TACACS+ deployment using Cisco ISE. The engineer wants to authenticate users using their account when they log into network devices. Which action accomplishes this task?
A Cisco AMP for Endpoints administrator configures a custom detection policy to add specific MD5 signatures The configuration is created in the simple detection policy section, but it does not work What is the reason for this failure?
A network engineer must create an access control list on a Cisco Adaptive Security Appliance firewall. The access control list must permit HTTP traffic to the internet from the organization ' s inside network 192.168.1.0/24. Which IOS command must oe used to create the access control list?
What must be enabled to secure SaaS-based applications?
Refer to the exhibit.
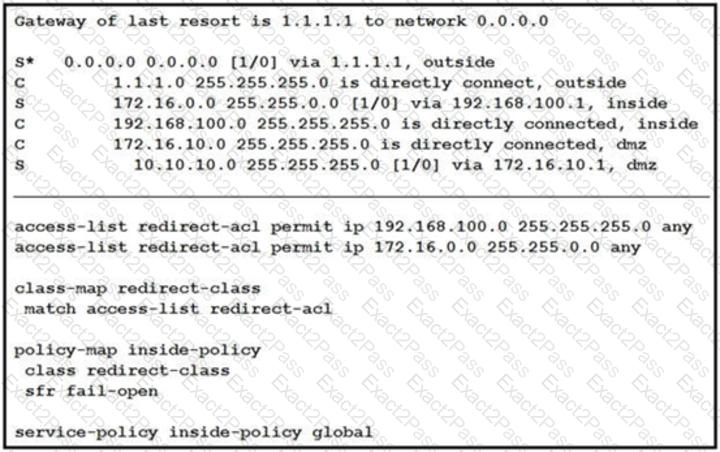
What is a result of the configuration?
A network administrator is setting up Cisco FMC to send logs to Cisco Security Analytics and Logging (SaaS). The network administrator is anticipating a high volume of logging events from the firewalls and wants lo limit the strain on firewall resources. Which method must the administrator use to send these logs to Cisco Security Analytics and Logging?
A user has a device in the network that is receiving too many connection requests from multiple machines.
Which type of attack is the device undergoing?
What is the purpose of the Cisco Endpoint loC feature?
A networking team must harden an organization ' s network from VLAN hopping attacks. The team disables Dynamic Trunking Protocol and puts any unused ports in an unused VLAN. A trunk port is used as a trunk link. What must the team configure next to harden the network against VLAN hopping attacks?
Which two configurations must be made on Cisco ISE and on Cisco TrustSec devices to force a session to be adjusted after a policy change is made? (Choose two)
What is the purpose of the Cisco Endpoint IoC feature?
A network administrator configures Dynamic ARP Inspection on a switch. After Dynamic ARP Inspection is applied, all users on that switch are unable to communicate with any destination. The network administrator checks the interface status of all interfaces, and there is no err-disabled interface. What is causing this problem?