Exact2Pass
Last Update 20 hours ago Total Questions : 801
The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) content is now fully updated, with all current exam questions added 20 hours ago. Deciding to include 350-701 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 350-701 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-701 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) practice test comfortably within the allotted time.
An organization is implementing AAA for their users. They need to ensure that authorization is verified for every command that is being entered by the network administrator. Which protocol must be configured in order to provide this capability?
What is the recommendation in a zero-trust model before granting access to corporate applications and resources?
An organization is using DNS services for their network and want to help improve the security of the DNS infrastructure. Which action accomplishes this task?
Which feature is configured for managed devices in the device platform settings of the Firepower Management
Center?
How does a WCCP-configured router identify if the Cisco WSA is functional?
Which two request of REST API are valid on the Cisco ASA Platform? (Choose two)
Refer to the exhibit.
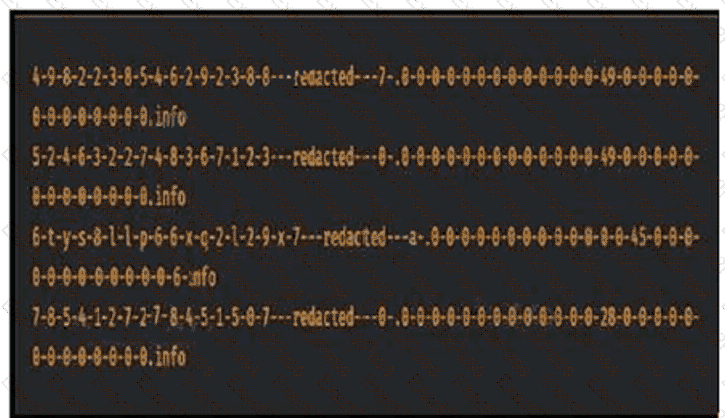
Consider that any feature of DNS requests, such as the length off the domain name
and the number of subdomains, can be used to construct models of expected behavior to which
observed values can be compared. Which type of malicious attack are these values associated with?
A security policy administrator configures a Cisco Secure Access SIA DNS policy to block all social media categories for the Marketing Active Directory group. While testing from one of the user machines, access to the domain https://socialmediaexample.org is allowed. When searching for this domain in User Activity Search, no queries for that specific domain are returned. Consider these facts:
The test user is part of the Marketing Active Directory group.
The domain socialmediaexample.org belongs to the social media category.
The user is configured with the Umbrella Roaming Client for DNS redirection.
All other social media websites are properly blocked for the same user and match the correct policy.
Which configuration must the administrator implement in Cisco Secure Access to meet the requirement?
What does Cisco ISE use to collect endpoint attributes that are used in profiling?
Which configuration method provides the options to prevent physical and virtual endpoint devices that are in the same base EPG or uSeg from being able to communicate with each other with Vmware VDS or Microsoft vSwitch?
How does Cisco Workload Optimization Manager help mitigate application performance issues?
Which attack is commonly associated with C and C++ programming languages?
Refer to the exhibit.
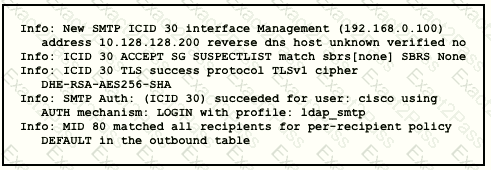
Which type of authentication is in use?
What are two characteristics of Cisco DNA Center APIs? (Choose two)
An engineer must force an endpoint to re-authenticate an already authenticated session without disrupting the
endpoint to apply a new or updated policy from ISE. Which CoA type achieves this goal?