Exact2Pass
Last Update 20 hours ago Total Questions : 801
The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) content is now fully updated, with all current exam questions added 20 hours ago. Deciding to include 350-701 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 350-701 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-701 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) practice test comfortably within the allotted time.
Which action controls the amount of URI text that is stored in Cisco WSA logs files?
Which method of attack is used by a hacker to send malicious code through a web application to an unsuspecting user to request that the victim ' s web browser executes the code?
Which protocol does Cisco Duo use to transport authentication assertions for single sign-on?
What are two ways that Cisco Container Platform provides value to customers who utilize cloud service providers? (Choose two.)
What is a characteristic of an EDR solution and not of an EPP solution?
Which type of API is being used when a security application notifies a controller within a software-defined network architecture about a specific security threat?
What is a function of the Layer 4 Traffic Monitor on a Cisco WSA?
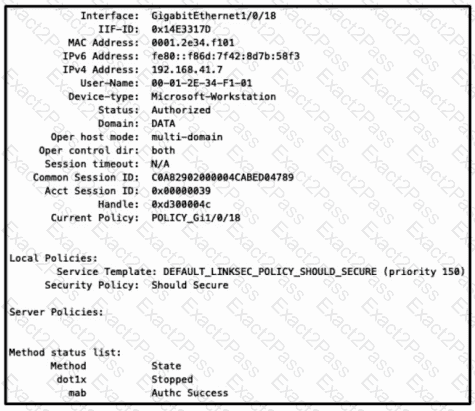
Refer to the exhibit. Which configuration item makes it possible to have the AAA session on the network?
What is a functional difference between Cisco Secure Endpoint and Cisco Umbrella Roaming Client?
Which policy represents a shared set of features or parameters that define the aspects of a managed device that are likely to be similar to other managed devices in a deployment?
Which two Cisco ISE components must be configured for BYOD? (Choose two.)
What is a language format designed to exchange threat intelligence that can be transported over the TAXII
protocol?
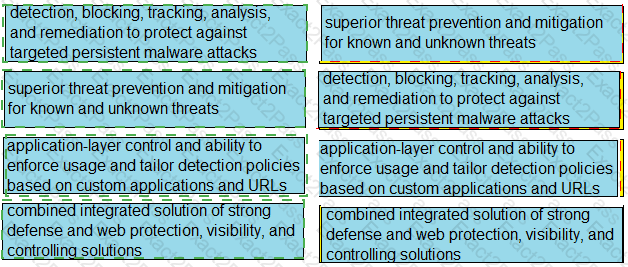
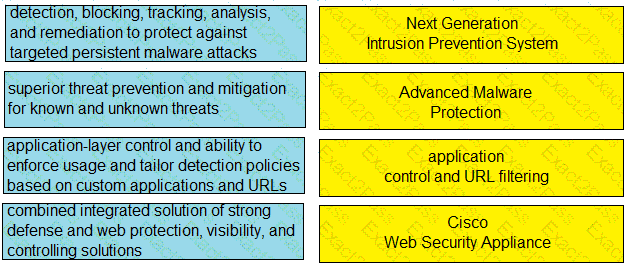
Drag and drop the capabilities from the left onto the correct technologies on the right.
A network administrator needs to find out what assets currently exist on the network. Third-party systems need to be able to feed host data into Cisco Firepower. What must be configured to accomplish this?
A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:
Matching IKEv2 proposals, preshared keys, and IPsec transform sets
Access control rules permitting the traffic
Crypto maps applied to the outside interfaces
VPN traffic exempted from inspection
During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?