Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: buysanta

Exact2Pass Menu

Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)

Last Update 20 hours ago Total Questions : 801

The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) content is now fully updated, with all current exam questions added 20 hours ago. Deciding to include 350-701 practice exam questions in your study plan goes far beyond basic test preparation.

You'll find that our 350-701 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-701 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) practice test comfortably within the allotted time.

Question # 121

An engineer is implementing NAC for LAN users on a segmented network. The engineer confirms that the device of each user is supported and the Cisco switch configuration is correct.

Which configuration should be made next to ensure there are no authentication issues?

A.

Disable the host firewall.

B.

Enable TACACS+ on the switch.

C.

Open TCP port 49.

D.

Permit UDP port 1812.

Question # 122

Which kind of API that is used with Cisco DNA Center provisions SSIDs, QoS policies, and update software versions on switches?

A.

Integration

B.

Intent

C.

Event

D.

Multivendor

Question # 123

In which scenario is endpoint-based security the solution?

A.

inspecting encrypted traffic

B.

device profiling and authorization

C.

performing signature-based application control

D.

inspecting a password-protected archive

Question # 124

A healthcare organization is deploying Cisco Secure Access to prevent protected health information from being shared with generative AI services. The security team requires real-time DLP inspection only for traffic destined for AI applications, with minimal false positives during general web browsing. The policy must permit tuning based on the proximity and match counts of PHI identifiers. Which configuration action must the engineer perform?

A.

Configure a real-time DLP rule referencing a built-in PHI data classification with default thresholds, scoped to a web profile that includes all Internet traffic.

B.

Implement an API-based DLP rule referencing a custom PHI data classification with tuned proximity and match-count thresholds, scoped to the generative AI application category.

C.

Deploy a real-time DLP rule referencing a built-in PHI data classification with tuned match-count thresholds, scoped to a web profile filtered by destination lists for known AI vendors.

D.

Apply a real-time DLP rule referencing a custom PHI data classification with tuned proximity and match-count thresholds, scoped to a web profile filtered by the generative AI application category.

Question # 125

What are two benefits of workload security? (Choose two.)

A.

Tracked application security

B.

Automated patching

C.

Reduced attack surface

D.

Scalable security policies

E.

Workload modeling

Question # 126

Which technology limits communication between nodes on the same network segment to individual applications?

A.

serverless infrastructure

B.

microsegmentation

C.

SaaS deployment

D.

machine-to-machine firewalling

Question # 127

Which two criteria must a certificate meet before the WSA uses it to decrypt application traffic? (Choose two.)

A.

It must include the current date.

B.

It must reside in the trusted store of the WSA.

C.

It must reside in the trusted store of the endpoint.

D.

It must have been signed by an internal CA.

E.

it must contain a SAN.

Question # 128

Which two statements about a Cisco WSA configured in Transparent mode are true? (Choose two)

A.

It can handle explicit HTTP requests.

B.

It requires a PAC file for the client web browser.

C.

It requires a proxy for the client web browser.

D.

WCCP v2-enabled devices can automatically redirect traffic destined to port 80.

E.

Layer 4 switches can automatically redirect traffic destined to port 80.

Question # 129

An engineer is configuring Cisco Secure Endpoint to enhance security by preventing the execution of certain files by users. The engineer needs to ensure that the specific executable file name Cisco_Software_0505446151.exe is blocked from running while never being quarantined. What must the engineer configure to meet the requirement?

A.

Create advanced custom detection list.

B.

Configure application control blocked applications list.

C.

Implement simple custom detection list.

D.

Enable scheduled scans to detect and block the executable files.

Question # 130

An engineer is implementing DHCP security mechanisms and needs the ability to add additional attributes to profiles that are created within Cisco ISE Which action accomplishes this task?

A.

Define MAC-to-lP address mappings in the switch to ensure that rogue devices cannot get an IP address

B.

Use DHCP option 82 to ensure that the request is from a legitimate endpoint and send the information to Cisco ISE

C.

Modify the DHCP relay and point the IP address to Cisco ISE.

D.

Configure DHCP snooping on the switch VLANs and trust the necessary interfaces

Question # 131

For Cisco IOS PKI, which two types of Servers are used as a distribution point for CRLs? (Choose two)

A.

SDP

B.

LDAP

C.

subordinate CA

D.

SCP

E.

HTTP

Question # 132

What is a difference between a DoS attack and a DDoS attack?

A.

A DoS attack is where a computer is used to flood a server with TCP and UDP packets whereas a DDoS attack is where multiple systems target a single system with a DoS attack

B.

A DoS attack is where a computer is used to flood a server with TCP and UDP packets whereas a DDoS attack is where a computer is used to flood multiple servers that are distributed over a LAN

C.

A DoS attack is where a computer is used to flood a server with UDP packets whereas a DDoS attack is where a computer is used to flood a server with TCP packets

D.

A DoS attack is where a computer is used to flood a server with TCP packets whereas a DDoS attack is where a computer is used to flood a server with UDP packets

Question # 133

An engineer must modify an existing remote access VPN using a Cisco AnyConnect Secure Mobility client solution and a Cisco Secure Firewall. Currently, all the traffic generate by the user Is sent to the VPN tunnel and the engineer must now exclude some servers and access them directly instead. Which element must be modified to achieve this goat?

A.

NAT exemption

B.

encryption domain

C.

routing table

D.

group policy

Question # 134

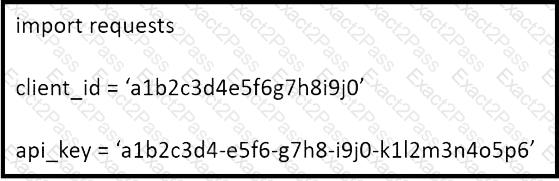
Refer to the exhibit.

What does the API key do while working with https://api.amp.cisco.com/v1/computers?

A.

displays client ID

B.

HTTP authorization

C.

Imports requests

D.

HTTP authentication

Question # 135

An engineer adds a custom detection policy to a Cisco AMP deployment and encounters issues with the

configuration. The simple detection mechanism is configured, but the dashboard indicates that the hash is not 64 characters and is non-zero. What is the issue?
A.

The engineer is attempting to upload a hash created using MD5 instead of SHA-256

B.

The file being uploaded is incompatible with simple detections and must use advanced detections

C.

The hash being uploaded is part of a set in an incorrect format

D.

The engineer is attempting to upload a file instead of a hash

Go to page: