Exact2Pass
Last Update 20 hours ago Total Questions : 801
The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) content is now fully updated, with all current exam questions added 20 hours ago. Deciding to include 350-701 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 350-701 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-701 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) practice test comfortably within the allotted time.
An engineer must implement an external application that authenticates against the Cisco Secure Email Threat Defense API to perform automated message searches. The application already presents a user bearer token, but the API requires an additional authentication header with each request. The engineer must configure the external application to include the required header alongside the bearer token so that the API calls are accepted. Which header must be configured?
What is the difference between EPP and EDR?
What is a benefit of using Cisco Tetration?
Which action must be taken in the AMP for Endpoints console to detect specific MD5 signatures on endpoints and then quarantine the files?
What does endpoint isolation in Cisco AMP for Endpoints security protect from?
A mall provides security services to customers with a shared appliance. The mall wants separation of
management on the shared appliance. Which ASA deployment mode meets these needs?
What is a capability of a Trojan horse on a computer system?
A security engineer must protect endpoints when a file appears harmless during initial inspection but later shows malicious behavior. The solution must continuously observe process and file activity after execution and respond when a threat emerges. The infrastructure includes Cisco Secure Endpoint. Which feature must the engineer configure to meet the requirements?
Which two risks is a company vulnerable to if it does not have a well-established patching solution for
endpoints? (Choose two)
When a Cisco Secure Web Appliance checks a web request, what occurs if it is unable to match a user-defined policy?
A large organization wants to deploy a security appliance in the public cloud to form a site-to-site VPN
and link the public cloud environment to the private cloud in the headquarters data center. Which Cisco
security appliance meets these requirements?
An engineer is securing access to data served by a cloud-based application. The data must be protected from modification in transit, and its integrity must be validated. The following security measures have been implemented:
• Governance with role-based access control based on the principle of least privilege
• TLS 1.3 with signed certificates
• AES-256 with MD5
What must be configured to complete the secure implementation?
Which Cisco Advanced Malware protection for Endpoints deployment architecture is designed to keep data
within a network perimeter?
What is the purpose of CA in a PKI?
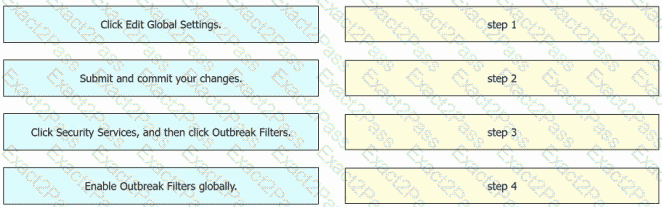
An engineer must enable Outbreak Filters globally on an AsyncOS for Cisco Secure Email Gateway to protect the network from large-scale malware attacks. Drag and drop the steps from the left into the sequence on the right to complete the configuration.