Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: buysanta

Exact2Pass Menu

Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)

Last Update 20 hours ago Total Questions : 801

The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) content is now fully updated, with all current exam questions added 20 hours ago. Deciding to include 350-701 practice exam questions in your study plan goes far beyond basic test preparation.

You'll find that our 350-701 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-701 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) practice test comfortably within the allotted time.

Question # 181

When Cisco and other industry organizations publish and inform users of known security findings and

vulnerabilities, which name is used?

A.

Common Security Exploits

B.

Common Vulnerabilities and Exposures

C.

Common Exploits and Vulnerabilities

D.

Common Vulnerabilities, Exploits and Threats

Question # 182

What is a difference between GETVPN and IPsec?

A.

GETVPN reduces latency and provides encryption over MPLS without the use of a central hub

B.

GETVPN provides key management and security association management

C.

GETVPN is based on IKEv2 and does not support IKEv1

D.

GETVPN is used to build a VPN network with multiple sites without having to statically configure all devices

Question # 183

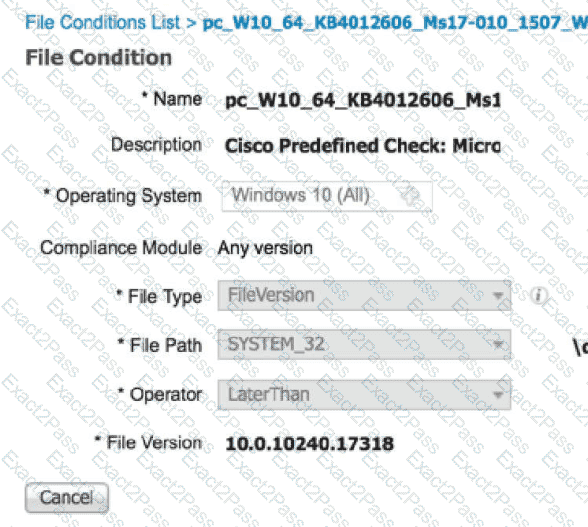
An engineer used a posture check on a Microsoft Windows endpoint and discovered that the MS17-010 patch

was not installed, which left the endpoint vulnerable to WannaCry ransomware. Which two solutions mitigate

the risk of this ransom ware infection? (Choose two)

A.

Configure a posture policy in Cisco Identity Services Engine to install the MS17-010 patch before allowingaccess on the network.

B.

Set up a profiling policy in Cisco Identity Service Engine to check and endpoint patch level before allowingaccess on the network.

C.

Configure a posture policy in Cisco Identity Services Engine to check that an endpoint patch level is metbefore allowing access on the network.

D.

Configure endpoint firewall policies to stop the exploit traffic from being allowed to run and replicatethroughout the network.

E.

Set up a well-defined endpoint patching strategy to ensure that endpoints have critical vulnerabilities patched in a timely fashion.

Question # 184

An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites

but other sites are not accessible due to an error. Why is the error occurring?

A.

Client computers do not have the Cisco Umbrella Root CA certificate installed.

B.

IP-Layer Enforcement is not configured.

C.

Client computers do not have an SSL certificate deployed from an internal CA server.

D.

Intelligent proxy and SSL decryption is disabled in the policy

Question # 185

Which RADIUS feature provides a mechanism to change the AAA attributes of a session after it is

authenticated?

A.

Authorization

B.

Accounting

C.

Authentication

D.

CoA

Question # 186

Which endpoint solution protects a user from a phishing attack?

A.

Cisco Identity Services Engine

B.

Cisco AnyConnect with ISE Posture module

C.

Cisco AnyConnect with Network Access Manager module

D.

Cisco AnyConnect with Umbrella Roaming Security module

Question # 187

A network engineer must migrate a Cisco WSA virtual appliance from one physical host to another physical host by using VMware vMotion. What is a requirement for both physical hosts?

A.

The hosts must run Cisco AsyncOS 10.0 or greater.

B.

The hosts must run different versions of Cisco AsyncOS.

C.

The hosts must have access to the same defined network.

D.

The hosts must use a different datastore than the virtual appliance.

Question # 188

Why would a user choose an on-premises ESA versus the CES solution?

A.

Sensitive data must remain onsite.

B.

Demand is unpredictable.

C.

The server team wants to outsource this service.

D.

ESA is deployed inline.

Question # 189

Which parameter is required when configuring a Netflow exporter on a Cisco Router?

A.

DSCP value

B.

Source interface

C.

Exporter name

D.

Exporter description

Question # 190

An engineer enabled SSL decryption for Cisco Umbrella intelligent proxy and needs to ensure that traffic is inspected without alerting end-users.

A.

Upload the organization root CA to the Umbrella admin portal

B.

Modify the user ' s browser settings to suppress errors from Umbrella.

C.

Restrict access to only websites with trusted third-party signed certificates.

D.

Import the Umbrella root CA into the trusted root store on the user ' s device.

Question # 191

Which Cisco security solution secures public, private, hybrid, and community clouds?

A.

Cisco ISE

B.

Cisco ASAv

C.

Cisco Cloudlock

D.

Cisco pxGrid

Question # 192

A network administrator is configuring a role in an access control policy to block certain URLs and selects the " Chat and instant Messaging " category. which reputation score should be selected to accomplish

this goal?

A.

3

B.

5

C.

10

D.

1

Question # 193

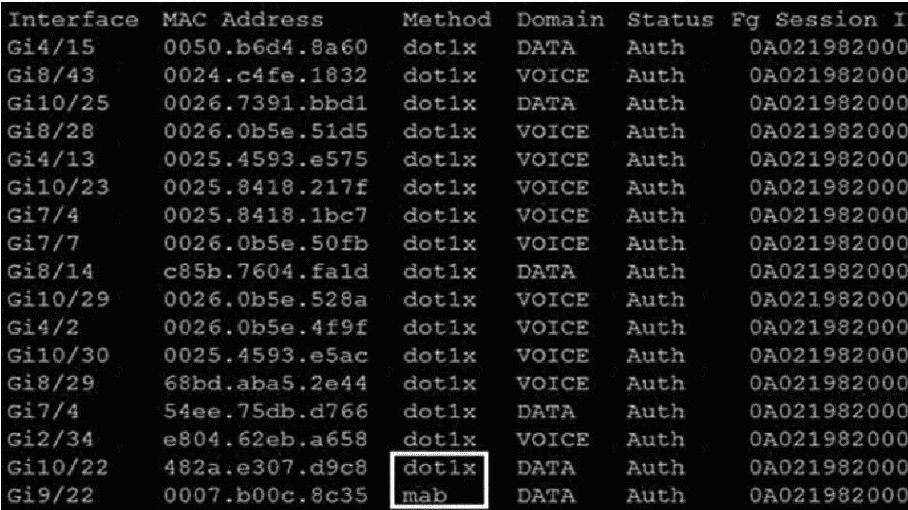
Refer to the exhibit.

Which command was used to generate this output and to show which ports are

authenticating with dot1x or mab?

A.

show authentication registrations

B.

show authentication method

C.

show dot1x all

D.

show authentication sessions

Question # 194

Which SNMPv3 configuration must be used to support the strongest security possible?

A.

asa-host(config)#snmp-server group myv3 v3 privasa-host(config)#snmp-server user andy myv3 auth sha cisco priv des ciscXXXXXXXXasa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy

B.

asa-host(config)#snmp-server group myv3 v3 noauthasa-host(config)#snmp-server user andy myv3 auth sha cisco priv aes 256 ciscXXXXXXXXasa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy

C.

asa-host(config)#snmpserver group myv3 v3 noauthasa-host(config)#snmp-server user andy myv3 auth sha cisco priv 3des ciscXXXXXXXXasa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy

D.

asa-host(config)#snmp-server group myv3 v3 privasa-host(config)#snmp-server user andy myv3 auth sha cisco priv aes 256 ciscXXXXXXXXasa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy

Question # 195

An organization must add new firewalls to its infrastructure and wants to use Cisco ASA or Cisco FTD.

The chosen firewalls must provide methods of blocking traffic that include offering the user the option to bypass the block for certain sites after displaying a warning page and to reset the connection. Which solution should the organization choose?
A.

Cisco FTD because it supports system rate level traffic blocking, whereas Cisco ASA does not

B.

Cisco ASA because it allows for interactive blocking and blocking with reset to be configured via the GUI, whereas Cisco FTD does not.

C.

Cisco FTD because it enables interactive blocking and blocking with reset natively, whereas Cisco ASA does not

D.

Cisco ASA because it has an additional module that can be installed to provide multiple blocking capabilities, whereas Cisco FTD does not.

Go to page: