Exact2Pass
Last Update 20 hours ago Total Questions : 801
The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) content is now fully updated, with all current exam questions added 20 hours ago. Deciding to include 350-701 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 350-701 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-701 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) practice test comfortably within the allotted time.
Which solution detects threats across a private network, public clouds, and encrypted traffic?
An organization has noticed an increase in malicious content downloads and wants to use Cisco Umbrella to prevent this activity for suspicious domains while allowing normal web traffic. Which action will accomplish this task?
Refer to the exhibit.
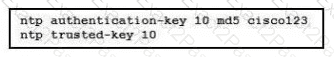
A network engineer is testing NTP authentication and realizes that any device synchronizes time with this router and that NTP authentication is not enforced What is the cause of this issue?
Which two global commands must the network administrator implement to limit the attack surface of an internet-facing Cisco router? (Choose two.)
An engineer needs behavioral analysis to detect malicious activity on the hosts, and is configuring the
organization’s public cloud to send telemetry using the cloud provider’s mechanisms to a security device. Which
mechanism should the engineer configure to accomplish this goal?
Which algorithm is an NGE hash function?
In a PaaS model, which layer is the tenant responsible for maintaining and patching?
What is the purpose of a denial-of-service attack?
Which attack type attempts to shut down a machine or network so that users are not able to access it?
A company wants to enforce security policy using Cisco Secure Access Secure Internet Access. The design requirements are:
Block adult-content and gambling categories for all users.
Inspect file downloads for malware.
Bypass TLS decryption for financial and healthcare domains because of compliance requirements.
Allow the Marketing department to use social media while keeping file scanning active for downloads from those sites.
Which two configuration actions must the engineer perform in Cisco Secure Access to meet the requirements? (Choose two.)
When using Cisco AMP for Networks which feature copies a file to the Cisco AMP cloud for analysis?
Which Secure Email Gateway implementation method segregates inbound and outbound email?
How does a Cisco Secure Firewall help to lower the risk of exfiltration techniques that steal customer data?
Client workstations are experiencing extremely poor response time. An engineer suspects that an attacker is eavesdropping and making independent connections while relaying messages between victims to make them think they are talking to each other over a private connection. Which feature must be enabled and configured to provide relief from this type of attack?
A logistics company issues corporate laptops that must automatically establish a Cisco Secure Client VPN tunnel whenever users are outside the office and connected to an untrusted external network. Cisco Secure Firewall Threat Defense is the VPN headend and is already configured with remote-access profiles, address pools, and a PKI that distributes both machine and user certificates to endpoints. Management requires the tunnel to come up unattended before any user signs in to a laptop. Device-based authentication must be used, and the client must distinguish the corporate LAN from outside networks. The VPN must be connected when a user is outside the corporate network. Which configuration action must be performed to meet the requirements?