Exact2Pass
Last Update 20 hours ago Total Questions : 801
The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) content is now fully updated, with all current exam questions added 20 hours ago. Deciding to include 350-701 practice exam questions in your study plan goes far beyond basic test preparation.
You'll find that our 350-701 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-701 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) practice test comfortably within the allotted time.
What is a difference between weak passwords and missing encryption?
Which security principle advocates rapid cryptographic algorithm replacement to defend against quantum-computing threats?
Drag and drop the exploits from the left onto the type of security vulnerability on the right.
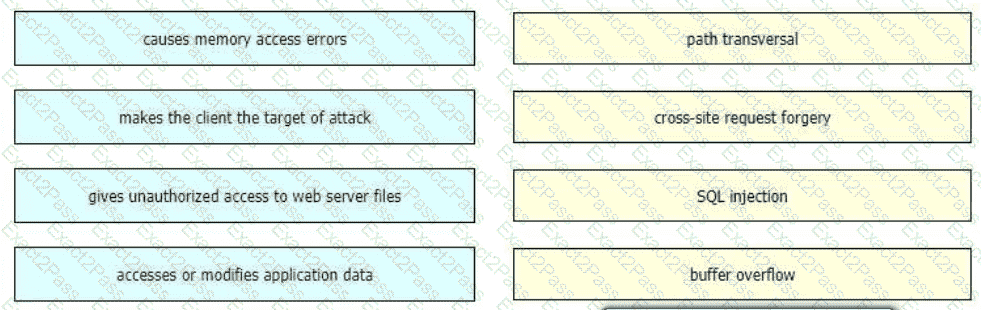
An organization has two systems in their DMZ that have an unencrypted link between them for communication.
The organization does not have a defined password policy and uses several default accounts on the systems.
The application used on those systems also have not gone through stringent code reviews. Which vulnerability
would help an attacker brute force their way into the systems?
An engineer implements Cisco CloudLock to secure a Microsoft Office 365 application in the cloud. The engineer must configure protection for corporate files in case of any incidents. Which two actions must be taken to complete the implementation? (Choose two.)
An organization wants to implement a cloud-delivered and SaaS-based solution to provide visibility and threat detection across the AWS network. The solution must be deployed without software agents and rely on AWS VPC flow logs instead. Which solution meets these requirements?
A network engineer entered the snmp-server user asmith myv7 auth sha cisco priv aes 256
cisc0xxxxxxxxx command and needs to send SNMP information to a host at 10.255.255.1. Which
command achieves this goal?
Refer to the exhibit. A network engineer must configure a Cisco router to send traps using SNMPv3. The engineer configures a remote user to receive traps and sets the security level to use authentication without privacy. Which command completes the configuration?
An organization is trying to improve their Defense in Depth by blocking malicious destinations prior to a
connection being established. The solution must be able to block certain applications from being used within the network. Which product should be used to accomplish this goal?
Which metric is used by the monitoring agent to collect and output packet loss and jitter information?
What is the function of the crypto is a kmp key cisc406397954 address 0.0.0.0 0.0.0.0 command when establishing an IPsec VPN tunnel?
Which method is used to deploy certificates and configure the supplicant on mobile devices to gain access to
network resources?
What is a benefit of performing device compliance?
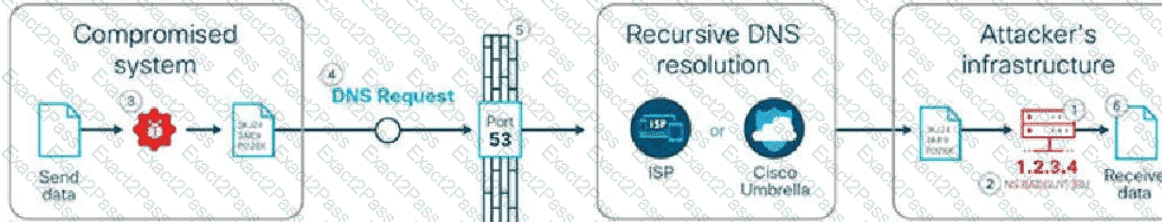
How is DNS tunneling used to exfiltrate data out of a corporate network?
Which solution allows an administrator to provision, monitor, and secure mobile devices on Windows and Mac computers from a centralized dashboard?