Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: buysanta

Exact2Pass Menu

Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)

Last Update 20 hours ago Total Questions : 801

The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) content is now fully updated, with all current exam questions added 20 hours ago. Deciding to include 350-701 practice exam questions in your study plan goes far beyond basic test preparation.

You'll find that our 350-701 exam questions frequently feature detailed scenarios and practical problem-solving exercises that directly mirror industry challenges. Engaging with these 350-701 sample sets allows you to effectively manage your time and pace yourself, giving you the ability to finish any Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) practice test comfortably within the allotted time.

Question # 76

Which feature enables a Cisco ISR to use the default bypass list automatically for web filtering?

A.

filters

B.

group key

C.

company key

D.

connector

Question # 77

Which encryption algorithm provides highly secure VPN communications?

A.

3DES

B.

AES 256

C.

AES 128

D.

DES

Question # 78

Which benefit is provided by ensuring that an endpoint is compliant with a posture policy configured in Cisco ISE?

A.

It allows the endpoint to authenticate with 802.1x or MAB.

B.

It verifies that the endpoint has the latest Microsoft security patches installed.

C.

It adds endpoints to identity groups dynamically.

D.

It allows CoA to be applied if the endpoint status is compliant.

Question # 79

What are two functions of IKEv1 but not IKEv2? (Choose two)

A.

NAT-T is supported in IKEv1 but rot in IKEv2.

B.

With IKEv1, when using aggressive mode, the initiator and responder identities are passed cleartext

C.

With IKEv1, mode negotiates faster than main mode

D.

IKEv1 uses EAP authentication

E.

IKEv1 conversations are initiated by the IKE_SA_INIT message

Question # 80

What is the difference between a vulnerability and an exploit?

A.

A vulnerability is a hypothetical event for an attacker to exploit

B.

A vulnerability is a weakness that can be exploited by an attacker

C.

An exploit is a weakness that can cause a vulnerability in the network

D.

An exploit is a hypothetical event that causes a vulnerability in the network

Question # 81

Which capability is exclusive to a Cisco AMP public cloud instance as compared to a private cloud instance?

A.

RBAC

B.

ETHOS detection engine

C.

SPERO detection engine

D.

TETRA detection engine

Question # 82

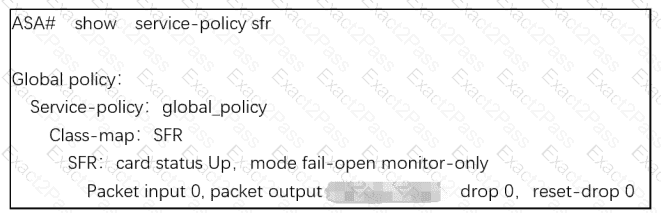
Refer to the exhibit.

What are two indications of the Cisco Firepower Services Module configuration?

(Choose two.)

A.

The module is operating in IDS mode.

B.

Traffic is blocked if the module fails.

C.

The module fails to receive redirected traffic.

D.

The module is operating in IPS mode.

E.

Traffic continues to flow if the module fails.

Question # 83

Which solution protects hybrid cloud deployment workloads with application visibility and segmentation?

A.

Nexus

B.

Stealthwatch

C.

Firepower

D.

Tetration

Question # 84

An engineer is trying to decide whether to use Cisco Umbrella, Cisco CloudLock, Cisco Stealthwatch, or Cisco AppDynamics Cloud Monitoring for visibility into data transfers as well as protection against data exfiltration Which solution best meets these requirements?

A.

Cisco CloudLock

B.

Cisco AppDynamics Cloud Monitoring

C.

Cisco Umbrella

D.

Cisco Stealthwatch

Question # 85

How does Cisco Umbrella protect clients when they operate outside of the corporate network?

A.

by modifying the registry for DNS lookups

B.

by using Active Directory group policies to enforce Cisco Umbrella DNS servers

C.

by using the Cisco Umbrella roaming client

D.

by forcing DNS queries to the corporate name servers

Question # 86

Where are individual sites specified to be block listed in Cisco Umbrella?

A.

Application settings

B.

Security settings

C.

Destination lists

D.

Content categories

Question # 87

What is a commonality between DMVPN and FlexVPN technologies?

A.

FlexVPN and DMVPN use IS-IS routing protocol to communicate with spokes

B.

FlexVPN and DMVPN use the new key management protocol

C.

FlexVPN and DMVPN use the same hashing algorithms

D.

IOS routers run the same NHRP code for DMVPN and FlexVPN

Question # 88

What is the function of Cisco Cloudlock for data security?

A.

data loss prevention

B.

controls malicious cloud apps

C.

detects anomalies

D.

user and entity behavior analytics

Question # 89

How does the Cisco WSA enforce bandwidth restrictions for web applications?
A.

It implements a policy route to redirect application traffic to a lower-bandwidth link.

B.

It dynamically creates a scavenger class QoS policy and applies it to each client that connects through the WSA.

C.

It sends commands to the uplink router to apply traffic policing to the application traffic.

D.

It simulates a slower link by introducing latency into application traffic.

Question # 90

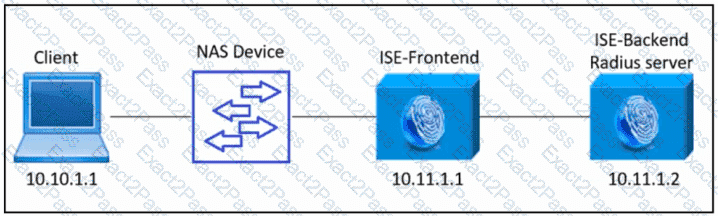
Refer to the exhibit. An engineer must configure a new Cisco ISE backend server as a RADIUS server to provide AAA for all access requests from the client to the ISE-Frontend server.

Which Cisco ISE configuration must be used?
A.

Set 10.11.1.2 as a network device in ISE-Frontend. Set port 1700/2083 for RADIUS authentication.

B.

Set 10.11.1.1 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

C.

Set 10.11.1.2 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

D.

Set 10.11.1.1 as a network device in ISE-Frontend. Set ports 1700/2083 for RADIUS authentication.

Go to page: